
 Do Son
Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Developer cloud platform Railway suffers a widespread, catastrophic infrastructure outage after Google Cloud abruptly suspends its corporate account.

GitHub confirms a perimeter breach by TeamPCP. An administrative VS Code extension supply-chain worm exfiltrated 3,800 proprietary core source repositories.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.

F5 warns of a critical 9.2 CVSS flaw (CVE-2026-8711) in NGINX JavaScript (njs). Unauthenticated attackers can trigger heap overflows and potential RCE.

At Google I/O 2026, Google launched Wear OS 7. The smartwatch OS replaces old Tiles with dynamic Wear Widgets and opens up wrist-bound Gemini AI agents.

Microsoft releases Azure Linux 4.0 at the Open Source Summit, transforming its custom OS into a full general-purpose VM server distribution based on Fedora.

Microsoft has announced the deprecation of SMS verification codes for consumer accounts, forcing a shift to secure passkeys and biometric authentication.
ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!

At Google I/O 2026, Google launched a $100 AI Ultra tier and shifted its billing model from message limits to a strict, metered Compute-Used matrix.

At Google I/O 2026, Google unveiled Android Halo—a persistent status bar interface coming to Android 17 to subtly track background AI agents.

Google DeepMind skips v4.0 to drop Gemini 3.5 Flash. Running 4x faster than rivals, it powers 24/7 autonomous agents via the new Antigravity framework.

At Google I/O 2026, Google unveiled "Ask YouTube" for natural-language video interrogation alongside "Live" voice-prompting across Gmail, Docs, and Keep.
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
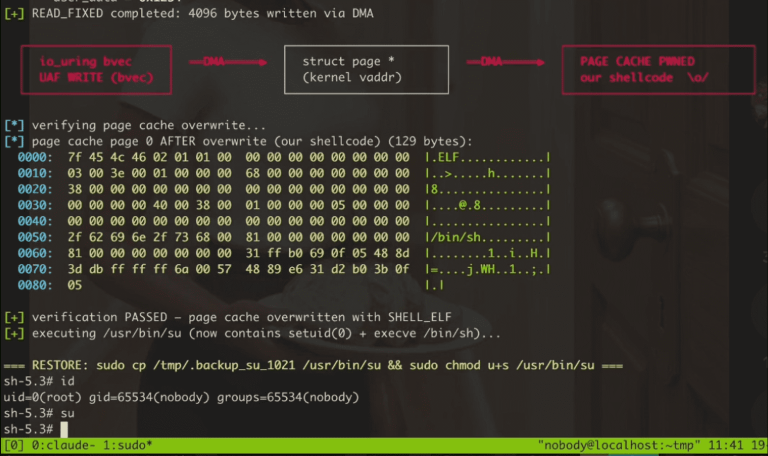
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.
NVIDIA has issued critical security updates for its GPU display drivers and vGPU software to fix a high-severity 8.8 CVSS use-after-free flaw. Patch now!
New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.