
 Do Son
CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

Google Chrome patches 79 vulnerabilities, including 14 "Critical" RCE threats. Update to version 148.0.7778.167 now to protect your data and browser.

Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

Google unveils the Googlebook series powered by AluminumOS. Discover how Intel's x86 architecture is bringing native Android apps to a powerful new desktop.
Update Alert: Windows 11 KB5089549 Triggers Widespread Network Degradation and Installation Failures

Update Alert: Windows 11 KB5089549 Triggers Widespread Network Degradation and Installation Failures
Windows 11 KB5089549 is causing severe network lag and boot-loop installation failures. Learn why IT admins say the latency persists even after uninstallation.

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!

CVE-2026-32661 exploited in the wild. A 9.8 CVSS flaw in GUARDIANWALL MailSuite allows unauthenticated RCE. Apply Canon's official patches immediately.

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!
Urgent: AMD Zen 2 processors (Ryzen/EPYC) hit by CVE-2025-54518. Hardware flaw allows instruction corruption and privilege escalation. Update your BIOS now!

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!
One of the most common sources of confusion among defense contractors preparing for CMMC certification is also...
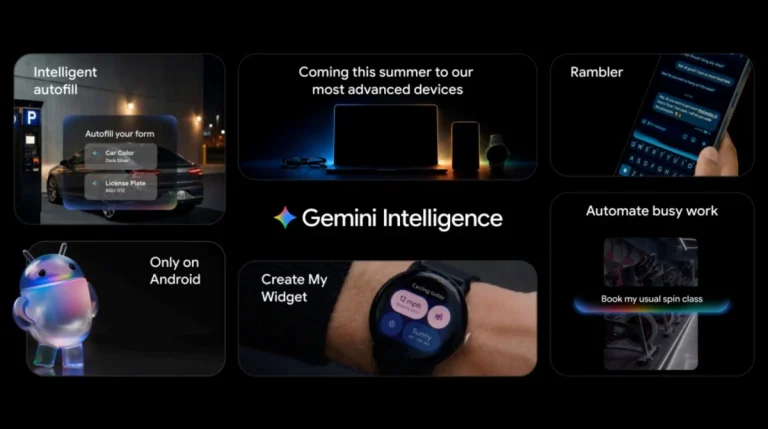
Google transforms Chrome into an "Intelligent Browsing Companion" with Gemini 3.1. Explore Auto Browse, real-time image synthesis, and AI webpage deconstruction.
Google I/O 2026 bombshell: Android 17's Quick Share adds native AirDrop support and a "one-tap" iOS migration tool. See the new Noto 3D emojis and Pause Point.