
 Do Son
Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

OpenAI debuts Workspace Agents: Codex-powered digital laborers that work 24/7 in cloud sandboxes to manage sales, IT audits, and reporting autonomously.

X product lead Nikita Bier debuts Custom Timelines and Snooze Topics. Powered by Grok AI, these Premium-only tools offer 75+ categories for a bespoke feed.

Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.

Linux maintainers propose purging 27,646 lines of legacy network code to combat a flood of AI-generated vulnerability reports and focus on modern security.

OpenAI's new 1.5B Privacy Filter uses semantic reasoning to tag sensitive data locally. Run PII protection on consumer hardware with 128K context support.


ClawCloud Run is shutting down. With free tiers ending May 11, 2026, and a strict refund deadline of May 20, users must migrate data immediately to avoid loss.

Critical 9.8 CVSS auth bypass hits Xiongmai IP cameras. Public PoC is live with NO patch available. Secure your live feeds and isolate your devices now!
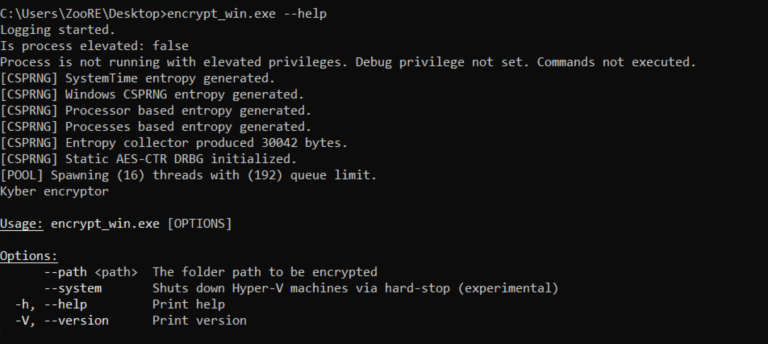
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.

Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.

Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.

Apache HttpClient 5.6 reveals a critical auth flaw (CVE-2026-40542) in SCRAM-SHA-256. Secure your Java microservices—upgrade to 5.6.1 immediately.

Esri issues an urgent fix for critical 9.8 CVSS flaws in ArcGIS. Over-scoped developer credentials could expose GIS data. Patch your portal immediately.
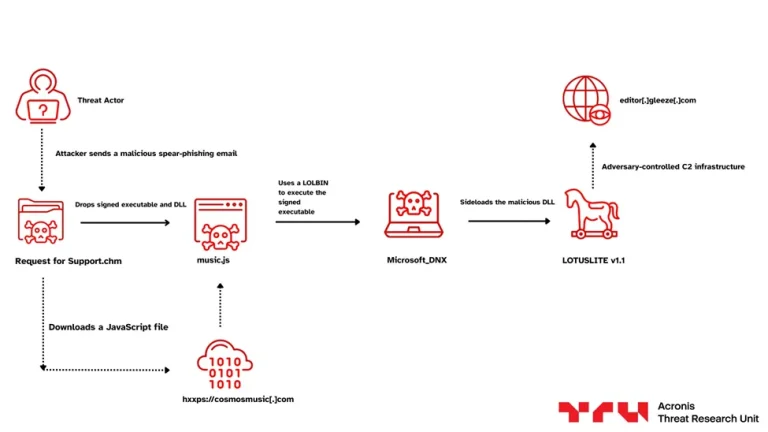
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
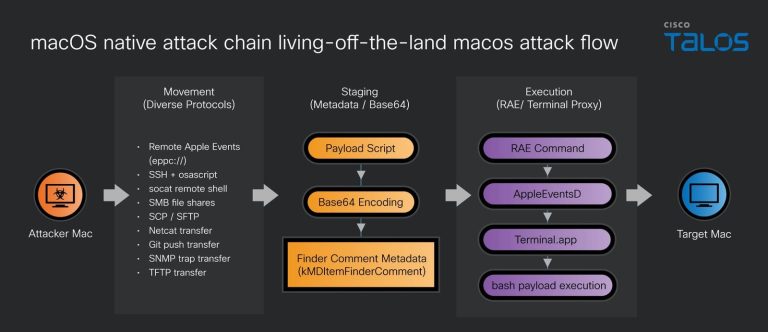
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.