 Do Son
Apache Nutch vulnerabilities include CVE-2026-41870, an unauthenticated remote code execution flaw. See affected versions and fixes.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Two critical Siemens vulnerabilities (CVE-2026-18963, CVE-2026-50093) allow account takeover and root access. See affected versions and fixes.
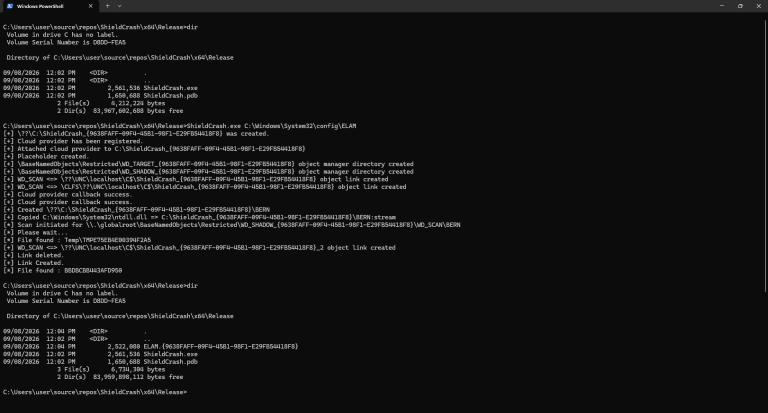
A Windows Defender 0day, CVE-2026-69414, has public PoC exploit code. ShieldCrash reads files as SYSTEM on all supported Windows versions.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
Google patched a Chrome zero-day, CVE-2026-87491, exploited in the wild. Chrome 153 fixes 230 flaws including critical WebGL bugs. Update now.

Unit 42 exposes AI-powered cyberattacks across Latin America, where LLM-assisted actors hit government, water, and financial targets.
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
Microsoft's September 2026 Patch Tuesday fixes two zero-day flaws, CVE-2026-81963 and CVE-2026-85880, both exploited in the wild.
Fortinet fixed three critical Fortinet vulnerabilities. Attackers can exploit CVE-2026-84390 and CVE-2026-26084 to access corporate data.
Microsoft is upgrading Windows 11 performance to ensure faster boot times and fluid experiences for PCs equipped with just 8GB of RAM.
Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.
PyPI file hosting errors caused weeks of 502s. See how a Fastly CDN 502 error was traced to one cache node and fixed by August 28.
Broadcom's unexpected VDDK download removal has severely disrupted VMware migrations. Learn how this impacts Azure and Red Hat enterprise transitions.
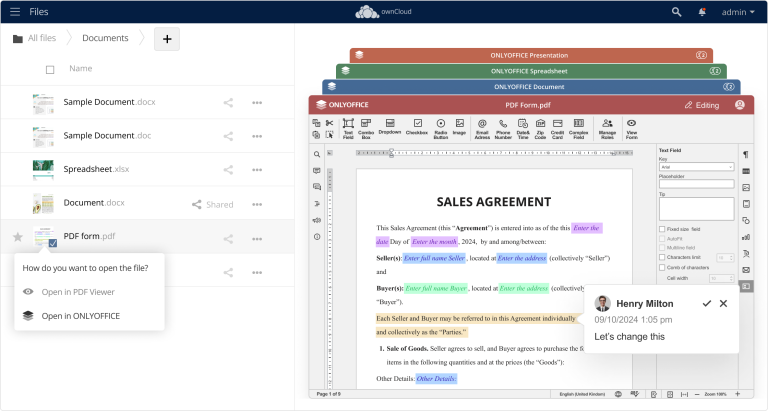
A new ONLYOFFICE ownCloud plugin SSRF vulnerability, tracked as CVE-2026-84282, allows attackers to trigger unauthorized internal network requests.
Ivanti Neurons ITSM RCE: 8 CVEs including unauthenticated code execution flaws (CVSS 9.8-9.9). Patch on-prem deployments now - cloud already fixed.
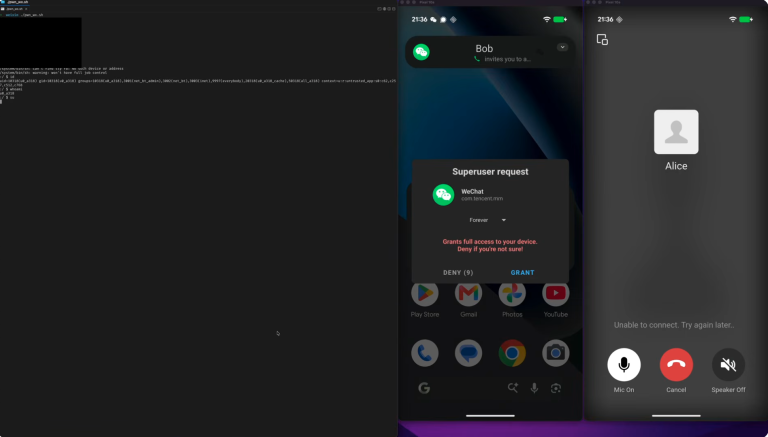
WeWorm is the first zero-click worm to spread via WeChat calls on iOS and Android. Calif researchers found the WeChat RCE flaw - now patched by Tencent.
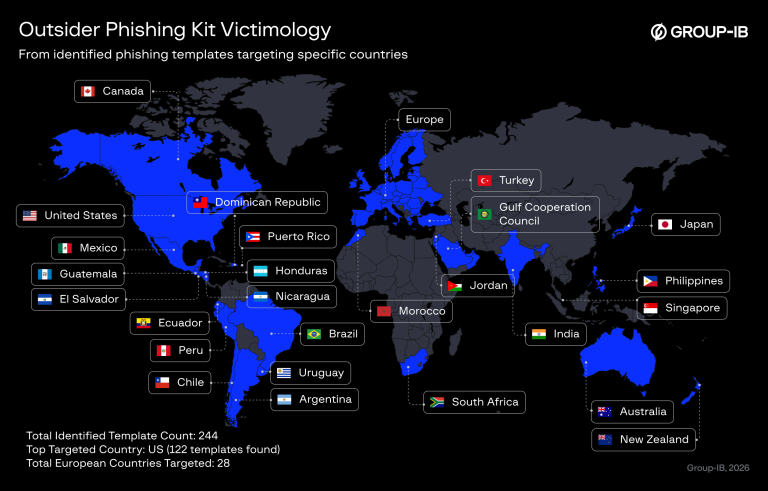
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
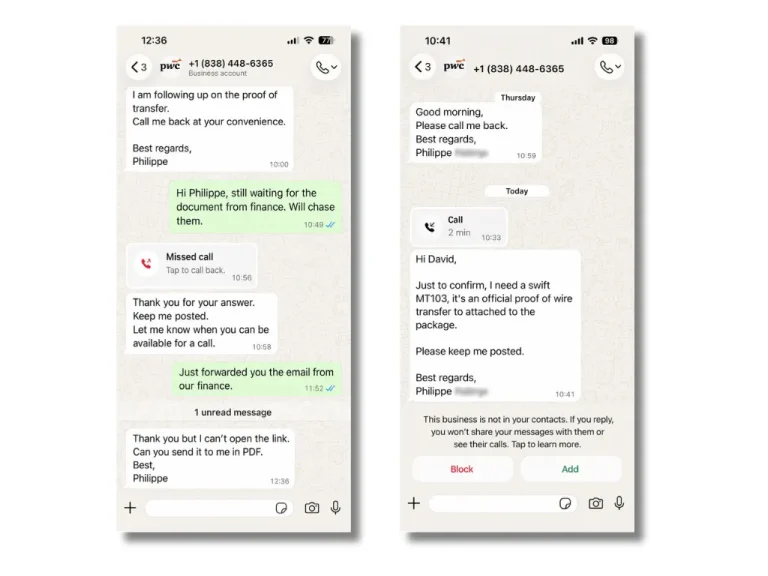
The Phantom Deal campaign uses fake acquisition documents to target executives. Gen exposed the Phantom Deal fraud after tracking bogus payment demands.
The September 2026 SAP Security Patch Day resolves 20 flaws. Apply these SAP Security Patch Day updates to fix CVE-2026-44756 and secure your environment.
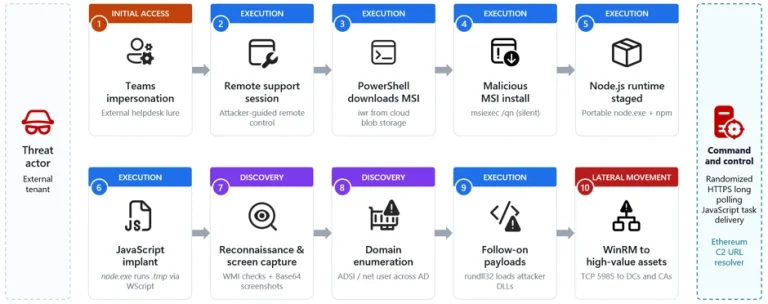
Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.
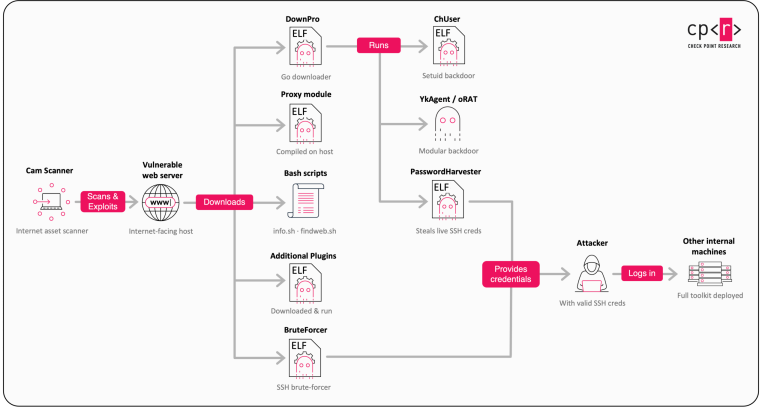
The Gambling Goblin campaign turns Brazilian government websites into an SEO weapon. Suspected Gambling Goblin operators push illicit gambling pages.
An ASUS vulnerability (CVE-2026-19397) lets a nearby attacker take over a host, while an Armoury Crate flaw leaks NTLM hashes. Update now.