 Do Son
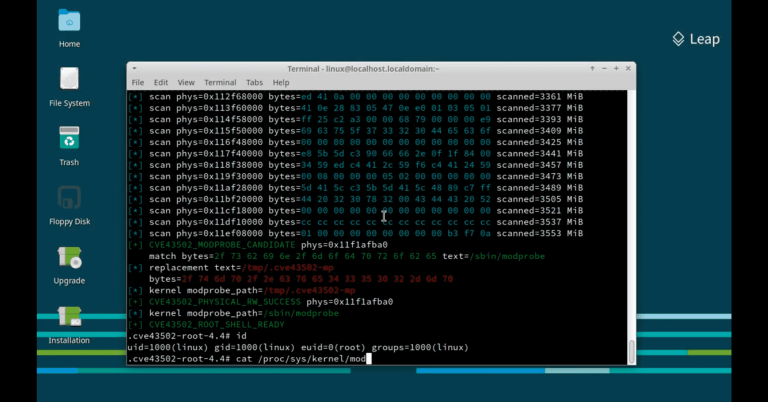
The details and PoC exploit code for the ZcopyReaper Linux vulnerability (CVE-2026-43502) are publicly disclosed, posing a privilege escalation risk.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Discover the details of the Liquid Network hack. A white hat attacker stole 4,000 Bitcoins but returned most of the funds to force a bug bounty payment.
Discover the upcoming Windows 11 battery widget that elegantly displays peripheral power levels and connection statuses directly on your lock screen.
Pegasus spyware infected a Serbian activist through a zero-click iMessage exploit, part of Serbia's largest spyware wave. Update iOS now.
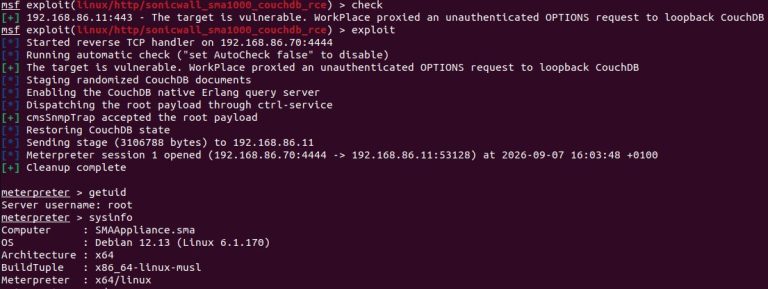
SonicWall SMA 1000 vulnerabilities are exploited in the wild. Public PoC exploit code is disclosed for the critical SonicWall SMA 1000 exploit chain.
JetBrains fixed 29 JetBrains vulnerabilities in Hub and YouTrack. Learn how these critical 9.8 CVSS bugs impact developer servers and how to patch now.
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
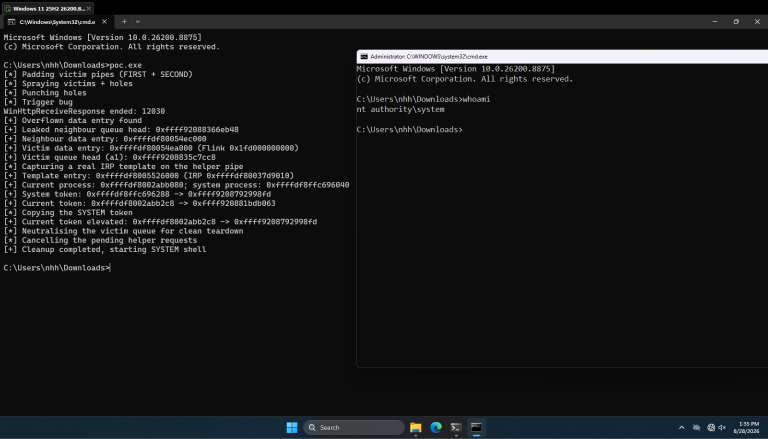
A Windows HTTP.sys vulnerability, CVE-2026-62735 (CVSS 7.8), now has public details and a PoC. It escalates local users to SYSTEM. Patch now.
Python NodeStealer now adds keylogging, clipboard, and screenshot spyware plus dual Telegram C2. See how the NodeStealer spyware upgrade works.
An Adobe Commerce vulnerability, CVE-2026-75650 (CVSS 10), enables unauthenticated arbitrary code execution and is exploited in the wild. Patch now.
A Dell Secure Connect Gateway vulnerability (CVE-2026-80172, CVSS 9.8) grants unauthorized access via forged admin tokens. Patch SCG now.
Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
A Linux PHP web server rootkit targets BIG-IP systems. Learn how this PHP web server rootkit injects in-memory shells into Apache processes.
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
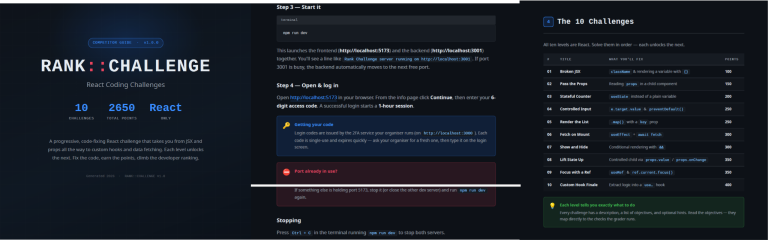
The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
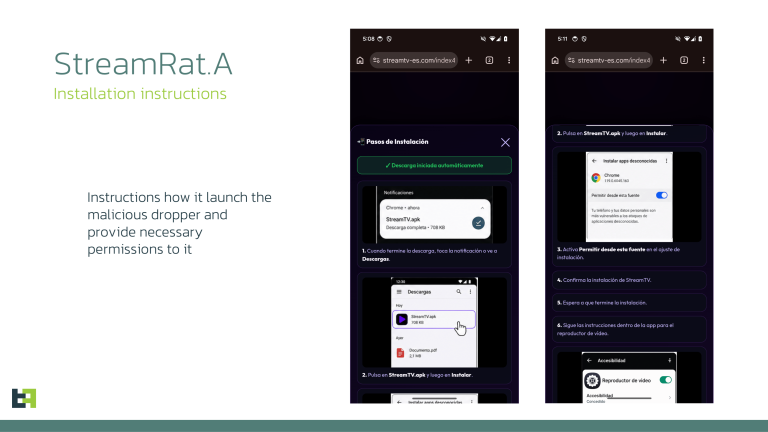
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
Silver Fox fake software installers impersonate Razer and Edge to disable Windows Defender and deploy malware. See how the campaign works.
The MikroTrick PoC is publicly disclosed. This MikroTrick RouterOS flaw is actively exploited in the wild, granting full administrative privileges.
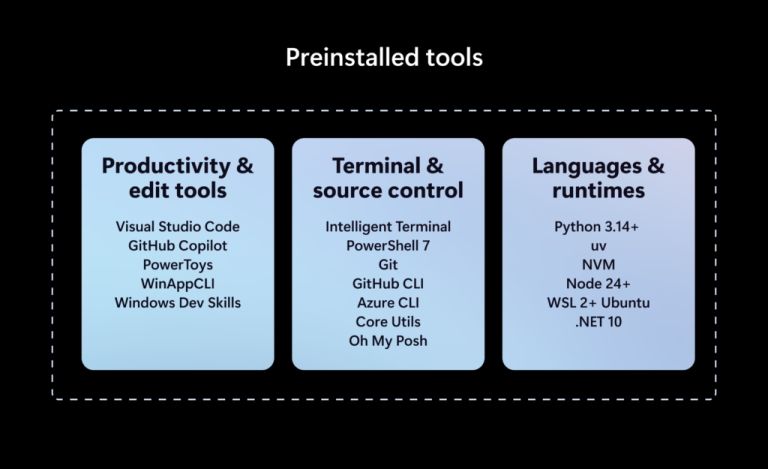
Microsoft Project Zenith is a ready-to-code Windows 11 experience for 64GB+ developer PCs, but a free open-source config offers much the same.
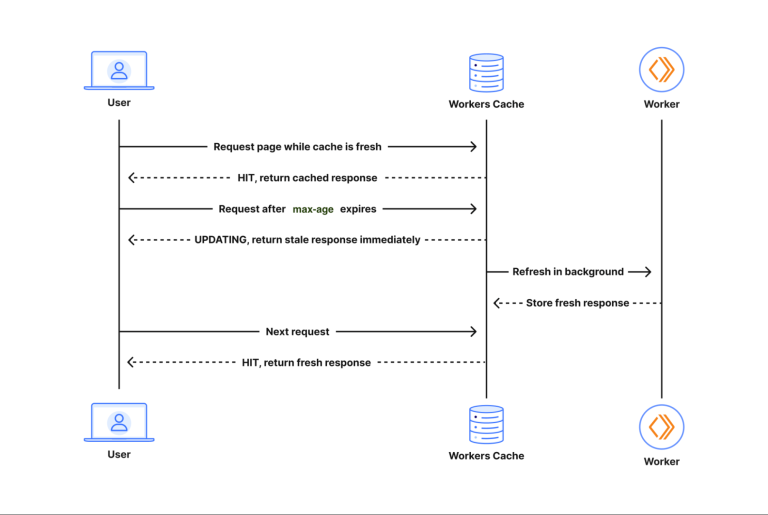
Cloudflare raises the Workers size limit to 64 MiB uncompressed on free and paid plans, replacing the old 3 MB and 10 MB compressed caps.