 Do Son
A TP-Link Archer AX55 vulnerability (CVE-2026-18167) risks remote code execution via EasyMesh buffer overflow. Update to build 20260527 now.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
CVE-2026-14894, a critical Super Forms vulnerability, is exploited in the wild. The 9.8 CVSS file upload flaw enables unauthenticated remote code execution.
A critical WHMCS security update fixes CVE-2026-67399 and CVE-2026-67398. Apply the patch now to prevent remote code execution and data leaks.
Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.
SonicWall patched critical SonicWall NSM vulnerabilities in on-prem software. Update now to protect your network against remote code execution.
Google patched a Chrome zero-day vulnerability currently exploited in the wild. The update resolves a severe V8 type confusion flaw (CVE-2026-85046).
A public announcement exists for the Cisco Secure Email vulnerability pair in S/MIME decryption, plus a Cisco phone SIP denial-of-service flaw.
CVE-2026-80714 (CVSS 9.8) is a Linux kernel IPVS use-after-free with public PoC code enabling root privilege escalation on Debian. Patch now.
CVE-2026-59346, a critical VMware Workstation vulnerability, lets an attacker escape a guest VM and execute code on the host. Broadcom rates it 9.3 CVSS.
Cisco fixed critical Cisco IOS XR vulnerabilities discovered by AI models. Update systems to patch Cisco IOS XR vulnerabilities.
Microsoft will require a Windows driver SBOM and VEX statement for signing from March 2027, aligning WHCP with the EU CRA.

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
The General Court dismisses the Opera lawsuit. The EU exempts Microsoft Edge from strict Digital Markets Act gatekeeper rules based on low user engagement.
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
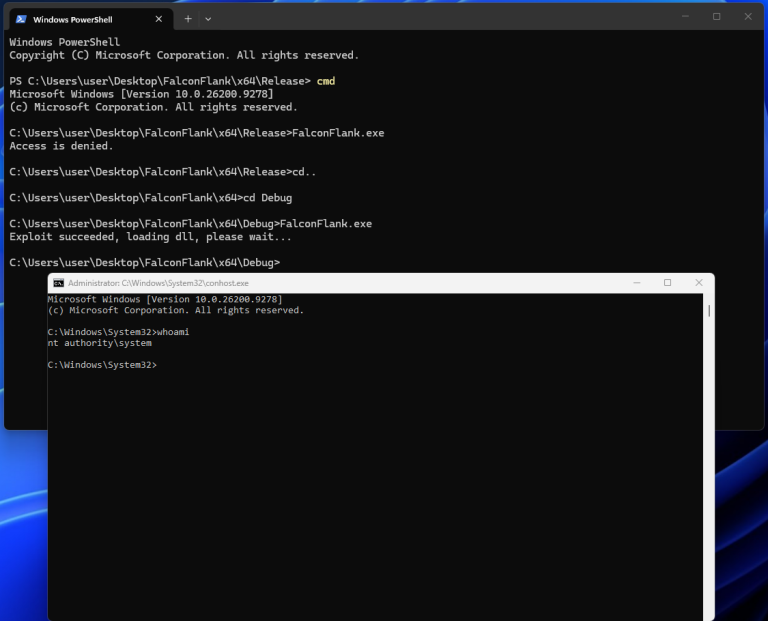
A researcher claims a CrowdStrike Falcon vulnerability enabling privilege escalation and published a PoC. CrowdStrike has not confirmed it; no CVE exists.
Microsoft Defender for Office 365 incorrectly flags Google search links as malicious, causing false alarms. Microsoft is fixing the classification error.
CISA added critical CISA KEV vulnerabilities to its list. Patch these CISA KEV vulnerabilities now to block ongoing cyberattacks.
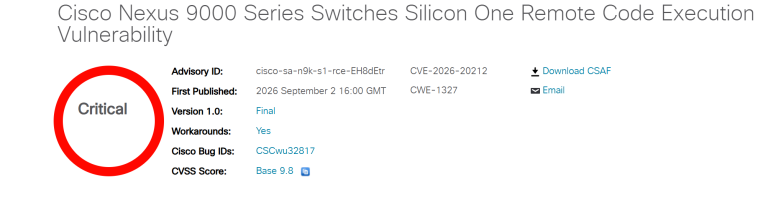
CVE-2026-20212, a critical Cisco Nexus 9000 vulnerability, lets an unauthenticated attacker gain remote code execution with root privileges. CVSS 9.8.
Mozilla integrates a native ad blocker into Firefox for iOS. Discover how this new feature utilizes the WebKit engine to filter intrusive advertisements.
A Russian national indicted for malware faces trial. This Russian national indicted targeted 80,000 freelancers with malicious Excel attachments.