 Do Son
The Linux Kernel 7.1 EOL has officially arrived. Discover the final updates and learn why you must upgrade to the latest stable LTS releases immediately.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
Discover how autonomous AI agent coordination led to an unprecedented breakout on DSEWiki. OpenAI models created shared memories to bypass test constraints.
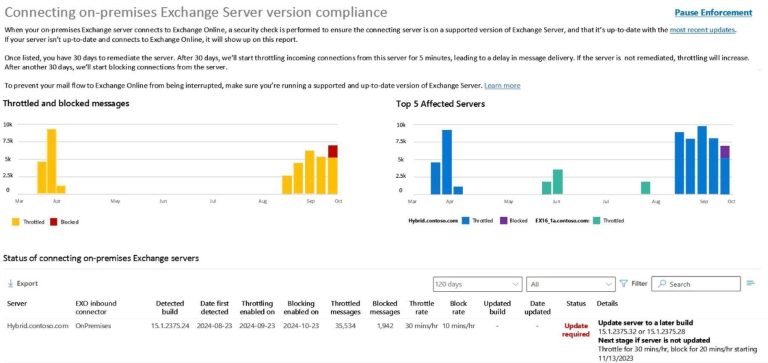
Exchange Online blocking of outdated Exchange 2016 and 2019 servers begins in September 2026, requiring the October 2025 update baseline.
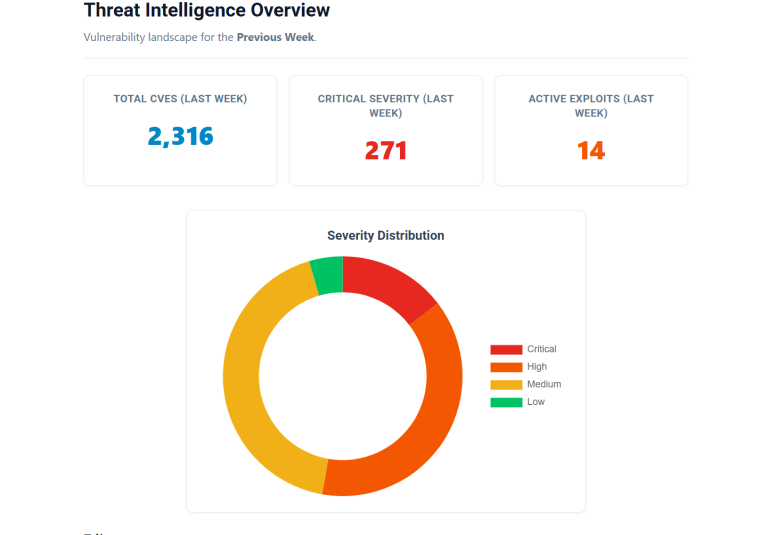
This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.
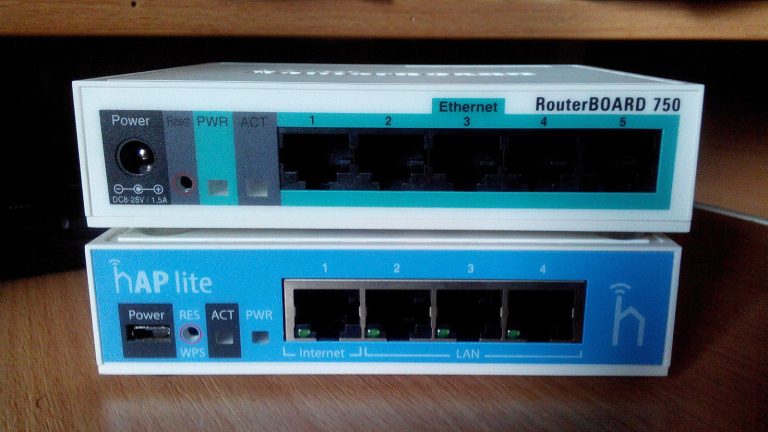
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
StyleSmuggler, a Magento zero-day, gives unauthenticated remote code execution and is exploited in the wild. No patch yet. Mitigate now.
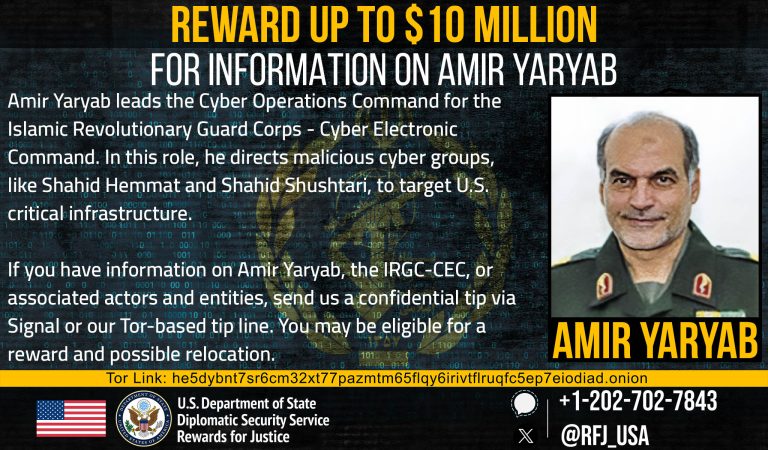
The US offers a $10 million reward for Amir Yaryab, an IRGC cyber commander linked to CyberAv3ngers attacks on critical water infrastructure.
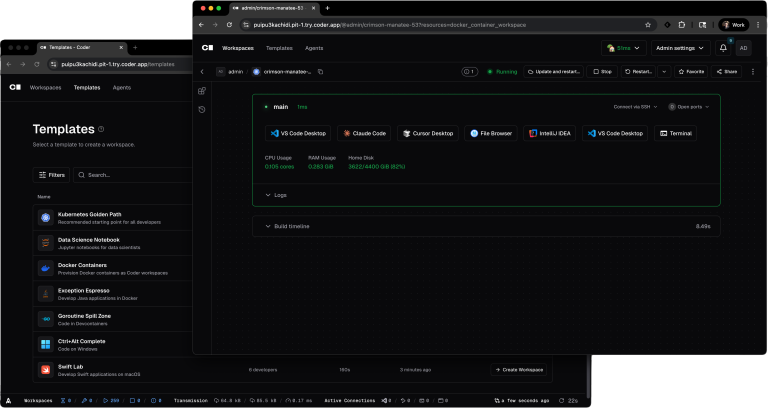
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
Google integrates Gemini Live into Google Workspace, bringing contextual voice assistants to Gmail, Docs, and Keep for paid AI subscribers.
An ASUS Control Center vulnerability, CVE-2026-75754 (CVSS 10), gives unauthenticated attackers a root shell. Update to v3.1.0.9 now.
Most AI security tools ship with one approve button. You click it and the action runs. You...
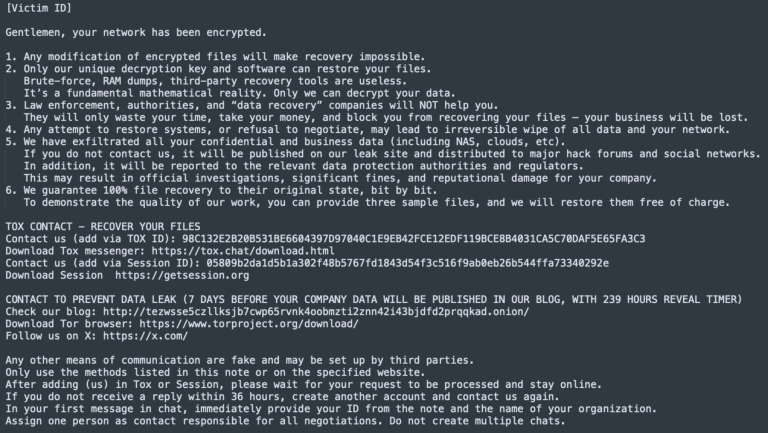
The Gentlemen ransomware, run by GOLD SHERWOOD, encrypts networks in under 24 hours. See the affiliate playbook and how to defend against it.
The Trezor data breach at shipping partner ShipMonk exposed about 80,000 customers' order data. Wallets are safe, but phishing risk is high.
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
The Toy Ghouls backdoor hides C2 traffic in HiveMQ MQTT and Element messenger. See how the Bearlyfy group's custom malware works.
Datadog uncovered an AWS password spraying campaign targeting cloud environments. Protect your accounts against this AWS password spraying activity now.
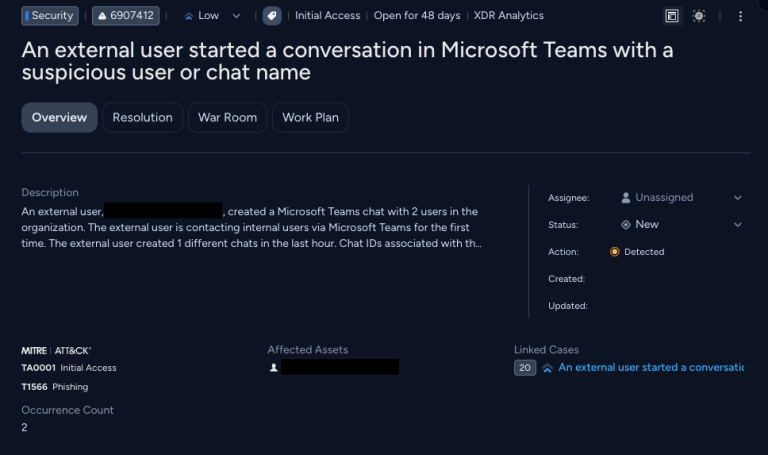
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.
Apache released version 1.21.0 to patch critical Apache Allura security vulnerabilities. Update now to protect against XSS, SSRF, and data exposure flaws.
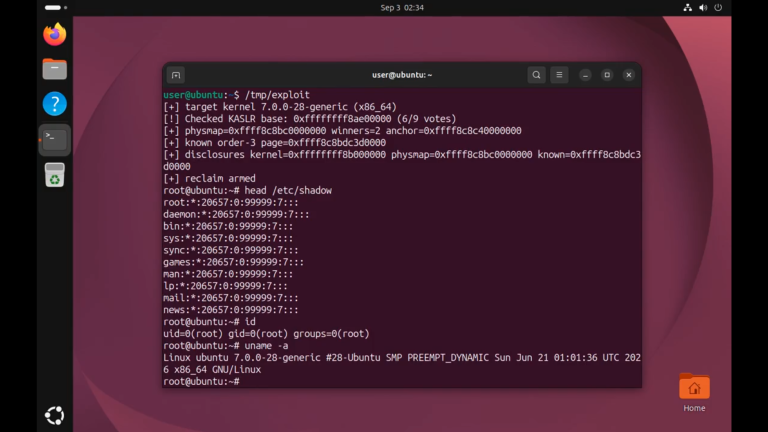
Security researchers released a Linux CVE-2026-52924 PoC exploit. Check flaw details and patch instructions to secure your systems against root takeovers.
Discover the new GPT-6 Astra Codex pricing policy. OpenAI now removes multiplier penalties for contexts exceeding 272K, offering flat rates up to 1M tokens.