
 Do Son
CVE-2024-30299 impacts Adobe FrameMaker Publishing Server and is rated with a critical CVSSv3.1 base score of 10.0
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

ASEC has published a report detailing a significant shift in the tactics employed by the Bondnet threat actor

The Black Basta ransomware group may have exploited a previously unknown vulnerability (CVE-2024-26169) in Windows Error Reporting Service

A security researcher has published a PoC exploit code for a CVE-2024-27801 vulnerability affecting multiple Apple platforms

Videolan, the organization behind the popular VLC media player, has released urgent security updates to address two critical vulnerabilities

SuiteCRM has released urgent security patches to address multiple critical vulnerabilities that could expose sensitive customer data and compromise system integrity

Cybersecurity researchers at Trend Micro have unveiled a previously undocumented backdoor malware dubbed "Noodle RAT,"

CVE-2024-35241 and CVE-2024-35242, both involve command injection attacks through malicious git/hg branch names

Schneider Electric has released a critical security patch to address multiple vulnerabilities in its SAGE Remote Terminal Unit (RTU) devices

Veeam, a prominent backup and disaster recovery solutions provider, has recently addressed a critical vulnerability (CVE-2024-29855)

This vulnerability is currently being actively exploited by malicious actors in a widespread ransomware campaign known as "TellYouThePass."

A high-severity vulnerability (CVE-2024-5585) has been identified in multiple versions of PHP, the widely used server-side scripting language

Researchers have demonstrated that teams of AI agents, powered by large language models, can successfully exploit zero-day vulnerabilities

IBM X-Force Red, a team of cybersecurity researchers, has uncovered critical vulnerabilities in Precor smart treadmills

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

CVE-2024-5452 enables attackers to remotely manipulate the entire application state, potentially leading to complete system takeover

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education

A newly released proof-of-concept (PoC) exploit has heightened concerns about a critical vulnerability (CVE-2024-29849)

A security researcher has published a proof-of-concept (PoC) exploit code targeting a recent important severity vulnerability (CVE-2024-30043)

A surge in cyber activity associated with the Sticky Werewolf group, a threat actor with suspected geopolitical or hacktivist ties
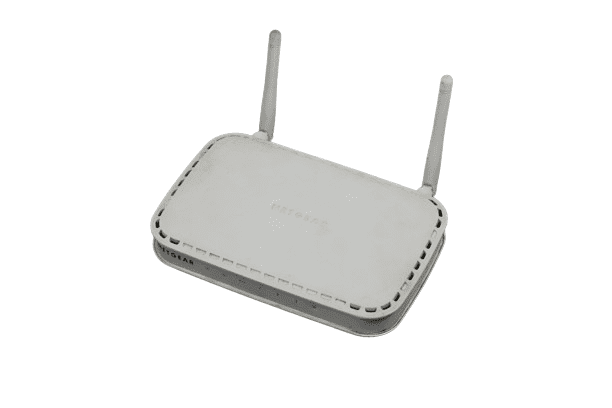
A series of critical vulnerabilities in the popular Netgear WNR614 N300 router, exposing users to significant security risks

A new variant of an ongoing cryptojacking campaign targeting misconfigured Kubernetes clusters has been uncovered