
 Do Son
Kali Linux, the renowned open-source, Debian-based Linux distribution, has officially released its latest version, Kali Linux 2024.2
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

Parrot OS 6.1 brings a slew of improvements and upgrades designed to bolster system performance, stability, and security
In a recent wave of cyberattacks, TikTok has confirmed a zero-day vulnerability within its direct messaging system has been exploited
Security researcher published the technical details and a proof-of-concept (PoC) code for a vulnerability, identified as CVE-2023-3390
CVE-2024-36522 discovered in earlier versions of Apache Wicket, stemmed from a potential XSLT injection attack, enabling malicious actors to RCE
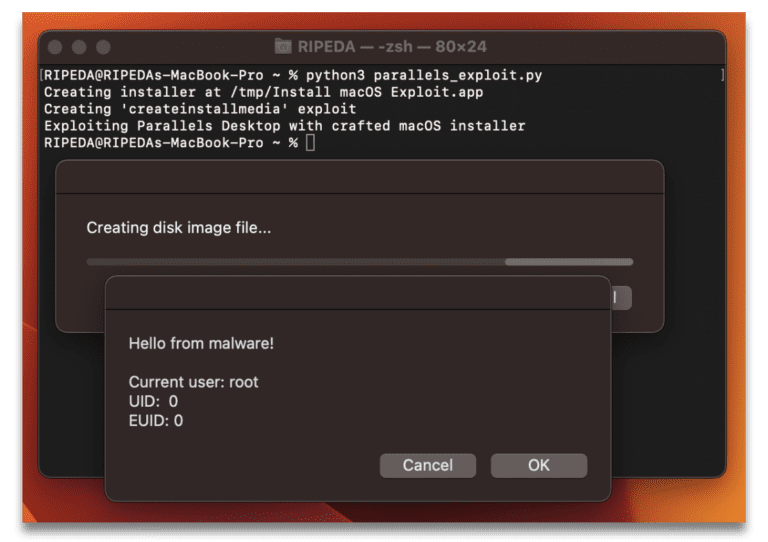
The technical details and a proof-of-concept (PoC) exploit code for a vulnerability (CVE-2024-34331) in Parallels Desktop for Mac

UNC1151 employed DLL loaders that downloaded an encrypted JPG file, which was then decrypted to deploy a final payload executable.
Successful exploitation of the CVE-2024-4332 vulnerability could lead to unauthorized information disclosure or modification

Security researcher Zeyad Azima has recently published a proof-of-concept exploit code for the CVE-2024-27348 vulnerability

Tenable Research has uncovered a significant vulnerability within Microsoft Azure's Service Tags functionality

Due to the critical severity of vulnerabilities CVE-2024-29972, CVE-2024-29973, and CVE-2024-29974, Zyxel has made patches available

A security researcher has published details and proof-of-concept (PoC) code for a macOS CVE-2024-27822 vulnerability

CVE-2024-21512 stems from a Prototype Pollution vulnerability that could be exploited for remote code execution.
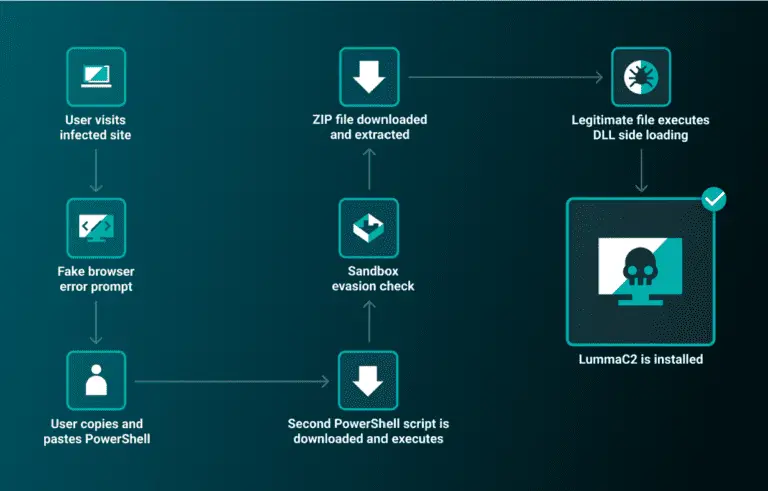
The ReliaQuest Threat Research Team has unveiled a new execution technique used in the ongoing ClearFake campaign

Tracked as CVE-2024-3584, this flaw carries a near-perfect CVSS score of 9.8, underscoring the potential for severe exploitation.

This multi-stage malware strategy ultimately delivers the notorious "Cobalt Strike" payload, establishing communication with a C2 server

The identified flaw, cataloged as CVE-2024-5404 with a CVSS score of 9.8, affects the "Forgot Password" function of the Moneo IIoT platform

WordPress, the world's most popular CMS, is facing a wave of targeted attacks exploiting critical vulnerabilities in several plugins

CVE-2024-36104 could allow remote attackers to execute arbitrary code on affected systems, potentially leading to full system compromise

A significant security vulnerability has been uncovered in the widely-used node-ip npm package, which is designed to...

Censys observed 13,802 internet hosts exposing either a CloudGuard instance, Quantum Security, or Quantum Spark gateway