 Do Son
CVE-2024-0087, rated with a critical CVSS score of 9.0, allows attackers to exploit Triton Server's log configuration interface to write arbitrary files
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

SocGholish, a sophisticated JavaScript malware framework, has been a persistent threat since its emergence in 2017.

The French National Cybersecurity Agency (ANSSI) has issued a warning about the continued activity of the Nobelium intrusion set

The perpetrators, utilizing tools linked to various Chinese espionage groups, have successfully penetrated these telecom networks

Fortra has issued a security advisory warning users of a high-severity flaw (CVE-2024-5275) in both FileCatalyst Direct and FileCatalyst Workflow

CVE-2024-28995 is a path-traversal vulnerability that allows unauthenticated attackers to retrieve arbitrary files from the filesystem

UNC3886 exploited a now-patched vulnerability in FortiOS, alongside a custom malware ecosystem targeting Fortinet devices

DataDog Security Labs has uncovered a concerning campaign targeting Amazon Web Services (AWS) environments
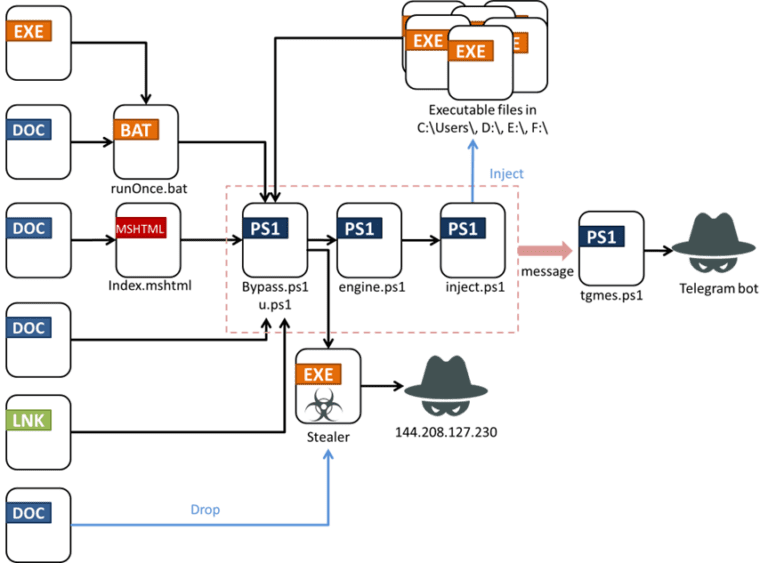
Fickle Stealer executes several scripts designed to bypass User Account Control (UAC) and prepare the environment for the main payload

CVE-2023-32191 (CVSS 10) poses a severe risk to the security and integrity of Kubernetes clusters managed by RKE

Cybersecurity researchers at Avast have unearthed a new and previously undetected variant of the Diamorphine Linux kernel rootkit

CVE-2024-5671 and CVE-2024-5731 leave unprotected systems vulnerable to remote code execution and unauthorized access

As QR code phishing attacks continue to evolve, individuals and organizations must remain vigilant. Cybersecurity awareness is key

EclecticIQ analysts have recently discovered a sophisticated PhaaS platform called ONNX Store, targeting financial institutions worldwide

Rapid7, a cybersecurity firm, has uncovered a recent malvertising campaign using fake software installers to distribute the Oyster backdoor

The first set of vulnerabilities, identified as CVE-2024-37079 and CVE-2024-37080, are classified as heap-overflow vulnerabilities

The CVE-2024-37902 vulnerability stems from how DJL handles archived artifacts, which are collections of files used in deep learning models

Taiwan's CERT has issued a critical security warning regarding a severe flaw (CVE-2024-6047) affecting various end-of-life GeoVision devices

CVE-2024-38457 and CVE-2024-38458 could enable malicious actors to take control of affected servers or inject harmful scripts

Cisco Talos has published a comprehensive report detailing a long-running cyber espionage campaign dubbed "Operation Celestial Force."

The vulnerabilities, assigned CVEs 2024-35304 through 2024-35307, affect Pandora FMS versions 700 to 776 and have received high CVSS scores

This new method has been employed by threat actors such as TA571 and the ClearFake cluster, targeting users with malware including DarkGate