
 Do Son
UAC-0184, leverages sophisticated techniques like DLL sideloading and the use of Python-related files to deliver the notorious XWorm RAT
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

CVE-2024-4196 and CVE-2024-4197, have been identified and could potentially allow remote attackers to gain full control of affected systems

ReversingLabs researchers have uncovered a malicious package named "legacyreact-aws-s3-typescript" on the npm registry

The most severe of these vulnerabilities, CVE-2024-5988 and CVE-2024-5989, have been assigned a CVSS score of 9.8

DBatLoader is being actively distributed via phishing emails, with the malware now packaged in compressed CMD files

Canonical’s new ‘Everything LTS’ initiative expands Ubuntu Pro by integrating thousands of new open source components

CVE-2024-5655 allows attackers to trigger pipelines as another user under specific conditions, posing a significant security risk
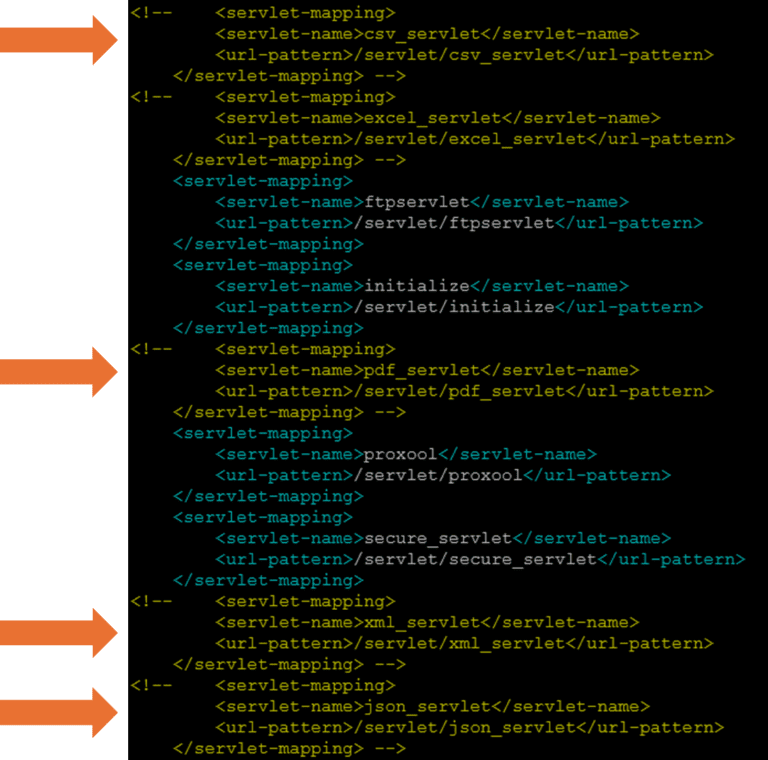
Tenable Research, who discovered and reported the CVE-2024-5276 flaw, has released a proof-of-concept (PoC) exploit code

"8220" mining gang, dubbed "k4spreader," represents a significant evolution in their arsenal, combining advanced persistence mechanisms

These security flaws, impacting GeoSolutionsGroup, the Linux Kernel, and Roundcube Webmail are now under active exploitation.

CVE-2024-38373 has been discovered in FreeRTOS-Plus-TCP, a popular TCP/IP stack widely used in Internet of Things (IoT) devices

Progress has issued a dire warning to all users of its WhatsUp Gold network monitoring software, revealing a series of severe vulnerabilities

SpyMax's attack strategy begins with a seemingly harmless phishing image that cleverly mimics the official Telegram app.

A security researcher has published a proof-of-concept (PoC) exploit code targeting a recent high-severity vulnerability (CVE-2024-30088) in...

The publication of CVE-2024-5806 vulnerability details and (PoC) exploit code on June 25, 2024, has led to immediate exploitation attempts

Singapore's digital landscape is facing a mounting threat as cybercriminals exploit stolen digital identities of its citizens on the Dark Web

With a CVSS score of 9.1, the CVE-2024-5805 vulnerability enables attackers to bypass SFTP authentication mechanisms

A critical vulnerability tracked as CVE-2024-5488 has been discovered in SEOPress, a popular WordPress plugin with over 300,000 active installations
A new and sophisticated cyber attack campaign has surfaced, leveraging a weaponized Microsoft Word document to deliver the notorious Remcos RAT

Upon activation, StrelaStealer methodically scans the compromised system, first targeting Thunderbird email clients.

WordPress has released a critical security update to address three vulnerabilities that could potentially expose millions of websites to cyber attacks

the technical details and PoC exploit code for a vulnerability in the Bluetooth Low Energy library in Windows, designated as CVE-2023-24871