
 Do Son
The KDE development team has issued a critical security advisory warning users of a high-severity vulnerability (CVE-2024-36041)
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

The vulnerability, identified as CVE-2024-6376, stems from insufficient sandbox protection settings within the ejson shell parser

Cloudflare's popular 1.1.1.1 public DNS resolver service experienced disruptions, leaving a small percentage of users worldwide unable to access the service

To mitigate the risk posed by CVE-2024-39943, users of HFS are strongly advised to update their software to version 0.52.10 or later

Apache HTTP Server version 2.4.61, a crucial update that addresses a severe source code disclosure vulnerability (CVE-2024-39884)

The attack involves the distribution of trojanized versions of jQuery through dozens of packages on the npm repository

A high-severity vulnerability (CVE-2024-38513) has been discovered in Fiber, a widely-used web framework for the Go programming language

An analysis detailing the advanced evasion techniques employed by GootLoader, a pervasive malware known for its role in delivering ransomware

An attacker can first bypass authentication using CVE-2024-5716 and then leverage CVE-2024-5717 to execute arbitrary code

A new wave of cyberattacks utilizing the sophisticated Mekotio banking trojan is raising alarms across Latin America

The OpenStack Foundation has issued an urgent security advisory, disclosing a critical vulnerability (CVE-2024-32498)

Victims whose files have been encrypted by the Mallox ransomware Linux variant may be able to recover their data using the decryptors

Security researchers from Graz University of Technology have unveiled a novel cybersecurity threat dubbed "SnailLoad" (CVE-2024-39920)
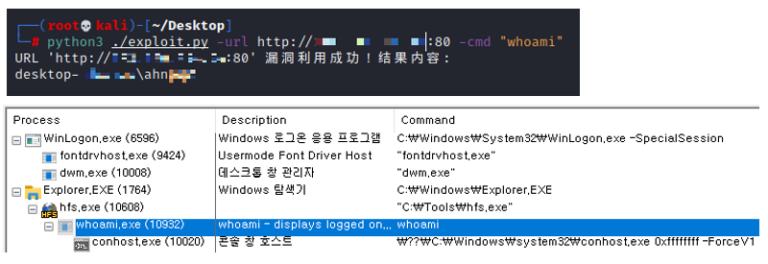
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

Adding to the urgency, security researcher carsonchan12345 has published a proof-of-concept (PoC) exploit code for CVE-2024-37726

The team has observed a surge in malicious PDF files distributed via email, which contain embedded QR codes

SonarSource, a leading code security firm, has uncovered four unpatched vulnerabilities in Gogs, a popular open-source self-hosted Git service

CVE-2024-21586 (CVSSv4 8.7), allows unauthenticated attackers to remotely crash the Packet Forwarding Engine (PFE) and cause a DoS condition

A severe security flaw, CVE-2024-36401 (CVSS 9.8), has been discovered in GeoServer, a widely-used open-source software platform

Nearly three years after the notorious ProxyLogon and ProxyShell vulnerabilities caused widespread havoc on Microsoft Exchange servers

CVE-2024-6172 has been assigned a near-maximum CVSS score of 9.8, underscoring its critical nature & potential impact on the over 90,000 websites

Google released the July 2024 security patches for the Android operating system, which address several critical vulnerabilities