
 Do Son
CVE-2024-6235 and CVE-2024-6236 could allow unauthorized access to sensitive information and even cause denial-of-service (DoS) attacks
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

OpenVPN, a leading provider of virtual private network solutions, has refuted claims of zero-day vulnerabilities in its OpenVPN2 software

According to the ImmuneFi Severity Classification System, the severity of CVE-2024-39696 has been classified as Critical

Despite the critical nature of CVE-2023-46685, LevelOne has declined to patch the vulnerability in their software.

A new, insidious phishing scam impersonating India's RTO has been detected, preying on unsuspecting Android users via WhatsApp

Cybersecurity researchers at Morphisec have discovered a critical zero-click remote code execution (RCE) vulnerability, CVE-2024-38021

This zero-day vulnerability, designated CVE-2024-38112, has been addressed by Microsoft in its July 2024 Patch Tuesday update

CVE-2024-6409, has been found to expose systems to potential remote code execution (RCE) due to a race condition in signal handling

A PoC exploit has been released, targeting a recently patched high-severity vulnerability (CVE-2024-22274) in the VMware vCenter Server

The most severe vulnerability, CVE-2024-36138, is a bypass of an incomplete fix for a previous issue, CVE-2024-27980

Apache Software Foundation has issued an urgent security advisory, disclosing two critical vulnerabilities (CVE-2024-38346 and CVE-2024-39864)

This includes the use of LNK files, MSbuild for loading the fileless backdoor, and novel methods for disabling event logging

A severe vulnerability (CVE-2024-5441) has been discovered in the widely used WordPress plugin Modern Events Calendar
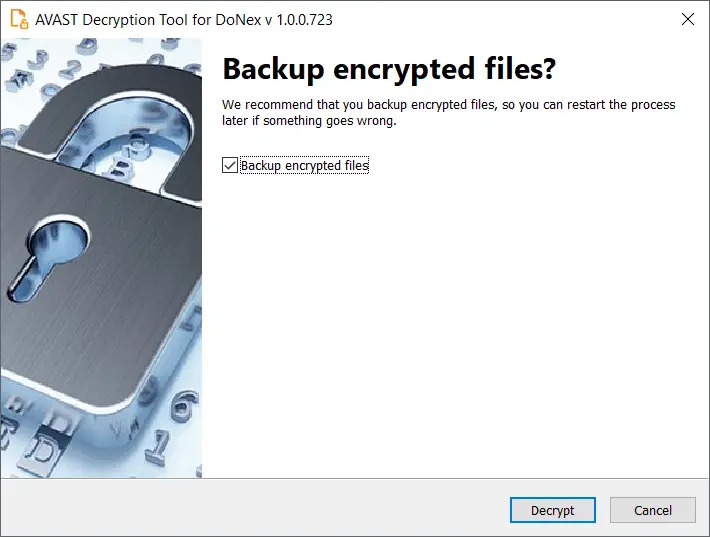
The free DoNex ransomware decryptor tool, now available to the public, is user-friendly and guides victims through the decryption process
Hardware manufacturer ZOTAC faced a significant security lapse that compromised sensitive customer information

Cisco has issued a critical security advisory, warning users of a high-severity vulnerability (CVE-2024-6387) codenamed "regreSSHion"

The most severe vulnerability (CVE-2024-39349) was a classic buffer overflow in the libjansson component, which could enable RCE

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

CRIL has revealed a surge in cyberattacks exploiting the patched Microsoft Defender SmartScreen vulnerability (CVE-2024-21412)

CVE-2024-6209 and CVE-2024-6298, pose a significant risk to organizations utilizing ASPECT for optimizing energy consumption in buildings

The AhnLab Security Intelligence Center (ASEC) has issued a warning about a new backdoor malware called HappyDoor

Trend Micro, a global leader in cybersecurity, has issued a warning about a recent wave of attacks targeting misconfigured Jenkins servers