
 Do Son
CVE-2024-38472 (Important): Server-Side Request Forgery (SSRF) vulnerability on Windows systems, potentially leaking sensitive NTML hashes
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

A security researcher has published a PoC exploit code targeting a high-severity CVE-2024-1085 vulnerability in the Linux kernel

McPhail has identified a critical vulnerability (CVE-2024-1724) in Snap, a popular package manager for Ubuntu and other Linux distributions
CVE-2024-3330 stems from insufficient input validation, allowing low-privileged attackers with read/write access to craft malicious Analyst files
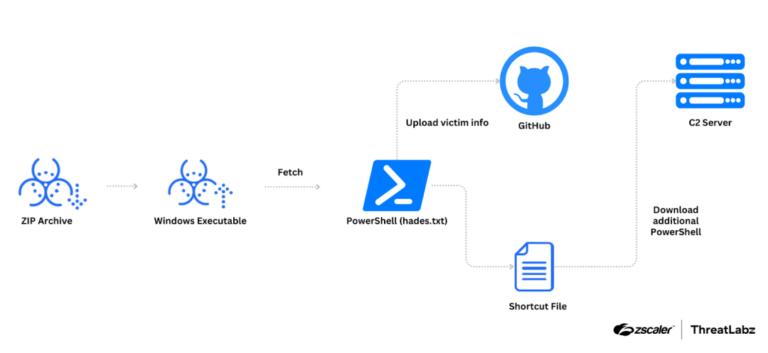
The group is deploying a malicious Google Chrome extension called "TRANSLATEXT" to steal sensitive information from South Korean academics

CVE-2024-20399 has been discovered in Cisco NX-OS Software, the operating system powering a wide range of Cisco's networking devices

TRU has detailed a CVE-2024-6387 flaw, dubbed 'regreSSHion,' that leaves millions of Linux systems vulnerable to remote code execution

Chrome 127 and all subsequent versions will no longer trust newly issued digital certificates from the U.S private software company, Entrust

A security researcher has released PoC exploit code targeting a high-severity vulnerability (CVE-2024-0193) within the Linux kernel

The Document Foundation has issued an urgent security advisory regarding a critical flaw (CVE-2024-5261) in its LibreOfficeKit component

Dubbed "Indirector" attacks, exploit weaknesses in the chip's branch prediction mechanisms to precisely manipulate program execution flow

Water Sigbin employs various techniques, including creating scheduled tasks, adding exclusions to Windows Defender

This vulnerability is not a flaw in the DTLS protocol itself but in its implementation within certain WebRTC media servers

threat actors are increasingly exploiting publicly available Cobalt Strike profiles to mask their malicious activities and bypass security measures
Microsoft has announced a new practice of assigning CVE numbers for significant vulnerabilities found and fixed within their cloud services

this new strain, referred to as "InnoLoader," creates a unique malware instance each time a download request is made

CVE-2024-36072: An unauthenticated attacker could exploit a flaw in the logging component to execute system commands with root privileges

MerkSpy Spyware can silently record keystrokes, capture screenshots, and even steal login credentials from popular web browsers like Chrome

TeamViewer, a remote control tool trusted by millions of users globally, has disclosed a significant cyberattack.

Rapid7 has uncovered a sophisticated supply chain attack targeting users of well-known Windows software tools Notezilla, RecentX, & Copywhiz

Juniper Networks disclosed a critical vulnerability identified as CVE-2024-2973, which has earned a severity rating of 10 on the CVSS scale

A vulnerability has been discovered in TP-Link VIGI NVR4032H network video recorder, a device widely used in surveillance systems