 Do Son
CVE-2026-16347 lets attackers brute-force MikroTik RouterOS logins for unauthorized system access. Rated CVSS 8.8, with no fix yet. Apply mitigations.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
The Arris BGW210-700 vulnerability, CVE-2026-16771, is an authentication bypass in AT&T's gateway. A LAN user can read the WiFi password.
Four OpenAM vulnerabilities are fixed in 16.1.2. CVE-2026-62379 (CVSS 9.8) allows unauthenticated remote code execution; CVE-2026-62261 scores 9.9.
Five Erlang/OTP vulnerabilities include a critical TLS certificate bypass and several remote crash flaws. Update to the patched OTP releases now.
There is a category of vulnerability that almost every automated security tool is structurally incapable of finding,...
A CodeIgniter4 RCE vulnerability, CVE-2026-63223 (CVSS 9.8), enables remote code execution via file upload. Patch to v4.7.4 to fix four flaws.

Discover how AI driven cyberattacks have become the most lethal weapon for hackers in 2026, increasing breach costs and targeting critical infrastructure.
A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.
Public PoC exploits a GitLab RCE built from two Oj memory corruption bugs. See affected versions and patched GitLab releases to install now.

Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.
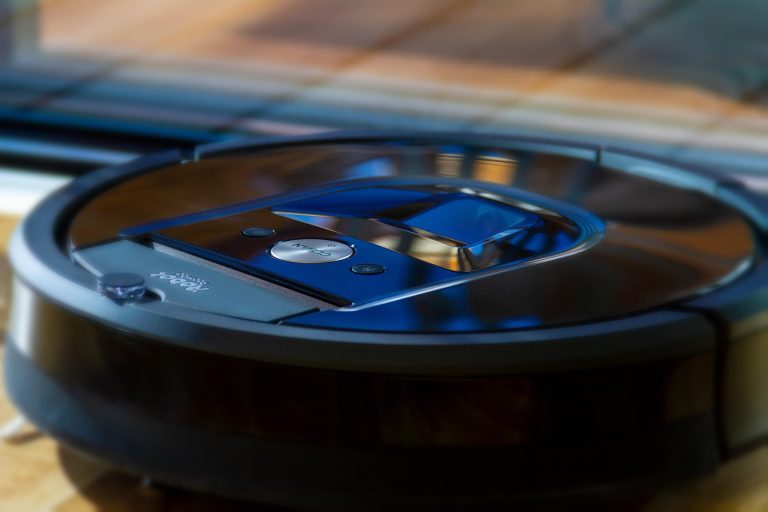
The FCC has banned the import and sale of new foreign-made robot vacuums in the US, citing broad definitions of advanced robotic devices and national security.
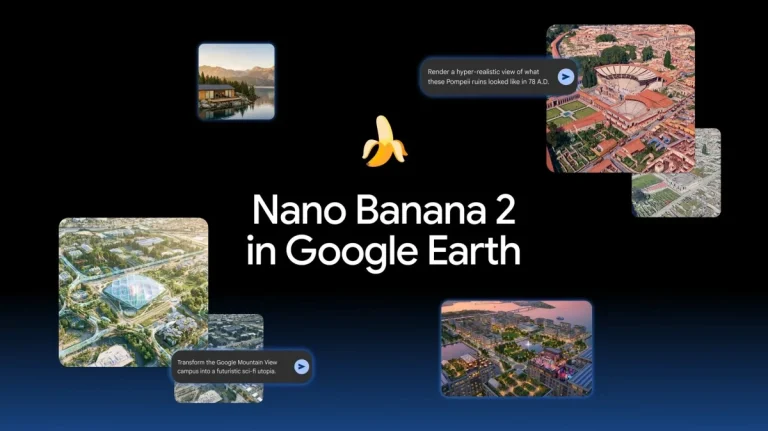
Google integrates its Nano Banana 2 AI image generator into Google Earth, allowing users to visualize historical scenes and future real estate projects.
A SolarWinds Web Help Desk SAML authentication bypass, CVE-2026-28323, scores a critical CVSS 9.8. Update to 2026.2.1 to stay protected.
Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
MicroLogix 1400 attacks hit internet-exposed PLCs at water utilities, locking out operators. Rockwell shares recovery and hardening steps.
Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.
A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.
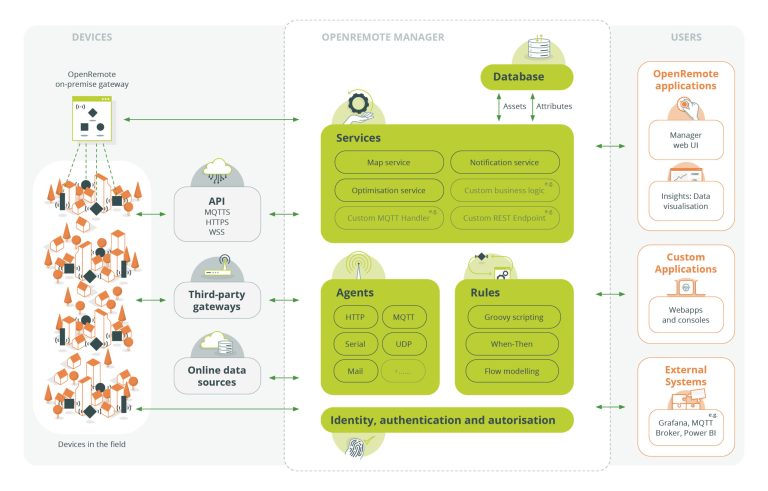
An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.
Four IBM WebSphere vulnerabilities are fixed, including a 9.8 pre-auth RCE (CVE-2026-14512) and a 9.4 SSRF (CVE-2026-14529). Patch now.
MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.
A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.
A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.