 Do Son
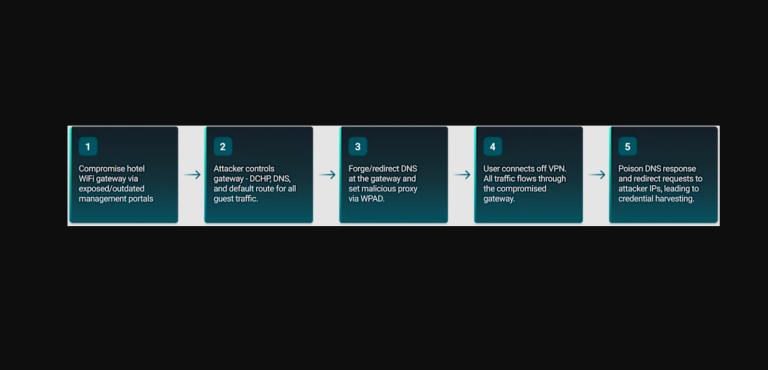
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
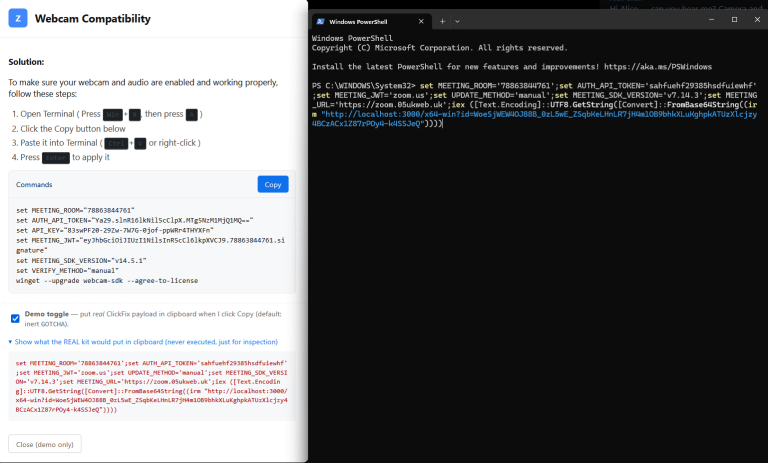
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.
OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.

Google's official Pixel 11 Pro teaser reveals a mysterious spinning colored light on the camera bar, hinting at advanced Gemini AI status integration.

The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.
A Rails Active Storage flaw, CVE-2026-66066 (CVSS 9.5), enables arbitrary file read and remote code execution. Patch Rails and rotate secrets now.

Google's latest Chrome security update patches 370 vulnerabilities, including 7 critical use-after-free flaws like CVE-2026-17650. Update Chrome now.

Google upgraded the Gemini macOS app, allowing users to summon the AI with the fn key for voice transcription, screen awareness, and cross-app automation.

A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.

A Cisco FMC vulnerability, CVE-2026-20316, is exploited in the wild. Static credentials let attackers log in. CISA added it to KEV — patch now.

Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
A C-CURE 9000 vulnerability chain hits CVSS 9.6. CVE-2026-21655 allows remote code execution on Johnson Controls victor application servers.

Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.

Certighost AD CS vulnerability details and PoC code for CVE-2026-54121 are public. The flaw let a low-privileged user impersonate a Domain Controller.
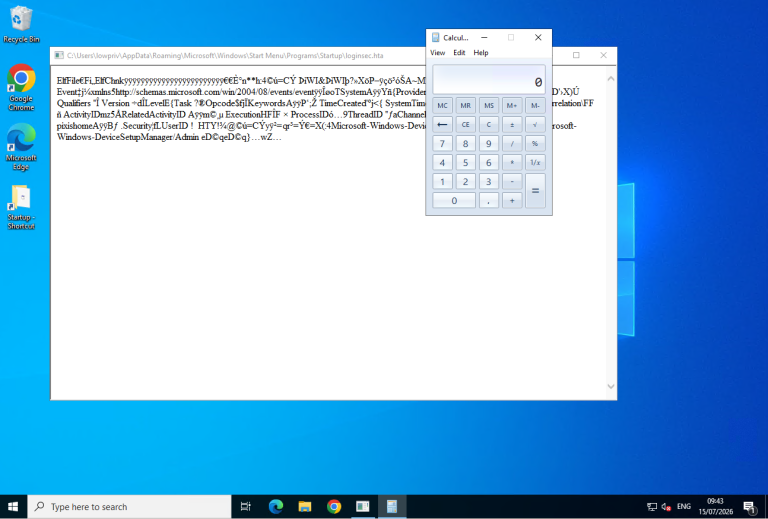
A public PoC exploit now targets CVE-2026-50502, an RCE in the Windows Event Log service. Microsoft patched the flaw on July 14, 2026. Details below.

A TA488 half-click exploit abuses CVE-2026-42897 in Outlook Web Access to drop OWAReaper, a stealthy implant that survives device reimaging.

Broadcom released updates to fix a critical VMware authentication bypass (CVE-2026-59309). A directory traversal flaw (CVE-2026-59310) was also patched.
FortiGuard Labs found a TrickBot DNS tunneling variant that hides malware C2 communication inside malformed DNS queries and IP address responses.
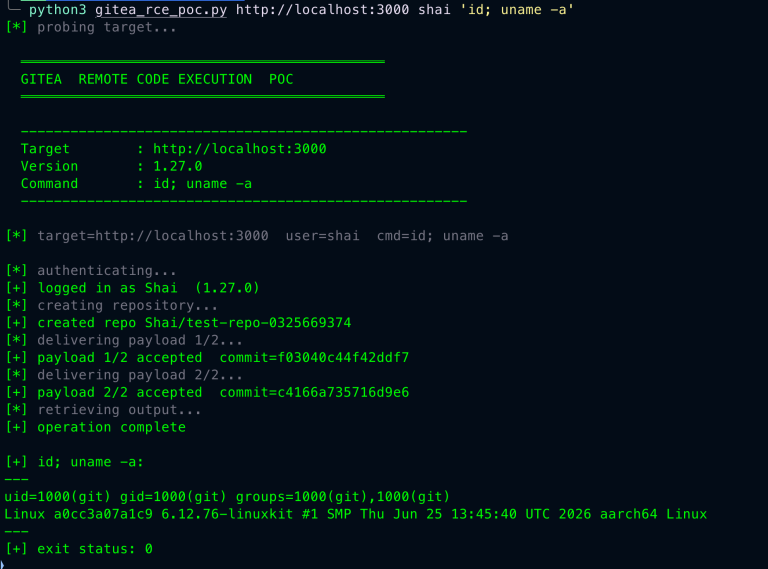
CVE-2026-60004 is a critical Gitea RCE via a diffpatch Git hook, rated CVSS 9.8. Full details and a public PoC are out. Update to Gitea 1.27.1 now.
A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.

Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.

The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.