
 Do Son
A new report reveals the Silver Fox APT group is abusing a Microsoft-signed vulnerable driver to disable endpoint security and deploy the ValleyRAT backdoor.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

Amazon has disrupted a watering hole campaign by Russia's APT29. The hackers used compromised sites to trick users into authorizing attacker-controlled devices via Microsoft.

The DOJ has indicted 28 members of a Chinese fraud ring for a $65M scheme targeting seniors. Evidence from YouTubers 'Scammer Payback' helped in the takedown.
A new Anthropic report reveals how criminals are weaponizing AI systems to automate attacks, create AI-generated ransomware, and secure fraudulent employment.

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.
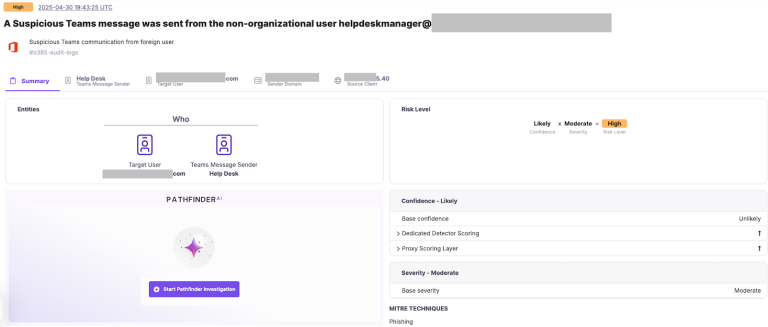
A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.

A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.

The U.S. Treasury has sanctioned individuals and entities linked to a North Korean IT worker scheme, which funnels millions of dollars to the regime's weapons programs.

A new report reveals how scammers are exploiting the Ganesh Chaturthi festival in India with fake websites, lottery fraud, and phishing to steal money and data.

A new report reveals DSLRoot, a residential proxy network operated by a Belarusian national that uses hardware planted in U.S. homes, enabling foreign operators to bypass security.

A new report reveals a mobile malware campaign in Indonesia impersonating the state pension fund TASPEN to steal financial and personal data from civil servants.

A new report reveals a widespread data theft campaign targeting Salesforce instances. Attackers used compromised OAuth tokens from a third-party app to steal data and credentials.

A new report reveals a persistent phishing campaign targeting ScreenConnect super admins. The stolen credentials are being sold to ransomware affiliates for future attacks.

A new phishing campaign called ZipLine reverses the attack by tricking victims into initiating contact. It targets supply chains and deploys a custom in-memory implant.

A supply chain attack on the Nx build system is stealing crypto wallets and SSH keys from developers. The malware also abuses AI tools for data exfiltration.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.

GreyNoise reports a massive, coordinated scanning campaign targeting Microsoft RDP services. Attackers are probing tens of thousands of IPs to prepare for future attacks.
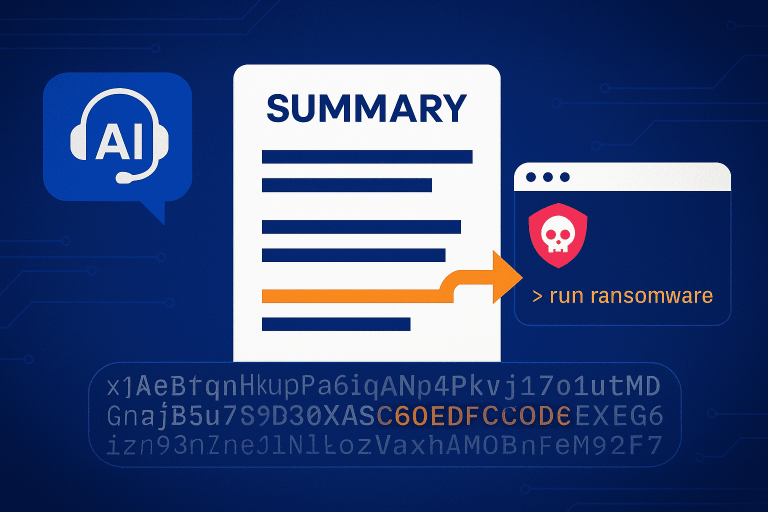
A new report reveals how attackers are using invisible text and "prompt overdose" to trick AI summarizers into delivering ransomware instructions to users.

A new report reveals that the Pakistan-linked APT36 is now targeting Indian government and defense entities with Linux-specific malware delivered via Google Drive.

A data leak from an alleged North Korean APT group's workstation has revealed its use of a commercial proxy service, offering a rare look into its anonymizing infrastructure.

A coordinated international operation led by Europol has dismantled a criminal network responsible for a string of explosive ATM attacks in Austria, Germany, and the Netherlands.