
 Do Son
The victim's computer is infiltrated with remote access trojans known as LummaC2 and RecordBreaker (also referred to as Raccoon Stealer V2)
Malware

Malicious actors behind the ShellBot botnet are employing hexadecimal-converted IP addresses to infiltrate vulnerable SSH Linux servers

In a stark reminder of the constantly evolving cyber threat landscape, September 2023 witnessed a formidable ransomware attack on the automation giant
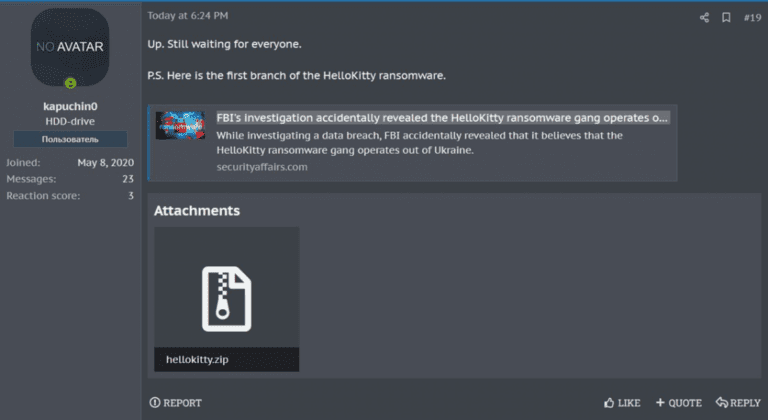
3xp0rt discovered that the full source code of the inaugural version of the HelloKitty ransomware has been unveiled on cybercrime forums

VBA script initiates a series of actions, creating a directory, downloading an AutoIt3 executable, and preparing the ground for the DarkGate malware

Human Security revealed a staggering 74,000 globally distributed Android devices exhibiting traces of the Badbox malware

Spyware typically records user activity and transmits it to servers, consuming significant smartphone resources.

This campaign displays significant overlaps with tactics, techniques, and procedures (TTPs) previously linked to cyber espionage initiatives

Microsoft Defender showcased its susceptibility to false positives by recognizing the Tor browser as a virus and halting its operations

Menorah malware was spotted playing a crucial role in a recent targeted phishing attack demonstrating the group's undiminished proclivity

The Cl0p ransomware group exploited a popular SQL injection vulnerability (CVE-2023-34362) within the MOVEit file transfer solution

According to Kaspersky Lab, the Linux application, "Free Download Manager", has clandestinely been embedded with a backdoor

In a detailed expose, Symantec pointed out that Redfly employed the ShadowPad Trojan to infiltrate a national power grid in Asia

Using its dynamic memory extraction technique, MemDive intercepts the payload even before its execution.

In July 2023, JPCERT identified and christened this technique "MalDoc in PDF", which ingeniously sidesteps detection

Revealed in May this year, this flaw is exploited to release the Kinsing malware and a cryptominer, posing significant risks for users

DreamBus malware uses a blend of service setups and cron jobs, scheduled hourly, to ensure consistent execution of its payload.

due to prior cyberattacks, for security considerations, LetMeSpy will cease offering its services to anyone starting August 31, 2023.

the software's ubiquity has drawn the attention of cybercriminals, who are deceiving and compromising these users via a Trojanized MS Visual Studio malware

The botnet under investigation by Black Lotus Labs, for instance, has seen its AVrecon malware infect over 70,000 Linux-based routers

After trace analysis, Kaspersky discovered 34 analogous extensions on the Chrome Web Store. While these extensions offer specific functionalities

Fortinet revealed that the Condi botnet had infected a significant number of AX21/AX1800 routers, offering DDoS services