
 Do Son
Now that the second wave of sabotage has begun, the researcher released the source code of the Conti ransomware.
Malware
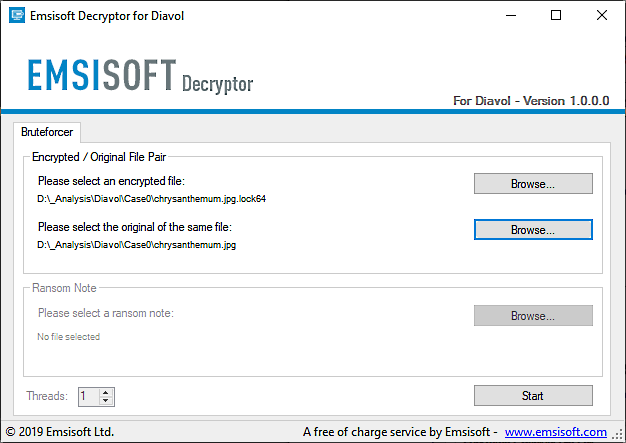
Using the Diavol ransomware decryptor tool, users can decrypt files encrypted by Diavol for free, and the encrypted file formats include .lock64 and so on

Once the device is successfully compromised, B1txor20 Linux backdoor utilizes the DNS tunnel to retrieve and execute commands sent by the server
Microsoft Defender for Endpoint incorrectly flagged Microsoft Office updates as malicious, saying a potential ransomware behavior

hackers are not using normal software to sign, and security researchers have found multiple pieces of malware that carry Nvidia's code-signing certificate

Previously, Nvidia suffered a ransomware attack by a hacker group, and its internal systems were compromised

Asustor, a NAS server manufacturer under ASUS, has been attacked by Deadbolt ransomware, and many users have reported on the ASUS Technology forum

Criminals also saw an opportunity in this case, and the gang behind the RedLine malware started creating fake upgrades to lure users into downloading
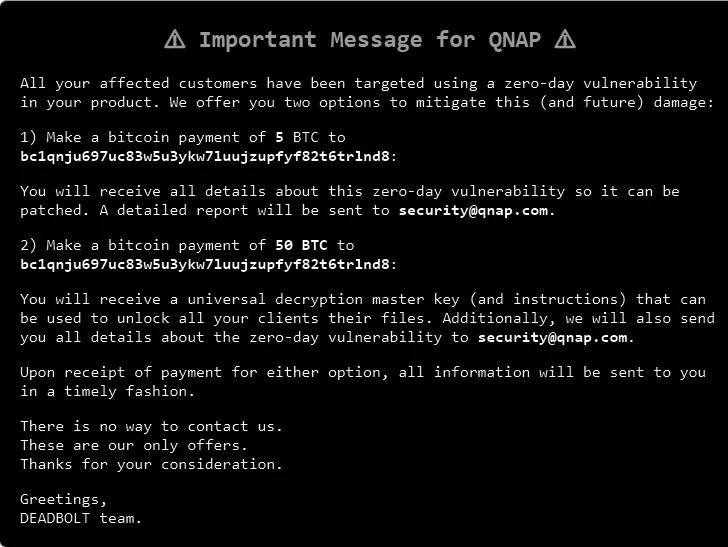
DeadBolt ransomware is looking for exposed NAS on the network, and then looking for potential vulnerabilities to try to launch an attack

Google has previously issued a policy change reminder, and if users store or use files with security issues in Google Drive, a banner warning will pop up
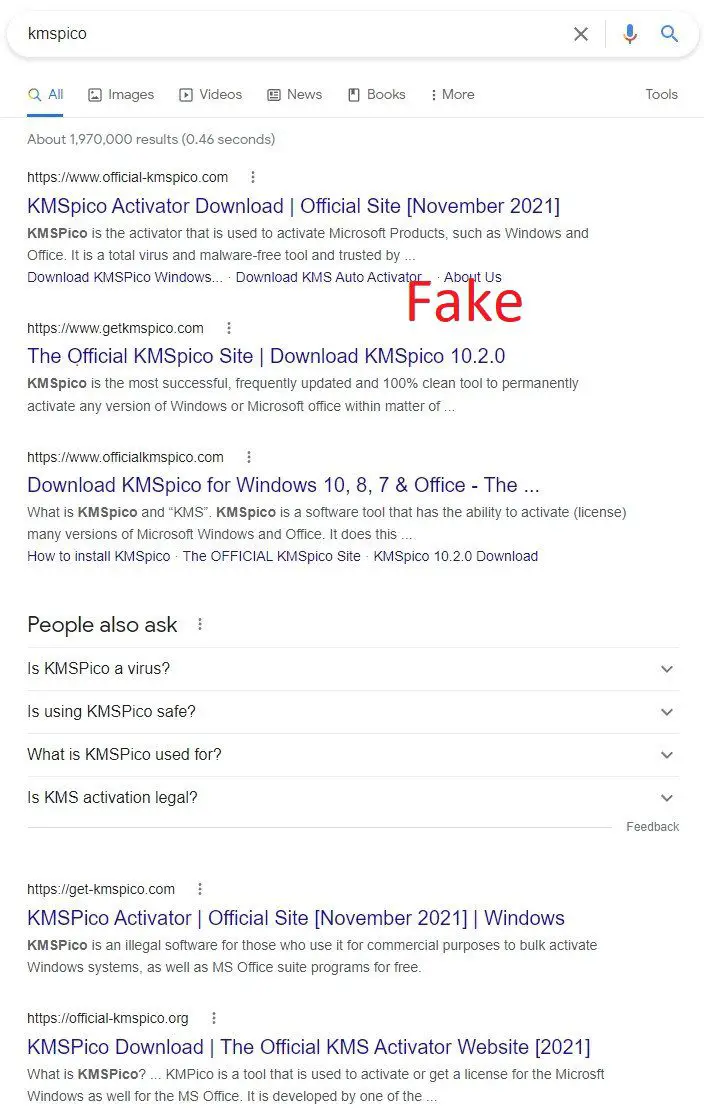
Malicious KMSPico installers mainly embeds malicious software in the activator and then distributes it through the Internet and software forums.

According to the report, 86% of the 50 Google Cloud instances recently attacked were used to perform cryptocurrency mining.
Emotet is now making a comeback with the help of TrickBot malware, and researchers are currently paying close attention to the development of Emotet

In October 2016, a hacker used the Mirai Internet of Things worm to control millions of Internet...
Recently, network security company Check Point disclosed a massive malicious advertising attack. The attacker hijacks user traffic...
According to AppleInsider, Apple’s iPhone and iPad chip foundry TSMC were attacked by computer viruses, and several...

Brazil has been attacked by a well-designed cryptocurrency attack that has infected hundreds of thousands of routers...

It is essential for developers to download development tools from official channels, otherwise, it is very likely...
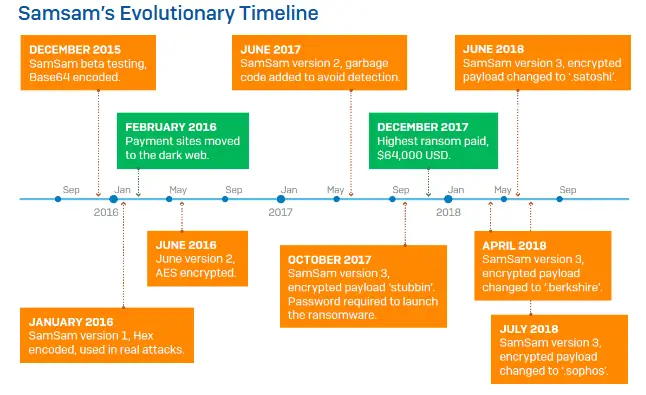
The SAMSAM ransomware that attacked the Atlanta City System in the United States earlier, the attacker has...

Tech support scams from India has recently been found to play with new tricks – scammers send phishing...
The latest report from FireEye security companies shows that hackers are inserting backdoors into victims through security...
According to the US Long Beach local media Press-Telegram July 24, 2018 report, China Ocean Shipping Co....