Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • Samsam ransomware creator has earned $6 million in ransom from victims
  • Malware

Samsam ransomware creator has earned $6 million in ransom from victims

Do Son August 2, 2018 3 minutes read
Samsam ransomware

The SAMSAM ransomware that attacked the Atlanta City System in the United States earlier, the attacker has received a $6 million ransom in the past two years.


SAMSAM attack method:

Unlike normal ransomware attacks, SAMSAM does not infect regular household users through a wide-spreading way because the success rate of blackmail is too low.

This professional criminal gang focuses on the ransomware business and uses social engineering to carefully select targets and then launch attacks in a targeted manner.

For example, in the current dark market black market, look for the RDP remote protocol password of the target organization, or violently crack the server that forcibly logs in to the victim.

If the infection is successful, all the documents are immediately encrypted with high intensity, forcing the victim to pay the ransom to the criminal gang to obtain the file decryption key.

Unlike WannaCry, which has a wide range of ransomware, SAMSAM ransomware has neither worm modules nor virus-like features.

That is to say, SAMSAM relies entirely on human attackers to manually infect rather than worms to automate attacks, which is also a typical feature of SAMSAM.

Carefully selected targets for huge ransoms:

At present, the ransomware industry has dropped significantly in the mining tide from the end of last year to the beginning of this year, because many entry-level hackers have abandoned ransomware.

The main reason is that many ordinary home users do not care about encrypted files. They encounter ransomware and do not pay the ransom.

For example, WannaCry, which infected more than 200,000 computers last May, only received a $150,000 ransom, which is no match for SAMSAM.

SAMSAM will ask for a ransom of up to $50,000 after successfully infecting large enterprises and institutions, which is hundreds of times more than the industry average.

Due to the carefully selected targets that make SAMSAM a very successful rate, most organizations pay ransom after being infected, except Atlanta City.

Earlier, the Atlanta municipal system was directly attacked and lost as much as $2.7 million, but the city did not believe that it could not encourage hackers to be arrogant and then not pay the ransom.
 

A $6 million ransom in two and a half years:

After a long-term follow-up, the foreign security company SOPHOS analyzed and counted the bitcoin wallet address used by the criminal gang and the flow of bitcoin.

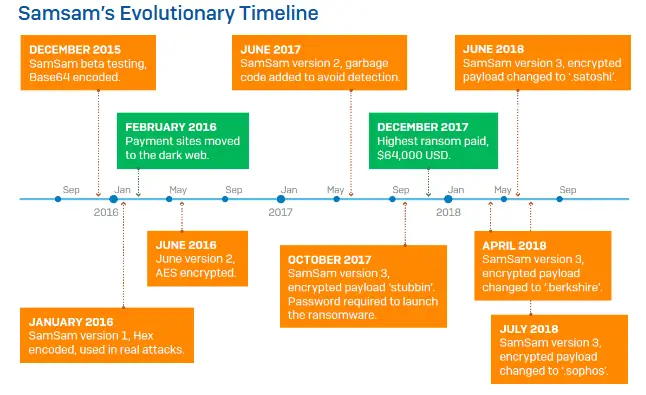
It was finally determined that SAMSAM had received a $6 million ransom since its launch in December 2015, and an average of $10,000 in ransom payments per day.

One of the victims was also carefully selected by the SAMSAM gang, who eventually paid the band for up to $64,000 in ransom.

Daily safety precautions reminder:

The best solution for ransomware attacks is naturally to do an excellent job of data backup every day, which can not only deal with ransomware but also other accidents.

At the same time, the server tries to enable key login or 2-step verification. Both Windows Server and Linux distributions support 2-step verification.

There are also servers that use high-intensity passwords and modify the default port number as much as possible to avoid being hacked and hacked into the server by criminal gangs.

Of course, the extra reminder is that you don’t trust the various download stations, crackers or plug-ins to prevent carrying backdoors.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Anubis Ransomware: New RaaS Combines Encryption with Permanent Data Wiping
  • From SideCopy to Transparent Tribe: Pakistan APTs Hit Indian Government With RATs
  • New malware automatically detects computer configuration to determine mining or crypting
  • Jellyfish Loader: Stealthy .NET Malware Raises Cybersecurity Concerns
  • Beast Ransomware: RaaS Platform Targets Windows, Linux, and VMware ESXi
  • A new bank Trojan, BankBot Anubis was found PhishLabs
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: SamSam Ransomware

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-83770CVSS 9.8
    Heap-based buffer overflow in Windows Text Shaping allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-83780CVSS 9.8
    Use after free in Windows CCFFilter Driver allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    📅 Updated: Nov 2, 2026
  • CVE-2026-83782CVSS 9.8
    Heap-based buffer overflow in Windows Shell allows an unauthorized attacker to execute code over a network.
    📅 Updated: Nov 2, 2026
  • CVE-2026-19677CVSS 9.3
    An authentication bypass vulnerability in the public onPhase/ frevvo registration form version 11.0.14 allows an unauthenticated remote attacker to...
    📅 Updated: Nov 2, 2026
  • CVE-2026-111594CVSS 9.2
    InterSystems IRIS for Health has TLS/SSL encryption turned off by default, which may enable an attacker to view...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120213CVSS 9.1
    @fastify/http-proxy is a Fastify plugin that proxies HTTP requests to an upstream server under a configured prefix. In...
    📅 Updated: Nov 2, 2026
  • CVE-2026-102435CVSS 9.8
    The Ultra Addons for Contact Form 7 plugin for WordPress is vulnerable to arbitrary file deletion due to...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.