
 Do Son
A new report from Trend Micro has revealed that ShadowPad, a modular malware with deep ties to...
Malware

Cybersecurity firm CYFIRMA has uncovered a highly sophisticated malware campaign leveraging JavaScript to establish covert communication with...

Elastic Security Labs has recently uncovered an expansive cyber espionage campaign, codenamed REF7707, that spans across South...

AhnLab Security Emergency Response Center (ASEC) has issued a warning about a new distribution method for the...

On December 31, cybercriminals launched a mass infection campaign, dubbed StaryDobry, leveraging the holiday season’s increased torrent...

Security researchers at Netskope Threat Labs have uncovered a new backdoor malware written in Golang that leverages...

A newly discovered ransomware campaign, dubbed XELERA, is targeting job seekers in India with fraudulent Food Corporation...
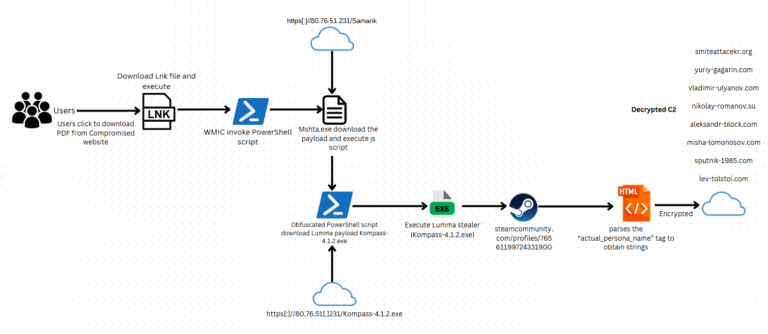
A new report from CloudSEK reveals an ongoing malware campaign distributing the Lumma Stealer information stealer, primarily...

Valve has removed the video game PirateFi from its Steam platform after the discovery of embedded malicious...

Researchers at eSentire Threat Response Unit (TRU) uncovered a sophisticated cyber espionage campaign by RedCurl/EarthKapre, a threat...

Microsoft Threat Intelligence has discovered a new variant of the XCSSET malware targeting macOS users. This sophisticated...

Cybersecurity researchers at JPCERT/CC have uncovered a significant upgrade to the SPAWN malware family, introducing SPAWNCHIMERA, a...

In a recent investigation into the REF7707 intrusion set, Elastic Security Labs has identified a new malware...

A new MageCart attack targeting Magento-powered eCommerce websites has been uncovered by researchers at Sucuri, revealing a...

Cybersecurity researchers at Sekoia have uncovered a new and sophisticated Remote Access Trojan (RAT) leveraging the Invisible...
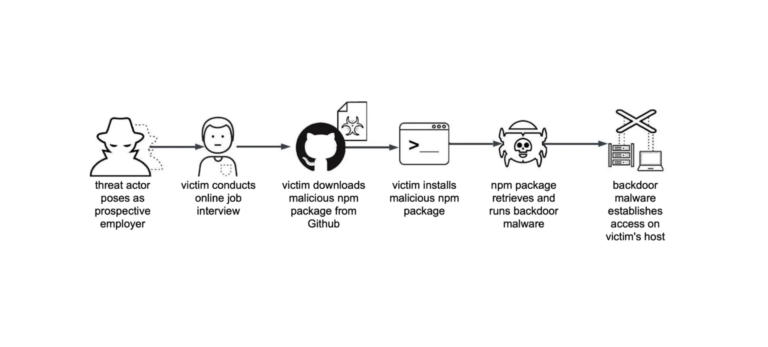
North Korea’s infamous Lazarus Group is back in the spotlight, this time deploying a sophisticated infostealer malware...

A newly discovered Android Remote Access Trojan (RAT) called BTMOB RAT has been observed targeting unsuspecting users...

A new report from AhnLab Security Intelligence Center (ASEC) reveals a concerning trend: the distribution of cryptocurrency-mining...

The notorious Sandworm APT (APT44), a Russian-state-sponsored threat actor affiliated with the GRU (Russia’s Main Intelligence Directorate),...

New research from ReversingLabs has uncovered a novel technique for distributing malware on the Hugging Face platform,...

A new analysis from the TEHTRIS Threat Intelligence team details the resurgence of LegionLoader, a sophisticated malware...

Trend Micro researchers have uncovered a widespread SEO manipulation campaign orchestrated by a Chinese-speaking group utilizing a...