
 Do Son
Uncover the tactics used by the North Korean APT group Kimsuky in their cyber espionage operations, including the use of the RDP Wrapper for persistent access.
Malware

Learn about the widespread BADBOX botnet infecting Android devices via compromised firmware. Stay protected from this insidious threat.

Unveiling the sophisticated Silver Fox APT: Learn how this multi-stage malware campaign deploys the resilient ValleyRAT.
Unveiling a malicious Go package discovered in the Go ecosystem. Learn how a typosquatting package exploits the Go Module Proxy's caching mechanism.

Discover the NOVA stealer, a new commercial variant of the SnakeLogger malware. Learn how this campaign is targeting Russian organizations.

Uncover the intricate web of the SmartApeSG FakeUpdate campaign and its connections to NetSupport RAT and other malicious threats.
Uncover the new 'FlexibleFerret' macOS malware attributed to North Korean threat actors. Learn about the evolving tactics and job interview schemes used in these espionage campaigns.

Beware of the SparkCat malware campaign that steals cryptocurrency recovery phrases using optical character recognition (OCR) technology on Android and iOS devices.

Learn about the Coyote Banking Trojan, a stealthy malware campaign targeting online banking users. Protect yourself from this sophisticated threat

Uncover the TAG-124 traffic distribution system used by cybercriminals to spread malware, phishing pages, and fake browser updates.
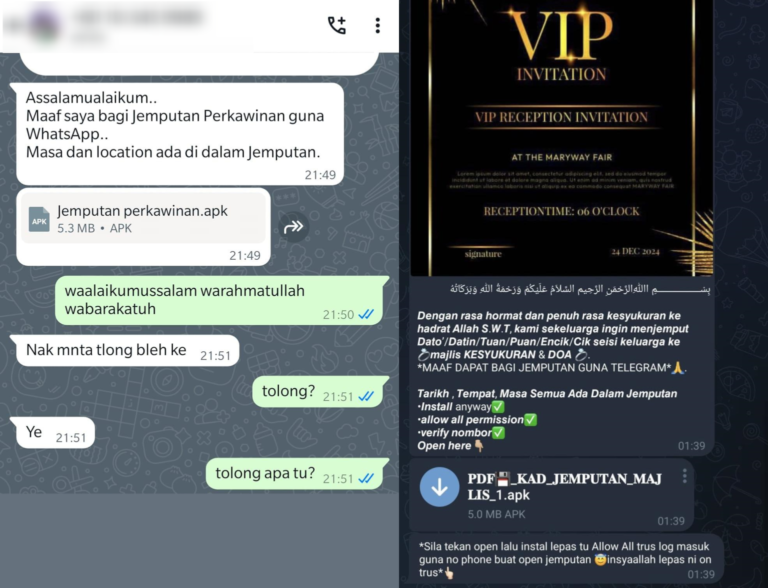
Tria Stealer: a dangerous Android malware campaign that steals personal messages, hijacks WhatsApp and Telegram accounts, and facilitates financial fraud.

Uncover the details of a newly identified cyberespionage campaign, CL-STA-0048, targeting high-value organizations in South Asia.

Uncover the threat of Tiny FUD, a fully undetectable macOS backdoor that poses a significant risk to Apple users.

Learn about a sophisticated attack campaign targeting WordPress websites and delivering SocGholish Windows malware to unsuspecting users.

Uncover a sophisticated malware campaign using GitHub's release infrastructure to distribute the dangerous Lumma Stealer Trojan. Learn more.

Discover the latest supply chain attack orchestrated by the North Korean APT Lazarus Group. Learn how the BeaverTail malware infiltrates developer environments.

Explore the evolution of SparkRAT, a powerful tool for cybercriminals. Learn about its modular design, web-based interface, and cross-platform support.

Beware of fake game hacks! McAfee Labs warns about malware spread through YouTube videos offering cheats for popular games like Minecraft, Roblox, and Fortnite.

Uncover the unique attack method involving the Phorpiex botnet and LockBit Black Ransomware. Find out how automation is changing the landscape of ransomware deployment.

Protect your organization from the SapphireRAT phishing attack. Discover how cybercriminals are evading traditional security measures with fake legal notices.

Discover ScatterBrain, a powerful obfuscating compiler employed by APT41. Understand its role in protecting the advanced modular backdoor POISONPLUG.SHADOW.
Mitel SIP phones under active exploitation by Aquabotv3, a new variant of the Mirai-based botnet. Learn about the undisclosed vulnerability CVE-2024-41710.