
 Do Son
Beware of a recent phishing website targeting Homebrew, a popular macOS package manager. Learn how this incident exposes flaws in Google's ad system.
Malware
Discover the top three malware families that caused havoc in the cybersecurity landscape in 2024. Learn how to defend against Lumma, Agent Tesla, and AsyncRAT.

Uncover the secrets of Gootloader malware. Explore its use of poisoned SEO and compromised WordPress websites to deliver malicious payloads.

Stay informed about the MintsLoader malware campaign and its impact on the Electricity, Oil & Gas, and Law Firms & Legal Services industries.

Discover the ValleyRAT malware and how the Silver Fox APT group utilizes the PNGPlug loader to execute their cyber-espionage attacks.

Beware of the malicious PyPI package targeting Discord developers. Learn how typosquatting can lead to token theft and backdoor installation.
NVISO Labs uncovers a new phishing campaign by Black Basta. See how they employ Microsoft Teams as a tool for social engineering attacks.
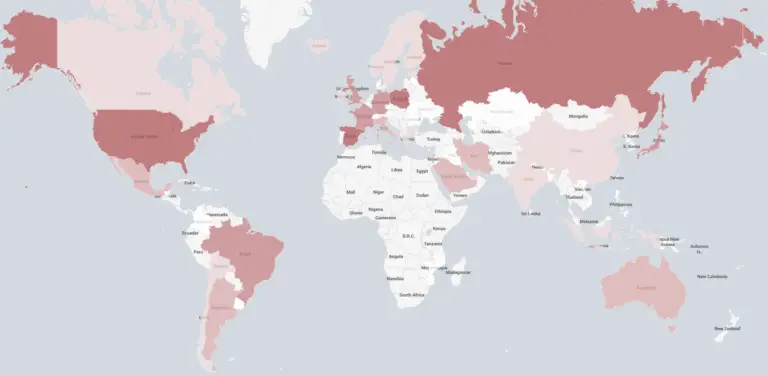
Discover how a newly discovered IoT botnet is targeting organizations globally with large-scale DDoS attacks.

Uncover the ClickFix Technique and its use by North Korea's Lazarus APT group. Learn how this advanced social engineering method targets job seekers.

U.S. authorities successfully neutralize Chinese state-sponsored cyber espionage threat by deleting PlugX malware.
Learn about the concerning supply chain attack targeting popular Node.js libraries, chokidar and chalk, and how developers can protect their projects.

Protect your WordPress website from the WP3.XYZ malware attack. Learn how to detect and prevent unauthorized admin accounts, malicious plugins, and data exfiltration.

Uncover the sophisticated phishing campaign leveraging Formbook stealer. Learn how this notorious malware continues to evolve and maintain its notoriety in the MaaS market.

Learn about the sophisticated sysinitd rootkit and how it hijacks network traffic and executes malicious commands on compromised Linux systems.

Discover the UAC-0063 cyber espionage campaign: Russia's strategic interest in Central Asia's geopolitical dynamics.
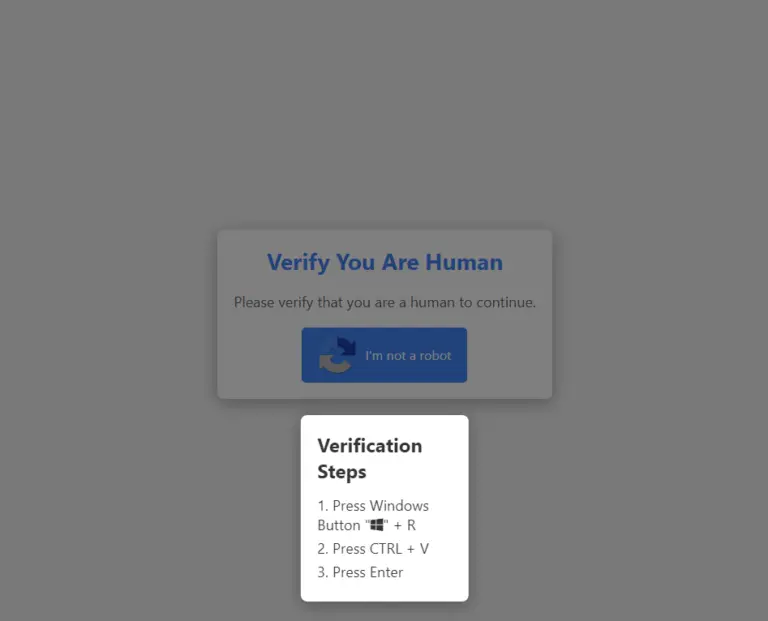
Beware of the stealthy LummaC2 Infostealer malware. Learn how it tricks users with a fake CAPTCHA page and initiates a series of malicious steps.

Unveiling the new HexaLocker V2: a more sophisticated and complex ransomware variant with advanced encryption and data theft features.

Uncover the details of RedDelta: A sophisticated cyber-espionage group targeting political and government entities in Asia.

Discover the latest cyber threat: RedCurl APT group. Learn about their sophisticated techniques and targeted cyber espionage campaigns.

Discover the latest cyberattack on GroupGreeting.com. Learn about the sophisticated JavaScript injection techniques used in the “zqxq” campaign.

Beware of cracked software and fake installers. Discover how cybercriminals exploit user trust and spread malicious payloads.
Stay informed about the latest credit card skimming malware targeting WordPress checkout pages. Learn how this sophisticated malware evades detection and steals sensitive payment details.