
 Do Son
Discover cShell, a new strain of DDoS malware targeting poorly managed Linux SSH servers. Learn how it exploits weak credentials to turn servers into DDoS bots.
Malware

Stay informed about the rise of VIPKeyLogger, a dangerous infostealer malware that poses significant risks to individuals and organizations.

Uncover the dangers of the Mamont Android banking Trojan. Protect yourself from malicious parcel tracking apps and photo identification scams.

The BADBOX botnet is making a comeback with a vengeance. Discover the alarming details about its resurgence and growing sophistication.

Unveiling the Lumma infostealer malware: How a malvertising campaign uses fake CAPTCHA prompts to spread this dangerous threat.

Discover RiseLoader, a new malware family focused on efficient payload delivery. Get insights into its origins, similarities with RisePro, and advanced anti-analysis measures.
Learn about Nova, a dangerous variant of the Snake Keylogger family. Discover its advanced techniques and how it evades detection in cybersecurity.

Learn about the I2PRAT malware campaign, a sophisticated threat that leverages the Invisible Internet Project (I2P) to hide its activities and evade detection.
Stay informed about the latest threat to organizations worldwide: the HiatusRAT malware campaign targeting IoT devices.
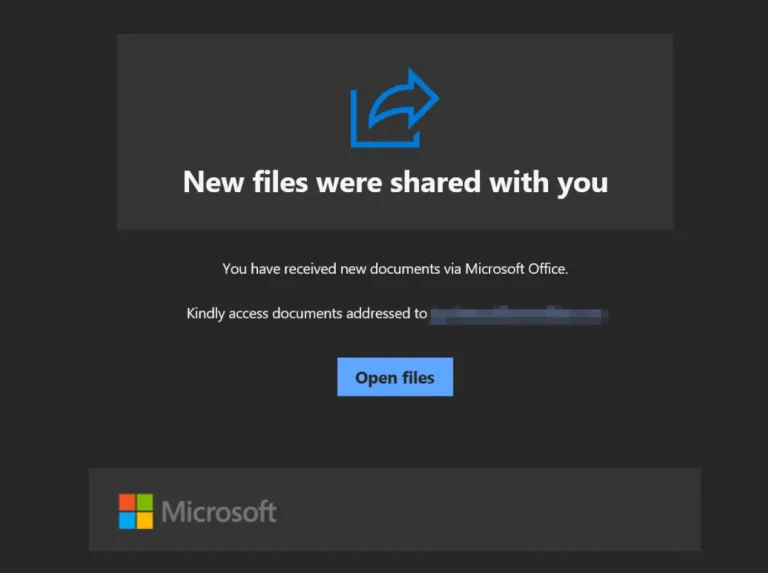
Unveiling a new malicious SharePoint impersonation campaign delivering Xloader malware. Learn how this sophisticated attack takes advantage of brand impersonation and advanced process injection.

Beware of CoinLurker, a sophisticated data-stealing malware targeting cryptocurrency users and businesses through fake browser update campaigns.

Explore the sophisticated ransomware campaign targeting DrayTek Vigor routers. Discover the tactics used by cybercriminals and steps to secure your devices.

Explore the TIDRONE threat actor and their cyberattacks on Korean companies. Find out how they exploit ERP software and deploy malware.
Discover the techniques used by Yokai Backdoor to bypass detection and exploit trusted executables. Stay informed about the latest cybersecurity threats.

Discover HeartCrypt, the powerful Packer-as-a-Service used by cybercriminals to protect malware from detection.

Discover GOSAR backdoor, a new Golang-based malware variant that rewrites the QUASAR RAT. Learn about its cross-platform capabilities and reduced detection rates

Discover how NodeLoader malware uses Node.js applications for Windows to deliver second-stage payloads, including XMRig, Lumma, and Phemedrone Stealer.

Discover the new threat of voice phishing (vishing) via Microsoft Teams. Learn how cybercriminals are leveraging this tactic to distribute dangerous malware.

Discover the shocking details of the MUT-1244 cyberattack campaign targeting security professionals and hackers, resulting in the theft of sensitive data.
Uncovering the tactics of Secret Blizzard: Learn how this threat actor co-opts tools from cybercriminals to target Ukraine.

Stay informed about the ongoing malvertising campaign targeting graphic design professionals. Learn how to protect yourself against this threat.