
 Do Son
Learn about the supply chain attack on Ultralytics, a popular AI library with over 60 million downloads, and how it was exploited through GitHub Actions scripts.
Malware

Unveil the sophisticated operations of BlueAlpha, a state-sponsored threat actor. Explore their use of HTML smuggling, Cloudflare Tunnels, and spearphishing to distribute GammaDrop malware.
Learn about the dangers of targeted surveillance and the Monokle spyware. Find out how a Russian programmer's Android device was infected with malicious spyware.

Uncover the dark secrets of the Earth Minotaur cyber campaign. Learn about the MOONSHINE exploit kit and the dangerous DarkNimbus backdoor.

Uncover the sophisticated cyberattack campaign targeting the manufacturing industry. Learn about the advanced techniques and the Amadey Bot used by threat actors.

Discover the shocking prevalence of the notorious Pegasus spyware in mobile devices. iVerify's investigation reveals seven infections in a sample of 2,500 devices.

Uncover the secrets of Secret Blizzard, a Russian threat actor known for hijacking other groups' infrastructure for intelligence gathering.
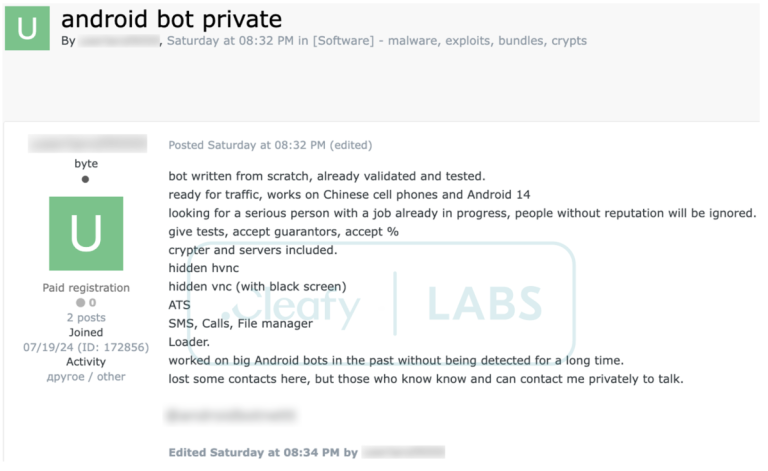
Dive into the world of mobile malware with DroidBot, a powerful Android RAT that combines hidden VNC, overlay attacks, and keylogging capabilities.

The threat actors have refined their techniques, introducing novel methods for gaining access and delivering malware, including Zbot, DarkGate

Learn about the latest discovery of a new cluster of Andromeda malware servers and its targeted activities in the APAC region.

Discover the strategic evolution of Akira ransomware with the introduction of Akira v2, a Rust-based variant. Learn how its use of Rust enhances its complexity and cross-platform capabilities.
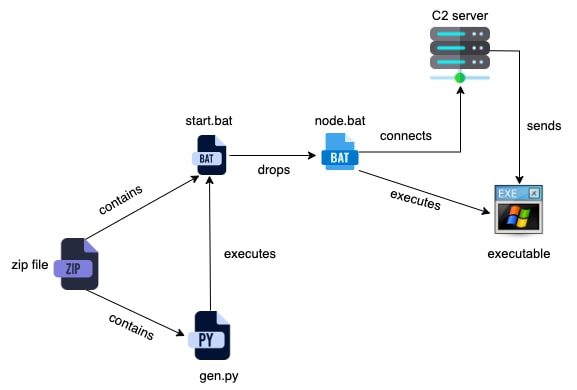
Unveiling the inner workings of Celestial Stealer: a powerful infostealer disguised as legitimate applications, targeting developers, gamers, and cryptocurrency users.

Discover the impact of the RECOPE ransomware attack on Costa Rica's fuel supply chain. Learn about the challenges faced and potential fuel shortages.

Warning: Security alert for Solana Web3.js users! Learn about a recent supply chain attack on the widely-used JavaScript library and how it puts developers and users at risk.

Discover the new target of Gafgyt malware: misconfigured Docker Remote API servers. Learn how attackers exploit these servers and deploy the malware.

Discover the latest malware threats: RevC2 and Venom Loader. Learn how cybercriminals are leveraging these malicious tools for remote code execution and data theft.

Explore the advanced tactics of the infamous SmokeLoader malware campaign. Discover how it used phishing emails and plugins to launch multi-layered attacks.

Explore the BurnsRAT and NetSupport RAT used in the Horns&Hooves campaign. Dive into the details of this cybercriminal operation targeting individuals and businesses

Learn about a new 0-day attack that bypasses antivirus and sandbox defenses, allowing malicious payloads to reach users' inboxes undetected.

Uncover the LogoFAIL vulnerability and Bootkitty, the new UEFI bootkit targeting Linux. Explore the impact of this emerging firmware-based threat.

Learn about the sophisticated cyber attack dubbed 'Operation Code on Toast' and the North Korean-linked hacking group TA-RedAnt behind it.

Unveiling the dark side of Windows' wevtutil.exe. Explore the dangerous potential of this legitimate tool in the hands of attackers.