
 Do Son
Stay informed about the latest supply chain attack on cryptocurrency wallets via PyPI. Discover the malicious aiocpa package and steps to enhance your security.
Malware

Beware of the critical vulnerability CVE-2024-11667 in Zyxel firewalls. Learn how attackers are exploiting it to deploy Helldown ransomware.
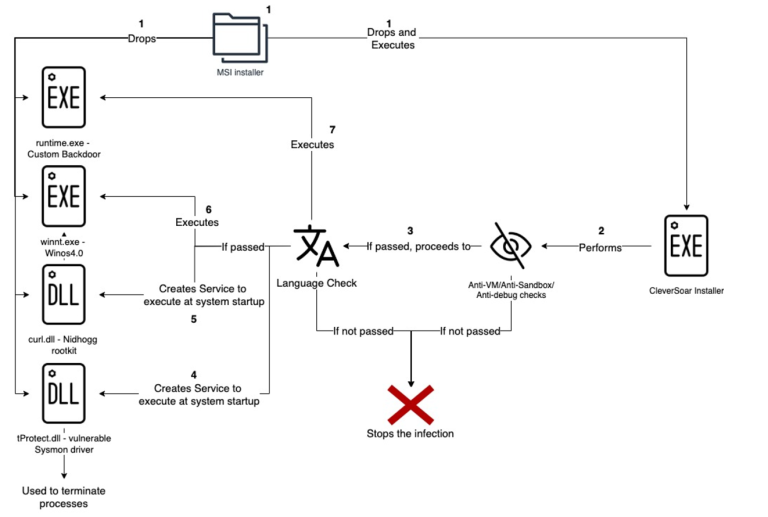
Discover the newly identified CleverSoar installer and its targeted espionage efforts. Explore the advanced evasion techniques and malicious components used in this sophisticated malware campaign.

Beware of a targeted campaign against crypto developers. Learn about the malicious npm packages and the risk they pose to cryptocurrency wallet credentials and sensitive data.
Discover how cybercriminals are leveraging the Godot game engine to distribute malware. Learn about the GodLoader technique and how it evades detection.

Stay informed about the latest threat to Magento websites: credit card skimmer malware. Learn how it works and how to protect yourself.

Discover the resurgence of PixPirate malware targeting financial services through WhatsApp. Learn how this highly sophisticated threat has expanded its reach globally.

Unveiling the Matrix DDoS campaign: Aqua Nautilus researchers reveal a new threat actor leveraging accessible tools to launch large-scale cyberattacks.

Learn about the new Elpaco ransomware variant and its sophisticated customization features. Discover how it exploits vulnerabilities and leverages legitimate software tools.

Discover the ANEL backdoor's resurgence and the evolving capabilities of the Earth Kasha cyber-espionage group.

Discover the resurgence of the XorBot botnet, a potent threat to IoT devices worldwide. Learn about its advanced anti-detection mechanisms and wide range of exploits.

Uncover the year-long NPM supply chain attack involving the malicious @0xengine/xmlrpc package. Learn how it combined cryptocurrency mining with data theft.

Learn about the SMOKEDHAM backdoor and its role in the activities of threat actor UNC2465. Discover how this highly adaptable tool is used in extortion and ransomware operations.

ESET researchers unveil Bootkitty, a UEFI bootkit targeting Linux. Find out how it operates and why it signals a new chapter in UEFI threats.
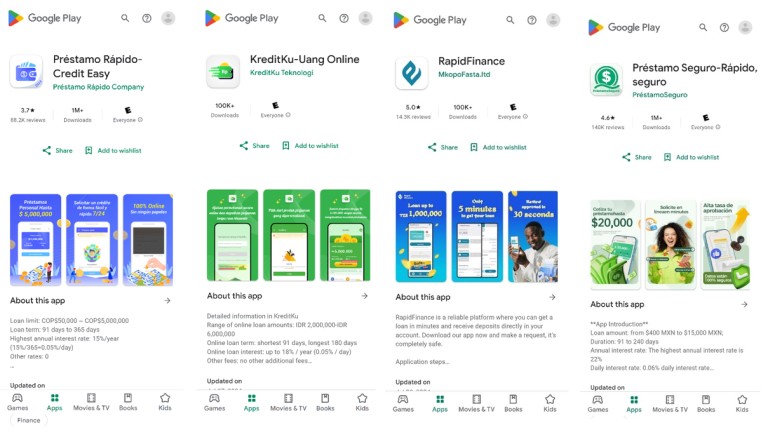
Protect your privacy and financial security from SpyLoan apps. McAfee Labs reveals the risks of these predatory loan apps exploiting social engineering tactics.

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.

Uncover the activities and alliances of CyberVolk, the pro-Russian hacktivist collective posing a significant threat in the cybercrime world.
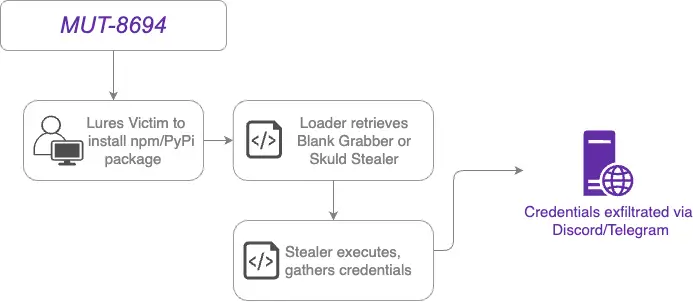
Uncover the supply chain attack by MUT-8694. Learn how this enigmatic threat actor targeted Windows users using malicious npm and PyPI packages.

Discover the stealthy technique used by the Lazarus Group: RustyAttr. Learn how this method leverages macOS metadata to conceal malicious payloads.

Beware of malicious npm packages disguising themselves as popular libraries. Learn how these packages inject SSH backdoors into developer systems.

Uncover the cyberespionage campaign attributed to TAG-110. Learn about the Russia-aligned threat group targeting organizations and their motives.

Unveiling WolfsBane: The Linux counterpart to Gelsevirine backdoor revealed by ESET researchers. Learn about the evolution of the Gelsemium APT group and their shift in strategy.