
 Do Son
Uncover the evolving threat from the APT-K-47 group and their sophisticated Asyncshell-v4 malware. Learn how this South Asia-based APT group is using malicious campaigns to infiltrate systems.
Malware

Unveiling the operational similarities between PROSPERO and Proton66: a comprehensive report on bulletproof networks and their hosting of malicious software.

Find out how the NodeStealer infostealer has evolved to target Facebook Ads Manager and collect crucial financial information using Facebook’s Graph API.

Uncover the alarming details of the PyPI crypto library attack. Find out how private keys were exfiltrated by a malicious update.

Discover the cybercrime group Ignoble Scorpius and their sophisticated ransomware campaign, BlackSuit, targeting industries worldwide.

Uncover a malicious campaign targeting security drivers. Learn how attackers exploited the Avast Anti-Rootkit driver to bypass and seize control of systems.

Learn about MisakaNetwork, a decentralized blockchain-powered botnet targeting open-source software and compromising systems.

Learn about the implications of the new XenoRAT variant, utilizing Excel XLL files for delivery and posing a threat to enterprise networks.

Uncover the stealthy tactics of a Potentially Unwanted Application (PUA) masquerading as a PDF conversion tool. Learn how persistence mechanisms are exploited by threat actors to maintain control.

Learn about the latest LODEINFO malware campaign attributed to the Earth Kasha threat group, targeting government agencies and high-tech industries in Japan, Taiwan, and India.
Learn about FrostyGoop, an alarming ICS-centric malware that exploits vulnerabilities in internet-exposed devices.

Discover the scale and sophistication of the NSOCKS botnet: a criminal proxy network aiding in DDoS attacks, phishing, and malware obfuscation.

Explore the rising threat of the Helldown ransomware targeting Linux machines. Find out how Sekoia's TDR team uncovered this new variant.

Stay vigilant! A malvertising campaign is spreading malware disguised as a Bitwarden security update. Read to learn how to avoid falling victim.
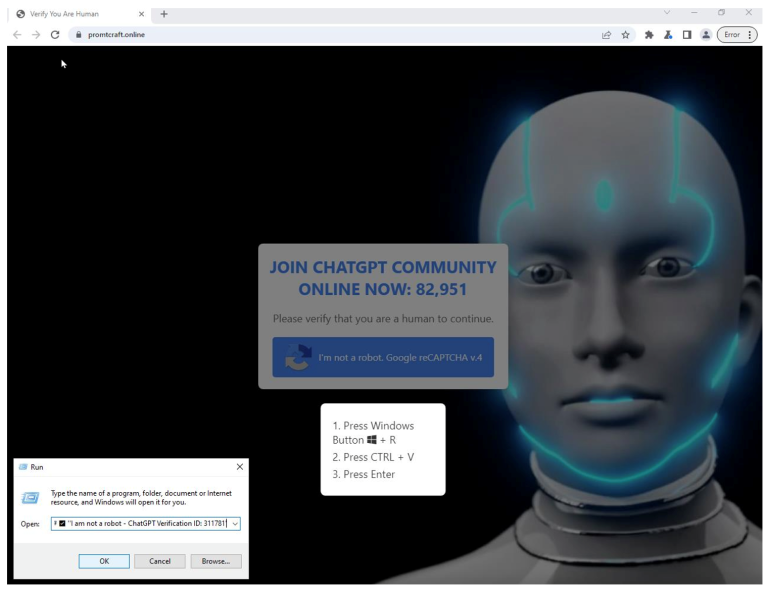
Discover the alarming rise of ClickFix, a unique social engineering method used to spread malware. Learn how it exploits human behavior and how to protect yourself.
Learn about the global ransomware scheme and the extradition of Evgenii Ptitsyn, accused of administering the Phobos ransomware.

Unmasking the elusive BabbleLoader malware loader: a highly sophisticated tool that evades traditional and AI-based detection systems.

Discover the operations of Water Barghest, a highly sophisticated botnet that exploits vulnerabilities to create a profitable residential proxy network.

Discover the sophisticated WezRat infostealer and its role in cyber campaigns targeting the US, Europe, and Israel.

Uncover the details about SafePay ransomware: a stealthy and sophisticated strain with ties to known families like LockBit.

Uncover the details of the sophisticated cyber campaign using the PXA Stealer malware to target government and educational sectors.

Learn about the dangerous malware known as Glove Stealer and its tactics of stealing sensitive data through social engineering.