
 Do Son
Learn about the stealthy keylogger malware used by the North Korean APT group Andariel to infiltrate and harvest sensitive information from U.S. organizations.
Malware

Discover the emergence of ToxicPanda, a sophisticated Android malware targeting financial institutions in Europe and Latin America.

Protect yourself from Stealc, a powerful infostealer malware. Learn how it targets systems and collects sensitive information, and take action to secure your data.

Discover how Kernel Callback Tables can be manipulated for process injection on Windows systems. Learn about the stealthy method employed by high-profile threat actors.

Discover Pygmy Goat, a new malware threat targeting network devices. Find out how it evades detection and captures sensitive data.

Discover the tactics used by threat actors to deploy ransomware with GOOTLOADER. Find out how they trick victims into downloading the malicious JavaScript file.

Protect your banking credentials and sensitive information from the advanced Android Trojan, HookBot. Stay updated on the latest cyber threats.

Stay informed about the Strela Stealer phishing campaign targeting Europe. Learn how this sophisticated malware steals sensitive data from compromised systems.
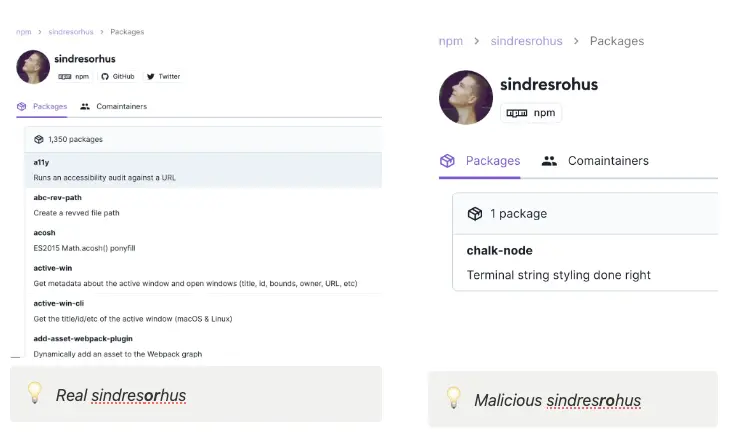
Beware of the latest npm threat! Learn how a malicious package called 'chalk-node' is posing as a popular library to steal sensitive data.

Discover the latest threat from the Bitter Group: MiyaRat, a new Trojan targeting South Asian entities with diverse attack methods.

Find out how an attacker used an EDR evasion tool to bypass security defenses and the important discovery that followed.

Beware of a new Facebook phishing campaign in Taiwan targeting business account users. Learn how to protect yourself from this malware-ridden scam.

Beware of a new typosquatting campaign targeting developers using open-source packages like Puppeteer. Learn how to protect yourself from malicious packages

Find out about the SYS01 Infostealer campaign: a sophisticated malvertising attack using social media ads to distribute a powerful malware tool.

Uncover the latest cyber threat: LUNAR SPIDER. Learn about their tactics and the adoption of Brute Ratel C4 in their malvertising campaigns.

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

Beware of the CryptoAITools malware campaign targeting cryptocurrency users. Learn how this sophisticated attack steals data and drains wallets.
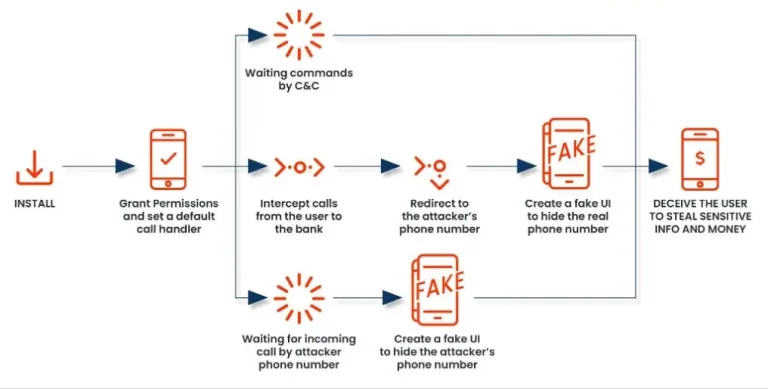
New FakeCall malware variant alert! Stay informed about this vishing threat that disguises as a banking app to target mobile banking users through fraudulent phone calls.

Discover the alarming collaboration between North Korean hackers and ransomware gangs. Learn how Jumpy Pisces is involved in a Play ransomware attack.

Stay informed about the recent lottie-player supply chain attack. Learn how malicious actors targeted the JavaScript library and the potential risks involved.

Discover Operation Magnus, the collaborative effort to dismantle RedLine and META, infostealers targeting millions of computers worldwide.

Learn about Interlock, a new ransomware group targeting both Windows and FreeBSD operating systems, and the concerning trend it represents.