
 Do Son
Uncover the sophisticated cyberespionage toolset CloudScout used by the APT group Evasive Panda to infiltrate networks and exfiltrate data from popular cloud services.
Malware

Discover the intensified threat to iOS users posed by the advanced LightSpy iOS spyware. Stay updated on its capabilities and target vulnerabilities.

Learn about the PySilon RAT, a malware variant that exploits Discord Bots to infiltrate systems and collect confidential information.

CYFIRMA has recently exposed a trio of malicious stealers—Divulge, Dedsec, and Duck Stealer—highlighting their proliferation

Uncover the UNC5812 Russian espionage campaign targeting Ukrainian military recruits. Learn how malware and strategic misinformation are used to undermine mobilization efforts.

Iqlusion's controversial Liquid Staking Module in Cosmos Hub: potential vulnerabilities and involvement of specialists from North Korea.

New report reveals TeamTNT's large-scale campaign targeting exposed Docker environments. Learn about the Docker Gatling Gun attack and the advanced Sliver malware.
Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes

Black Basta Ransomware Group Elevates Social Engineering with Microsoft Teams and Malicious QR Codes
Uncover the latest tactics of the Black Basta ransomware group targeting diverse sectors and geographies. Stay informed about the intensified social engineering campaign.

Discover SolarSys, a dangerous Trojan framework that poses a serious threat to Brazilian banking customers. Stay informed and protect your online security.

Discover the Rekoobe backdoor: a new cybersecurity threat with ties to APT31. Learn how it uses encrypted files and customized protocols to avoid detection in open directories.

Uncover the malicious activities of the Tenacious Pungsan group. Learn how they target developers through name-squatting attacks on popular npm packages.

Discover the concerning collaboration between Scattered Spider and RansomHub, resulting in a dangerous escalation of ransomware activities.

Learn about Embargo, a rising ransomware group targeting US companies. Discover their sophisticated techniques and the use of Rust programming language for versatile attacks.

Explore WarmCookie, a highly adaptive malware family that targets organizations across sectors. Learn about its range of functionalities and infection methods.

Get insights into the global reach of Grandoreiro banking trojan. Discover how this potent malware is targeting 1,700 banks and 276 cryptocurrency wallets, posing a threat to financial institutions worldwide.

Learn about a critical vulnerability in Secure Email Gateways and Antivirus scanners. Find out how to protect your organization from malicious VHD files.

Discover how cybercriminals use gRPC over h2c to deploy SRBMiner on Docker servers and mine XRP cryptocurrency.

Discover the cyberattack campaign targeting Docker Remote API servers and the deployment of the perfctl malware.
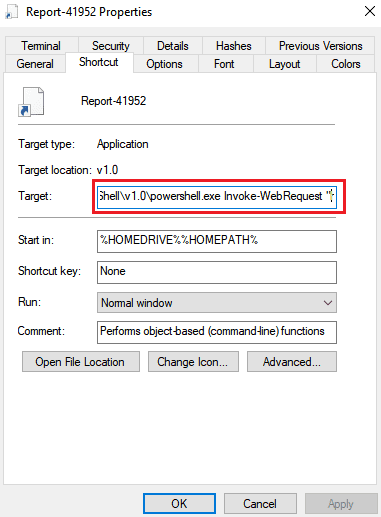
Explore the Bumblebee loader and its role in cybercrime. Learn about its new infection chain and the risks it poses to organizations.

Discover the latest tactics of the Akira ransomware group and how they have evolved to target both Windows and Linux hosts.
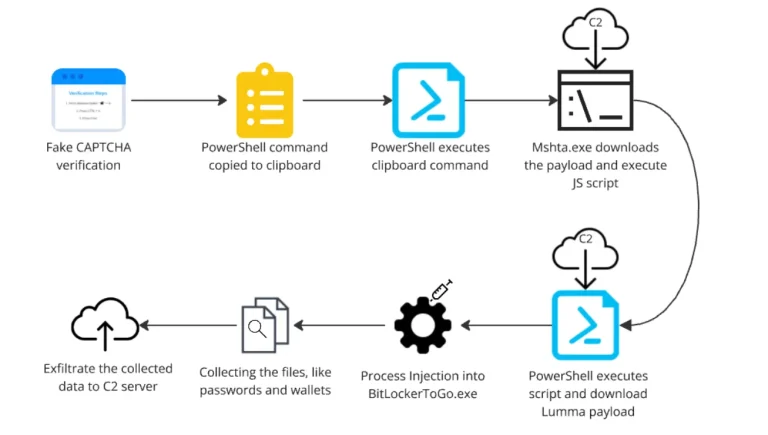
Explore the advanced delivery techniques and deceptive tactics employed by Lumma Stealer, an insidious information-stealing malware.

Uncover the latest tactics of GHOSTPULSE malware: discover how this evolving threat hides its payload within pixel structures.