
 Do Son
Symantec's Threat Hunter Team unveils the persistence of Stonefly, a North Korean cyberespionage group, in targeting U.S. organizations despite recent indictments.
Malware

Learn about a new attack vector exploiting vulnerabilities in CUPS. Find out how printers can be used to launch large-scale DDoS attacks.

Uncover the intricate cyber threat of GobRAT and Bulbature targeting edge devices worldwide. Learn how these malware variants have caused chaos in critical networks.
Learn how the United Kingdom is taking action against Evil Corp, a notorious cybercrime group linked to the Russian state and other ransomware groups.

Uncover the advanced cyberattack that exploits Visual Studio Code for unauthorized remote access. Stay informed and safeguard your systems.

Protect yourself from Skuld Stealer & Blank Grabber: two dangerous malware that exploits Roblox players using cheats and mods for an unfair advantage

Discover the latest evasive techniques and capabilities of XWorm, a sophisticated and multifaceted malware identified in 2022.
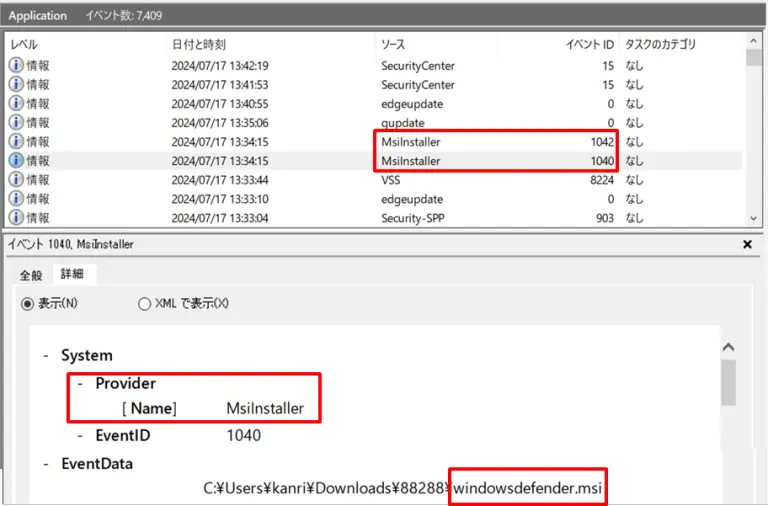
Discover how Windows Event Logs can be a powerful tool in the fight against human-operated ransomware. Learn how to detect and mitigate these evolving threats.

Stay informed about the evolving tactics of the 8220 Gang. Read about the new K4Spreader & Hadooken malware that targets cloud environments for cryptomining.

Discover the powerful new features of Rhadamanthys Stealer version 0.7.0: weaponized AI and OCR technology for advanced data theft.

Beware of cybercriminals using the League of Legends World Championship to distribute malware. Discover how scammers are tricking fans with deceptive ads.

Learn about the advanced tactics of the Patchwork APT group with their recent use of the Nexe backdoor in a cyber-espionage campaign.

Uncover the latest cyber-espionage activities of Sparkling Pisces, a notorious North Korean APT group. Learn about their evolving capabilities and targeted sectors.

Protect yourself from advanced malware threats. Understand the techniques employed by BBTok banking trojan in its complex infection chain.

Stay informed about the activities of Storm-0501, a financially driven cybercriminal group targeting organizations with hybrid cloud setups.

Learn about the first observed use of HTML smuggling by DCRat, a powerful remote access trojan. Find out how this technique allows cybercriminals to deploy malware undetected.

Stay informed about the Flax Typhoon botnet cyberattack campaign and how it poses a significant risk to global critical infrastructure.

Discover Octo2, the advanced variant of the ExobotCompact malware family, with enhanced capabilities and sophisticated techniques.

Stay informed about the new RomCom variant, SnipBot. Understand how it infiltrates networks and the industries it targets.

Discover the new malware campaign targeting Docker and Kubernetes environments. Learn how attackers exploit vulnerabilities to deploy cryptocurrency miners.

Discover the latest threat in cybersecurity: Mallox Linux 1.0. Learn how a group associated with the Mallox campaign is targeting Linux systems with modified Kryptina ransomware.

Learn about the latest threat to cybersecurity: infostealers that can bypass Chrome's App-Bound Encryption and compromise user data privacy.