 Do Son
Take immediate action to protect your Windows system. Learn about the new actively exploited vulnerabilities and how to safeguard your data.
Malware

Discover the new attack method used by cybercriminals: StealC malware. Learn how this malicious software steals user credentials through web browsers.

Uncover the dangers of proxyjacking through misconfigured instances of Selenium Grid. Learn how cybercriminals exploit vulnerabilities to deploy malicious campaigns.

Discover the dangers of Hadooken, a new Linux malware targeting Oracle WebLogic servers. Find out how it spreads and the risks it poses to critical applications.

Kawasaki Motors Europe is recovering from a cyberattack. Learn about the company's security response and progress in restoring services after the incident.

Learn about the dangerous Ajina.Banker malware campaign targeting bank customers in Central Asia and beyond. Stay informed and protect your personal and financial data.

Beware of the Poseidon Stealer malware targeting macOS users. Discover how this sophisticated attack exploits the interest in artificial intelligence.

Discover the latest cyberespionage campaign targeting the Iraqi government, attributed to the APT34 group and featuring custom-built tools.
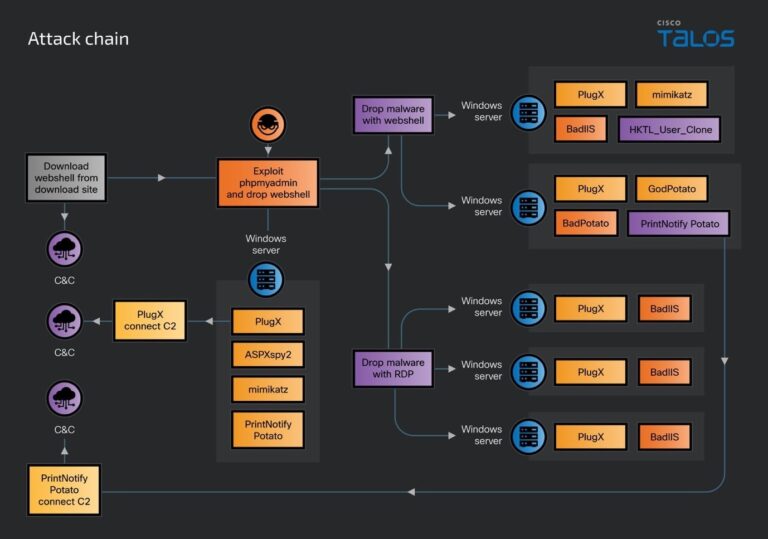
Learn about DragonRank, a Chinese threat actor specializing in SEO manipulation and cyberattacks. Find out how this group compromises websites and manipulates search engine rankings.

Discover the unique tactics of the Medusa Ransomware group. From their name-and-shame blog to their multi-platform presence, learn how they operate.

Explore the emergence of the Lynx ransomware group and their unconventional tactics. Uncover the motives behind their 'ethical' victim selection.

Uncover the new attack tactics of the RansomHub ransomware group. Find out how they exploit TDSSKiller and LaZagne to blind security teams and harvest valuable credentials.

Discover the concerning trend of cybercriminals leveraging legitimate Python libraries for malicious activities. Find out how these libraries are being exploited in malware scripts.

Get the latest insights on the Crimson Palace cyber espionage campaign, including the emergence of Cluster Charlie and the newly discovered keylogger 'TattleTale'.

Uncover the sophisticated fileless malware campaign delivering Remcos RAT. Learn how attackers exploit CVE-2017-0199 to infiltrate systems undetected.

Stay informed about the widespread Android.Vo1d malware infecting over 1.3 million Android TV boxes in 197 countries.

Discover the new variant of the notorious TrickMo banking trojan. Explore its evolved capabilities and the severe threats it poses to banking security and personal privacy.

Discover the latest developments in the activities of the threat actor known as CosmicBeetle and its new custom ransomware tool, ScRansom.

Stay informed about the sophisticated VMConnect cyber campaign targeting developers. Discover the tactics used by North Korea's Lazarus Group.

Learn about the rise of Repellent Scorpius, a ransomware group employing the Cicada3301 ransomware and a multi-extortion model.
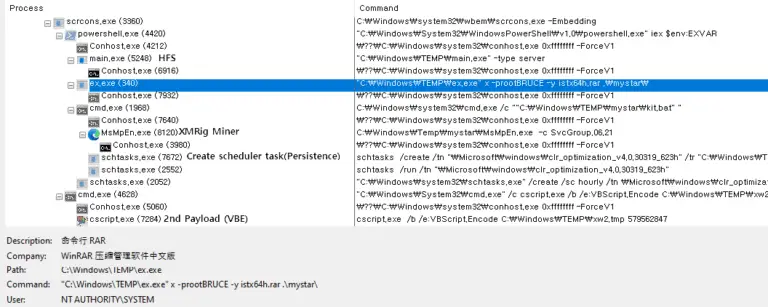
ASEC reveals the increasing sophistication of cybercriminals distributing XMRig malware through Binary Managed Object Files. Stay informed about this threat.

Discover the evolving tactics of Earth Preta, a notorious cyber espionage group, and their heightened threat to government entities in the APAC region.