
 Do Son
Uncover the evolving cyberwarfare tactics of Russian state-backed hackers. Find out how they exploit mobile devices for espionage and data theft.
Malware

Transport and logistics companies in North America targeted in a sophisticated cyberattack. Learn about the tactics used and how to protect your business.

Explore the sophisticated tactics of RansomHub ransomware and their use of EDRKillShifter. Discover how this tool enables them to evade detection and disable antivirus solutions.

Uncover the tactics of cybercriminals using a Go-based Injector and Lumma Stealer. Learn how they exploit vulnerabilities to access and exfiltrate valuable data.

Uncover the latest cyber threats targeting the European Union. From DDoS attacks to ransomware, gain insights into the challenges faced by the EU.
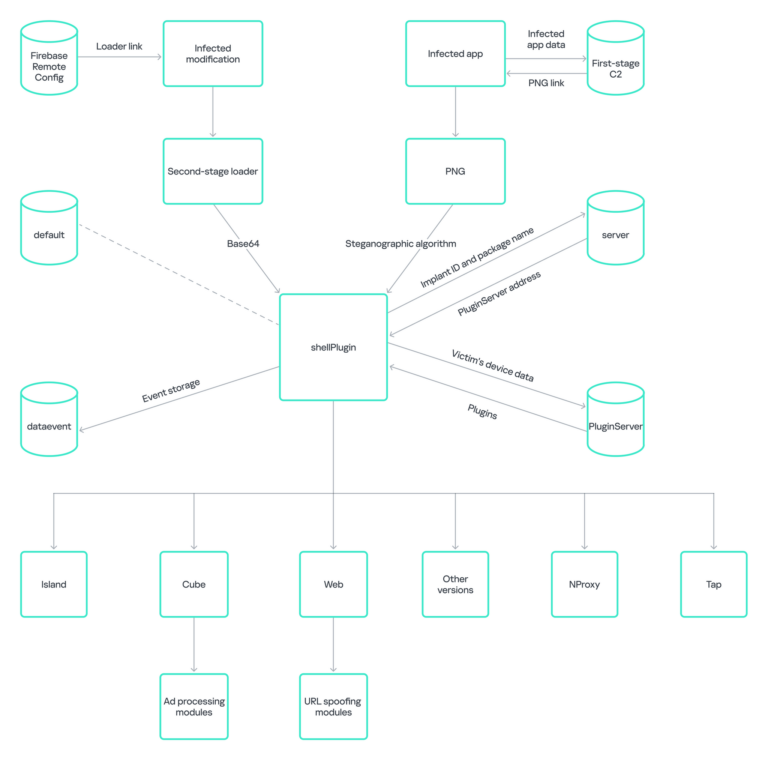
Stay informed about the latest Android threat: the Necro Trojan. Discover how this multi-stage malware is infecting millions of devices worldwide.
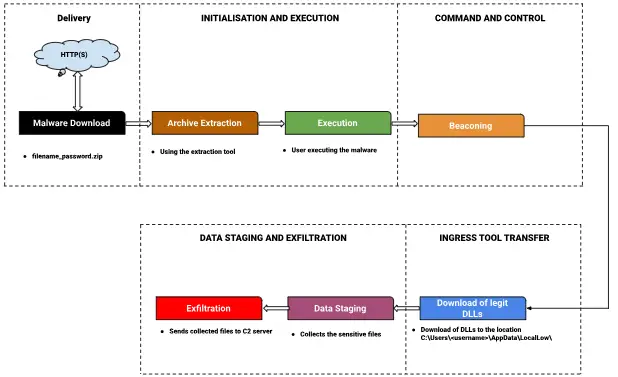
Learn about the dangerous RECORDSTEALER malware and its impact on user data. Stay informed and protect your sensitive information.

Get insights into UNC1860, a threat actor known for its ability to gain persistent access to high-priority networks in the Middle East.

Learn about Black Basta ransomware and its similarities to the infamous Conti group. Qualys report sheds light on their operational tactics.

Beware of the evolving threat of AsyncRAT malware disguised as cracked software. Learn how cybercriminals are using this sophisticated remote access trojan to infiltrate systems.

Learn about the aggressive campaigns and unique JavaScript scripts of MutantBedrog, a new malicious actor discovered by cybersecurity specialists.

Protect your systems from the Gleaming Pisces cyberattack campaign, which utilizes poisoned Python packages to deploy the backdoor, PondRAT.

Uncover the intricacies of the SambaSpy malware campaign that exclusively targeted Italian users. Explore the precision and customization of this RAT

Discover how cybercriminals exploited Fortinet FortiClient EMS, exposing critical vulnerabilities and utilizing a sophisticated attack chain.

Uncover the use of Azure Storage Explorer and AzCopy by ransomware groups for exfiltrating and storing data in Azure Blob cloud storage.

Learn about Earth Baxia's targeted cyber espionage campaign against government organizations in the APAC region, exploiting a critical GeoServer vulnerability.

Two malicious bash scripts downloaded and executed additional malware, later identified as the "Thiefbucket" malware, known in some circles as “Rustdoor.”

Stay informed about the latest cybersecurity threat: a botnet operated by cyber actors linked to the People's Republic of China, compromising thousands of devices worldwide.

Beware of counterfeit CAPTCHA tests! Learn how cybercriminals are using fake CAPTCHA challenges to distribute malware on Windows devices.

Uncover the cyber-espionage tactics of UNC2970 and their custom backdoor, MISTPEN, targeting senior-level employees in critical industries.

Uncover the latest credit card skimming technique targeting WooCommerce stores. Learn how malicious code disguised as an image file can steal customer data.
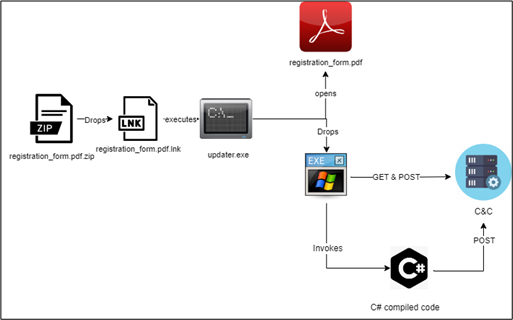
Unveiling a sophisticated cyberattack: Learn about the stealthy fileless malware targeting individuals associated with the US-Taiwan Defense Industry Conference.