
 Do Son
In a joint advisory, the Five Eyes intelligence alliance has warned of a widespread and ongoing cyberattack...
Malware

A new and more dangerous variant of the notorious Octo banking malware, dubbed “Octo2,” has been discovered...

Unit 42 has revealed a new variant of the notorious RomCom malware family, known as “SnipBot.” This...

Datadog Security Research has uncovered a new and widespread malware campaign targeting Docker and Kubernetes environments, where...

SentinelLabs has discovered that a group associated with the Mallox (TargetCompany) campaign is utilizing a newly modified...

In a concerning development for cybersecurity, developers of several notorious infostealers have announced that they have successfully...

Cybersecurity researcher BushidoToken’s latest report reveals a disturbing trend: Russian state-backed hackers are increasingly focusing on mobile...
Proofpoint researchers have uncovered a campaign targeting transport and logistics companies across North America. These attackers are...

In a recently uncovered report by Trend Micro, the notorious RansomHub ransomware group has been found to...

Recently, the eSentire Threat Response Unit (TRU) discovered a concerning new malware delivery chain involving a Go-based...

The European Union is grappling with an unprecedented wave of cyberattacks, according to the latest “ENISA Threat...
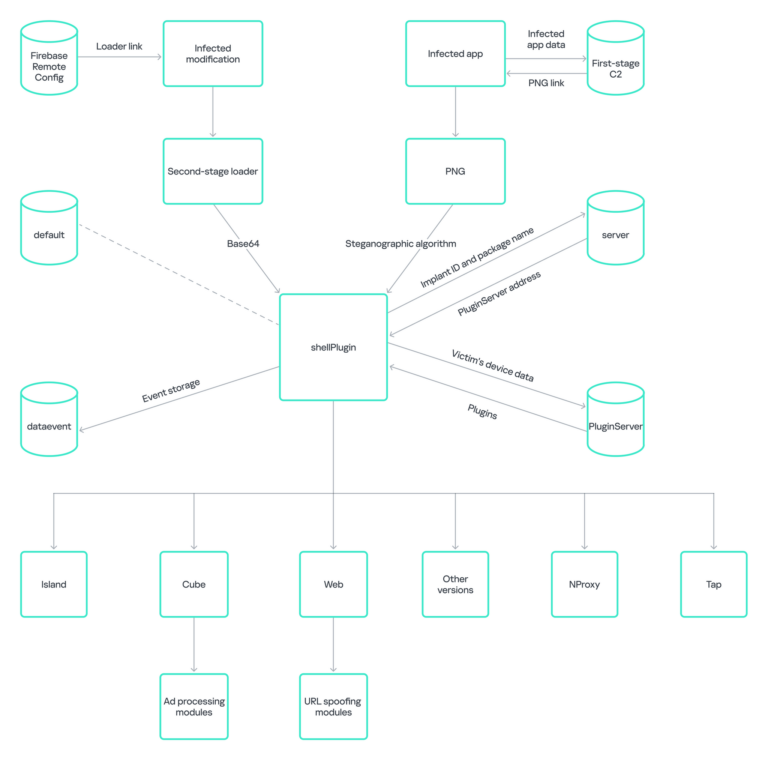
In a concerning development for Android users, Kaspersky Labs has uncovered a new version of the Necro...
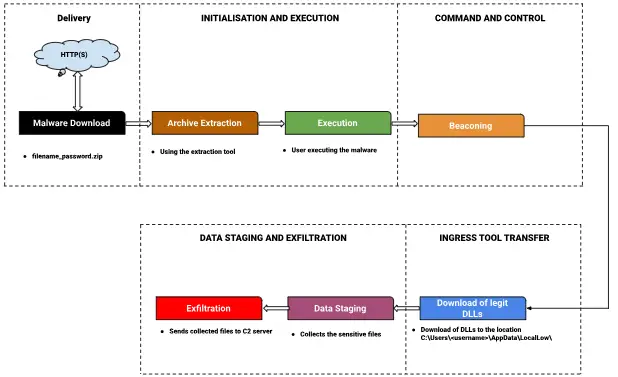
Google security researchers recently brought attention to the lingering impact of info-stealing malware. One such threat is...

Mandiant has uncovered alarming evidence of a sophisticated Iranian state-sponsored cyber campaign orchestrated by UNC1860, a threat...

Qualys has released a comprehensive report shedding light on the Black Basta ransomware, a highly disruptive threat...

In an alarming trend observed by McAfee Labs, cybercriminals have refined their tactics, luring unsuspecting users into...

In mid-2024, cybersecurity specialists from Confiant identified a new malicious actor known as MutantBedrog. This threat raised...

Unit 42 researchers have uncovered a new cyberattack campaign by the North Korean-affiliated APT group, Gleaming Pisces,...

In May 2024, Kaspersky Labs uncovered a sophisticated malware campaign exclusively targeting users in Italy. Unusual for...

In a concerning new development, cybersecurity researchers at Darktrace have unveiled a report detailing the exploitation of...

Security experts from modePUSH recently uncovered that ransomware groups such as BianLian and Rhysida are actively using...

In a recent report from Trend Micro, the cyber espionage group Earth Baxia has been identified targeting...