
 Do Son
Uncover the evolving Beast Ransomware, a popular RaaS platform actively targeting organizations. Explore its customizable options for Windows, Linux, and VMware ESXi servers.
Malware

Learn about Crypt Ghouls, a cybercriminal group behind ransomware attacks. Find out how they operate and how to defend against them.
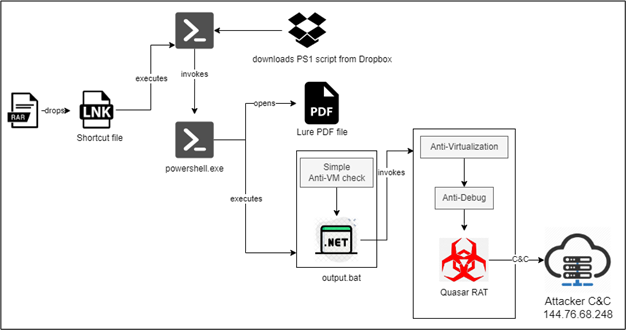
Discover the tactics used by a Vietnamese threat actor to target Meta Ads specialists with malware like Ducktail and Quasar RAT.

Learn about the sophisticated phishing campaign using a fraudulent NFT project to spread malware known as BeaverTail.

The rise of IcePeony: Explore the sophisticated tactics and geopolitical motivations of this China-nexus APT group

Beware of the new cybersecurity threat, ClickFix. Discover how cybercriminals are leveraging this dangerous tactic to deceive users and distribute malware.

Tavares highlights that between October 2024 and now, the team observed 5 million logs containing stolen credentials from 1,800 Telegram bots

Discover the latest cyber threat campaign: UAT-5647. Uncover the tactics, tools, and motivations behind this persistent group's targeted attacks.
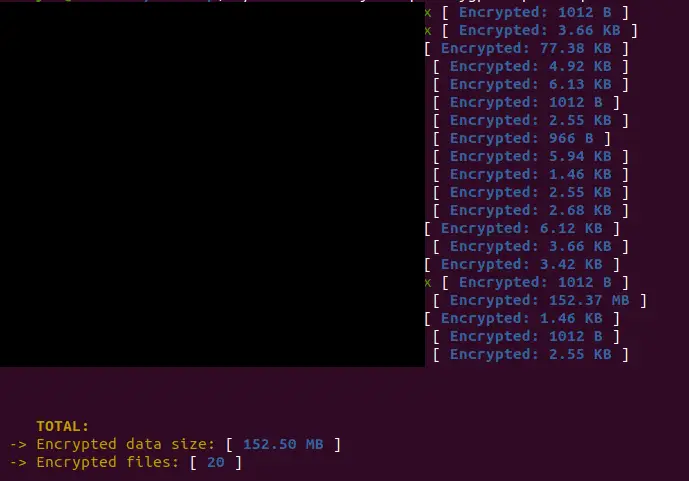
Explore the rise of Cicada3301, a notorious ransomware group targeting critical infrastructure. Discover their methods and impact on organizations.

Learn about the new malware crypter, HORUS Protector, and its potential impact on cybersecurity defenses. Stay informed and protect your systems.
Find out how cybercriminals are using a new loader called PhantomLoader to distribute the SSLoad malware undetected.

Discover the hidden threats of ransomware abusing AWS S3 infrastructure. Explore the tactics used by this sophisticated operation to steal sensitive data.

Discover the groundbreaking cybersecurity development known as ShadowLogic, a method for embedding undetectable backdoors in AI models.

Get insights into the SideWinder APT group's tactics and techniques. Learn about their global expansion and technical expertise in cyber espionage.

Stay informed about the latest cyber threat, ErrorFather. Read how this dangerous campaign utilizes the Cerberus Android Banking Trojan to target Android users.

Learn about the PipeMagic backdoor campaign targeting Saudi Arabia, using a deceptive ChatGPT application as the initial infection vector.

Uncover the latest Linux variant of FASTCash malware, used by North Korean state-sponsored hacking groups to target financial institutions.

Discover the Water Makara spear-phishing campaign targeting companies in Brazil. Find out how to identify and protect against this dangerous threat.

Uncover the hidden dangers of the TrickMo banking trojan. Learn about its evasion techniques and how it can access sensitive device information.
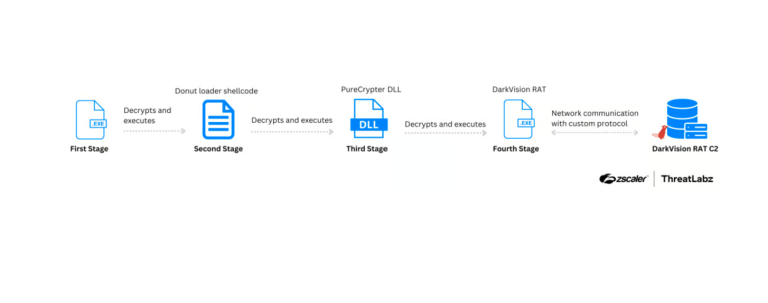
Uncover the details of DarkVision RAT, a low-cost remote access trojan (RAT) used by cybercriminals for unauthorized access and data theft.

Learn about the dangerous Lynx ransomware, a rebranding of INC ransomware. Find out how it threatens businesses and employs double extortion tactics.

Protect your enterprise from ransomware attacks exploiting Veeam Backup & Replication vulnerability. Patch and fortify your systems now!