
 Do Son
Xloader is known for its ability to steal sensitive information from web browsers, email clients, and FTP applications
Malware

Among the malware deployed in this campaign is a previously undocumented backdoor called TorNet, which is being distributed via PureCrypter malware

Discover the sophisticated operations of Lynx Ransomware-as-a-Service (RaaS) and its impact on businesses worldwide. Dive into the report by Group-IB.

A recent analysis by malware researcher Anurag uncovered a phishing campaign that spreads a fake SBI Bank Reward APK via WhatsApp messages

Discover the sophisticated LockBit ransomware operation leveraging Cobalt Strike beacons and proxy tools. Learn how it infiltrated systems and the impact it had.
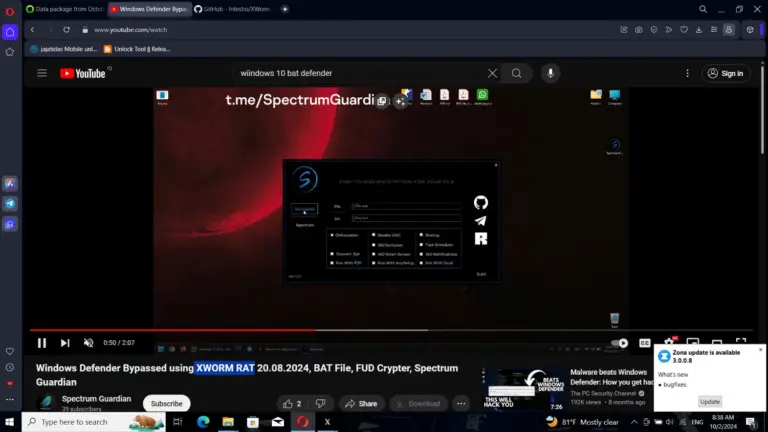
Beware of the XWorm Remote Access Trojan (RAT) builder attack. Discover how threat actors are targeting inexperienced cybersecurity enthusiasts with this malicious software.

Discover the rise of Akira, a highly active Ransomware-as-a-Service (RaaS) group targeting organizations worldwide.

Stay informed about the latest malware campaign leveraging the Lumma Stealer model. Learn how social engineering techniques are used to bypass traditional security defenses.

Learn about Lazarus Group's latest attack targeting cryptocurrency professionals. Discover how they weaponized a legitimate open-source project to steal sensitive information.

Learn about the recent campaign by Helldown ransomware group targeting Zyxel devices and the vulnerabilities exploited.

Learn about the J-Magic backdoor campaign targeting Juniper routers. Discover how attackers exploit vulnerabilities to gain long-term access and control.

Discover the latest threat in the ransomware landscape: HellCat ransomware. Learn about its origins, targets, and collaboration with Morpheus.

Discover BackConnect, the new strain of QBot malware that has resurfaced with enhanced capabilities. Learn how it adapts and what it means for cybersecurity.

Discover the latest evasion tactic used by cybercriminals: the ChaCha20 cipher in Lumma Stealer malware. Stay informed and protected against evolving threats.
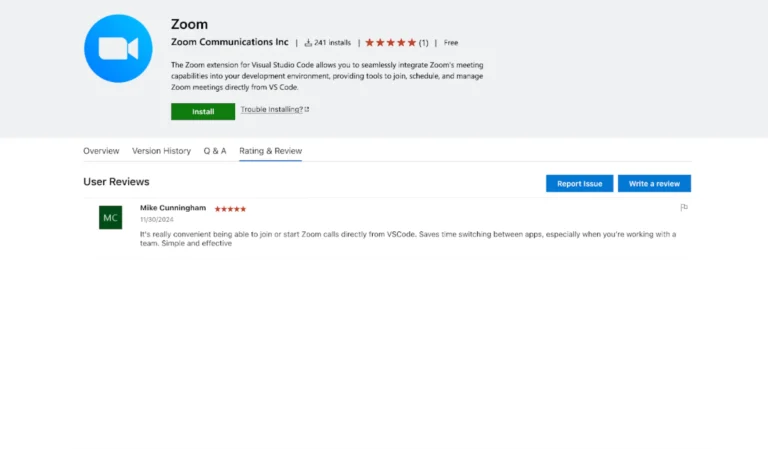
Beware of a malicious VS Code extension impersonating the Zoom Workspace tool. Learn how this deceptive extension targets software developers and steals sensitive data.

Uncover the alarming Android malware campaign attributed to the Indian APT group DONOT. Learn how this group targets individuals and organizations for strategic intelligence collection.

Unveiling Murdoc Botnet: A new variant of Mirai malware targeting AVTECH cameras and Huawei HG532 routers. Learn about the evolving tactics and sophistication of this expansive botnet campaign.

Stay informed about the latest tactics used in ESXi ransomware attacks. Learn how attackers exploit virtualized infrastructure components to disrupt operations.

Discover Purrglar, a potential new macOS stealer with alarming capabilities. Learn how it exfiltrates sensitive Chrome and Exodus wallet data.

Learn about the resurgence of DigitalPulse proxyware and its impact on Windows systems. Find out how attackers steal bandwidth for profit.

Uncover the dangerous world of botnets with the emergence of the AIRASHI botnet. Explore its relentless evolution and the 0-day vulnerability it exploits.
Learn about the ModiLoader malware distribution tactic: how it evades email security and targets victims through phishing emails.