
 Do Son
At a glance Actor: Suspected unknown threat cluster (tracked by Seqrite Lab) Activity Type: Spear-phishing, credential theft,...
News
At a Glance Malware family Edgecution (malicious Microsoft Edge extension plus a Python backdoor) Threat actor Initial...
The rapid development of generative artificial intelligence currently faces an unprecedented physical barrier. Specifically, a severe computing...

Google has just rolled out a genuinely useful addition to Google Wallet: package tracking. Thanks to deep...

TL;DR Attackers are exploiting a Cisco Unified CM RCE flaw in live attacks. Tracked as CVE-2026-20230, it...

TL;DR This weekly CVE report covers 1,909 new vulnerabilities published between June 22 and 28, 2026. Critical...
TL;DR Dell released urgent security updates for its thin client management platform. Two critical Dell Wyse vulnerabilities...
A critical Gemini CLI vulnerability (CVE-2026-12537) exposes developer workflows to maximum severity attacks. Google disclosed this CVSS...

A critical Hoppscotch mass assignment vulnerability threatens self-hosted API deployments. The flaw, tracked as CVE-2026-50160, allows unauthenticated...
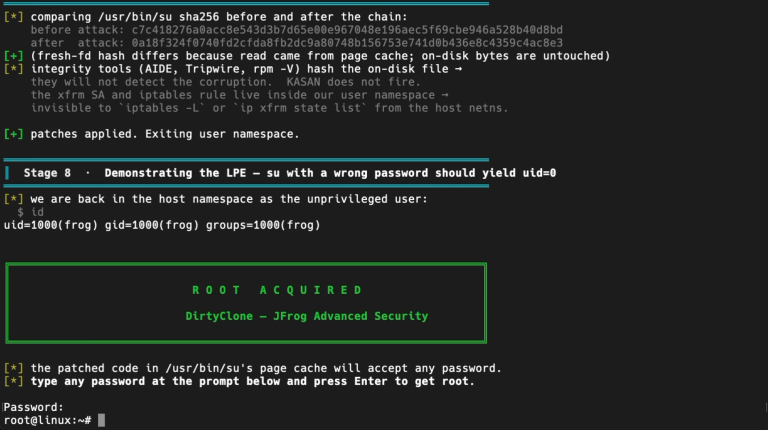
TL;DR DirtyClone is a Linux kernel privilege escalation flaw tracked as CVE-2026-43503. It scores 8.8 on the...

The evolution of generative AI technology is now officially intertwined with geopolitics and national security. Previewing GPT-5.6...

Anthropic recently suffered a complete network blackout under a stringent United States government ban. Fortunately, their formidable...
TL;DR Researchers publicly disclosed a libssh2 vulnerability tracked as CVE-2026-58050. The flaw lets a malicious SSH server...
TL;DR Security experts disclosed a high-severity flaw (CVE-2026-11940) in Python. A critical CPython tarfile vulnerability allows directory...

At a Glance Actor or Group: Unnamed digital piracy networks Activity Type: Copyright infringement Targets or Victims:...
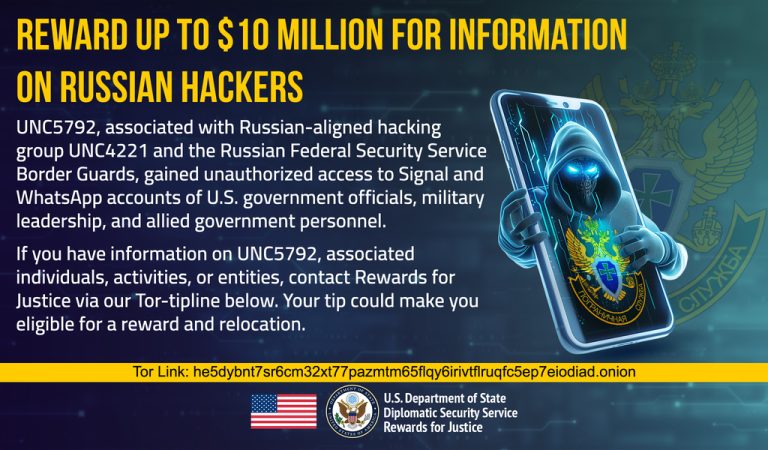
At a Glance Actor / group UNC5792 (linked to FSB Border Guards); UNC4221 (Russian military) Activity Phishing...
At a glance Malware Family: Backdoor.Mistic Threat Actor: Suspected Woodgnat (aka KongTuke) Target or Victims: Insurance, education,...
At least 39 rival malware families appear on a kill list used by a new Langflow cryptominer...
At a glance Actor: Unknown threat actor Activity Type: Privilege escalation and zero-day exploitation Targets: Service provider...

In a maneuver reminiscent of Mozilla Firefox’s legacy support strategy, Microsoft recently, and somewhat quietly, updated its...

At a glance Actor: Suspected Chinese-speaking threat actor (low confidence) Activity Type: Malware distribution and silent RMM...

At a glance Actor: Suspected cybercriminal networks (e.g., “Supplier Carl” and “Homborg Online Handel”) Activity Type: Fake...