 Do Son
Patch CVE-2026-110720 now. This 9.9 CVSS consul-k8s vulnerability enables a cross-namespace authorization bypass in ACL binding rules.
News
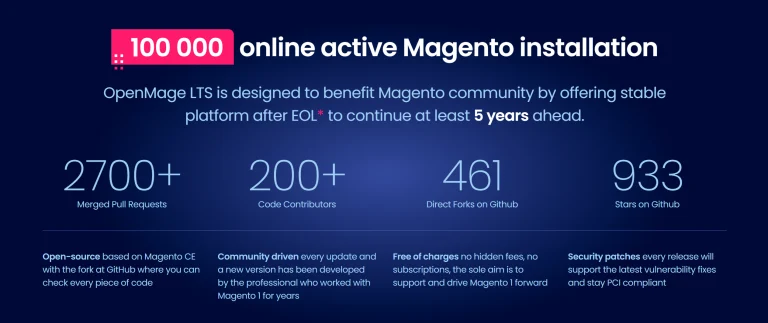
OpenMage fixes 34 OpenMage vulnerabilities in Magento LTS, including a critical CSRF flaw that hands out API tokens. Upgrade to 20.19.0 or 20.18.2.
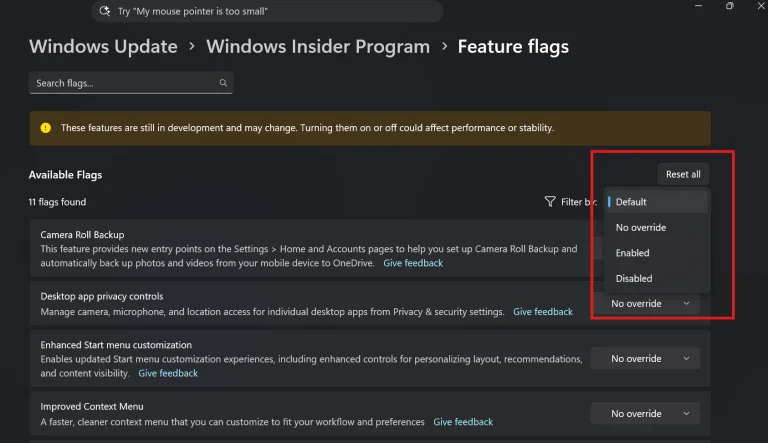
Microsoft tests an Intel APX Windows 11 performance toggle in preview builds, doubling general-purpose registers for enhanced processor speed.
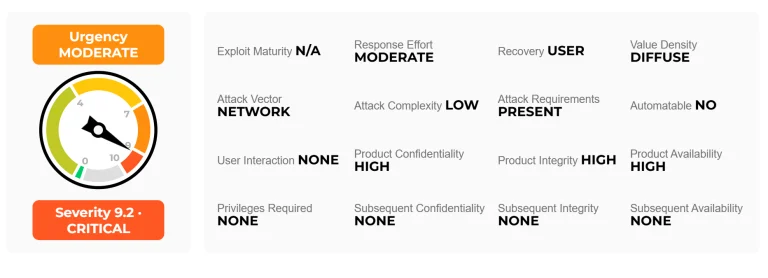
Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now.
Rapid7 disclosed 17 Zimbra Collaboration Suite flaws, including CVE-2026-10632 and CVE-2026-93640, allowing XSS and root privilege escalation.
Upgrade to Mautic 7.2.2 to fix critical Mautic vulnerabilities, including 9.9 CVSS RCE flaw CVE-2026-115188, CVE-2026-115189, and SQL injection bugs.
PoC and details are public for CVE-2026-84568, a macOS autofs vulnerability enabling root code execution, and a Gatekeeper bypass. Update macOS now.
A severe Tailscale SSH vulnerability allows attackers on authorized nodes to exploit Unix socket forwarding and escalate privileges to root access.
Apple blocks eMudhra certificates across macOS and iOS after weak intermediate keys compromised trust, with CLI tool bundles slated for future updates.
The Anthropic S-1 IPO filing reveals $16.8B Q3 revenue, $750B in compute commitments, and a historic valuation target on Nasdaq.
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
Apple deployed an in-box Apple Presto return scanner across retail stores to combat return fraud by running diagnostics on sealed iPhones.

Microsoft is testing a native Windows 11 speed test tool in preview builds, replacing web browser redirections with an integrated Ookla utility.
Mozilla launched the Come Back to Firefox campaign, leveraging nostalgic internet memes to promote user privacy and challenge Chrome market dominance.
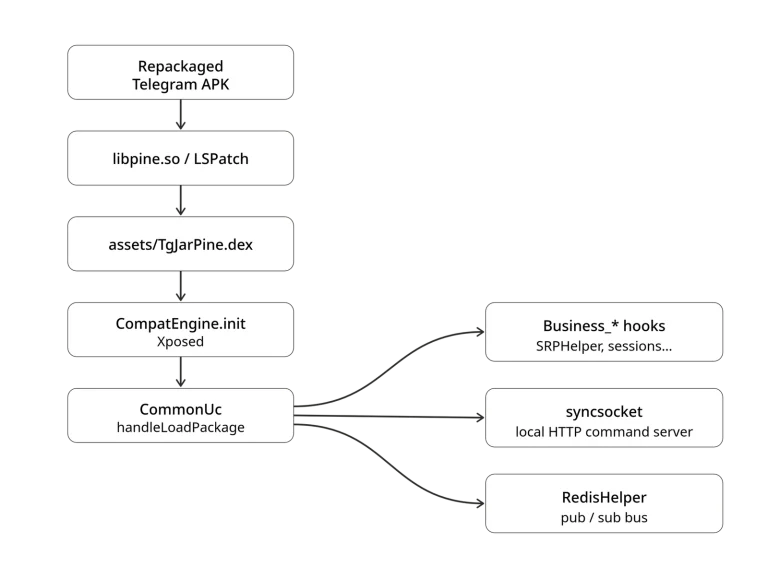
Researcher Ovi exposes uCreator Android spyware. The YingGai uCreator Android spyware platform uses VirtualApp and LSPatch to hijack 20 mobile apps.
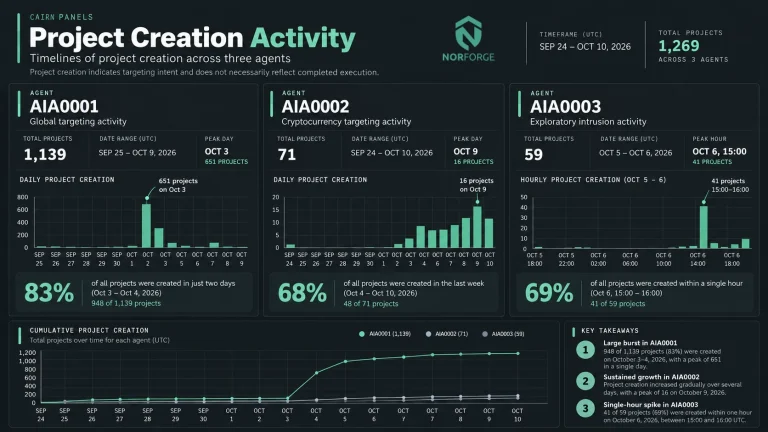
NorForge uncovered 20+ exposed Cairn AI panels showing how threat actors use the Cairn AI hacking tool to breach e-commerce and payment sites.
The OpenSSL 4.1.0 release introduces initial Elbrus e2k architecture support, DTLS 1.3 protocol capabilities, and post-quantum performance upgrades.
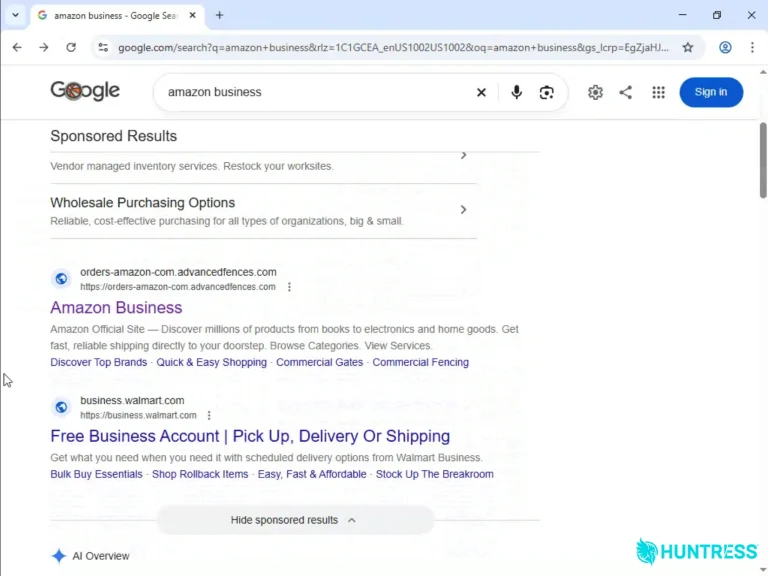
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
A devastating GMO Desktop Cloud breach compromised over 26,000 servers, exposing FX trading accounts and prompting a full infrastructure shutdown.
Security enthusiasts minted 106,000 eMudhra rogue certificates for Google domains after researchers uncovered trivial private keys in intermediate CAs.
A Keystone wallet data breach via Shopify API exposed customer shipping addresses, raising physical wrench attack concerns for crypto holders.
An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.