 Do Son
TL;DR The Apache Software Foundation disclosed eight CVEs on October 2, 2026, across three projects. The most...
News
Microsoft has shipped a V2 release of its September 2026 Exchange Server security updates. The only change...
TL;DR AWS published two security bulletins on October 2, 2026, covering four CVEs. Three hit Loom for...
TL;DR Digi International disclosed CVE-2026-75937, a critical Digi DAL OS vulnerability scored 9.4 on CVSS 4.0. One...
TL;DR Google pushed Chrome 154.0.8037.97/.98 to the Stable channel with 11 security fixes. The headline bug, CVE-2026-103628,...
TL;DR GitLab released AI Gateway versions 19.2.4, 19.3.2, and 19.4.1 to fix CVE-2026-90970. The GitLab AI Gateway...
TL;DR Citrix admins report NetScaler appliances rebooting repeatedly even after updating to build 14.1-73.37. Citrix now says...
TL;DR TP-Link published four security advisories on October 1, 2026, covering seven TP-Link vulnerabilities. The worst, CVE-2026-102369,...
TL;DR Moxa disclosed two Moxa MGate vulnerabilities on October 2, 2026. The worse flaw, CVE-2026-86325, scores 9.4...
TL;DR Full technical details and a proof-of-concept are now public for CVE-2026-85714, a CVSS 9.1 Stirling PDF...
For those closely monitoring the trajectory of artificial intelligence, OpenAI appears to be encountering profound difficulties in...
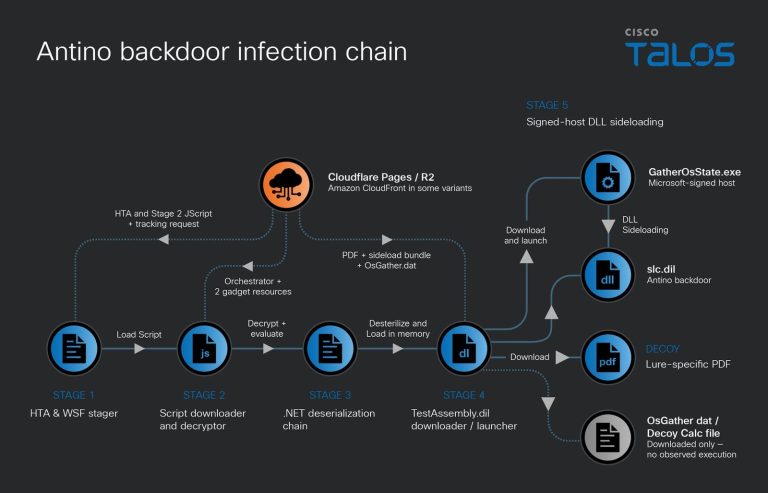
At a Glance Attribute Details Actor or Group UAT-11587 (suspected China-nexus group; overlaps with Jewelbug) Activity Type...
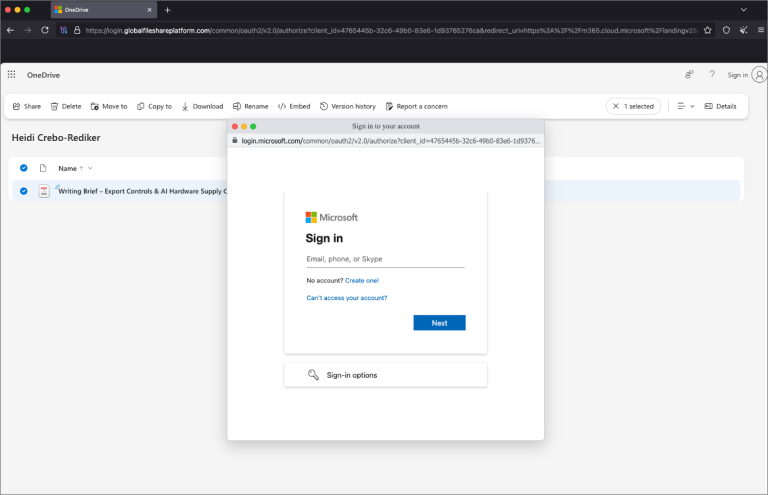
At a Glance Summary Attribute Details Actor or Group TA419 (China-aligned cyberespionage group) Activity Type Spear-phishing, AitM...
At a Glance Summary Attribute Details Actor or Group Unattributed cybercrime operators Activity Type Phishing, dual RMM...
TL;DR On October 1, Dell fixed five flaws in Dell System Update (DSU), led by a 9.6...

TL;DR Attackers chained two Zammad zero-day flaws to break into the Dutch Institute for Vulnerability Disclosure (DIVD)...
TL;DR A critical Capacitor vulnerability, CVE-2026-103922, scores 9.3 on CVSS and affects a framework with over 5.5...
TL;DR A Sharp printer vulnerability, now tracked as CVE-2024-58388, lets unauthenticated attackers read any file on the...
TL;DR On October 1, the Apache Software Foundation released Apache HTTP Server 2.4.69 with fixes for 20...
TL;DR Red Hat has disclosed a CVSS 9.9 Foreman RCE flaw that lets low-privileged users run commands...
TL;DR cPanel published security advisories addressing three critical cPanel security vulnerabilities across supported server platforms. Specifically, these...
TL;DR OpenBao maintainers issued security updates to address two critical flaws in the secrets management platform. These...