
 Do Son
Critical SonicWall flaw (CVE-2025-32818) in SSLVPN can crash firewalls, leading to DoS. Update your Gen7 devices now!
Vulnerability

CVE-2025-32965: A backdoor in xrpl.js SDK allows theft of crypto wallet keys. Users must upgrade and rotate compromised credentials immediately.

A critical vulnerability (CVE-2025-34028) in Commvault Command Center allows remote code execution. Patch immediately or isolate vulnerable instances.

Critical flaw CVE-2024-6235 in NetScaler Console lets attackers create admin accounts by abusing an internal API. Patch to version 14.1-25.53 now.

NVIDIA discloses 3 vulnerabilities in the NeMo Framework enabling remote code execution and data tampering. Update to version 25.02 to secure your AI development.

The Verizon 2025 DBIR reveals a surge in vulnerability exploitation and a doubling of third-party breaches. Learn key findings on ransomware, BYOD risks, and more.

Grafana fixes critical CVE-2025-3260 and two medium bugs, urging users to update immediately to prevent unauthorized access and XSS exploits.

SSL.com disclosed mis-issuance of digital certificates due to a DCV flaw. The "Email to DNS TXT Contact" method was incorrectly implemented.

Critical RCE vulnerability (CVE-2025-32433) in Erlang/OTP affects Cisco products. Unauthenticated attackers can execute code remotely. Patch now!

IBM's Hardware Management Console (HMC) has two privilege escalation vulnerabilities. Update to the latest fix to secure your Power Systems environment.

TP-Link WR841N routers are vulnerable to a stored XSS attack. Update firmware and change your password to protect your device from potential admin password theft.

Two critical CVEs in Yi IOT smart cameras allow unauthenticated RCE and root access via ports 6789 and 999, exposing users to full device compromise.

Zyxel releases patches for USG FLEX H firewalls to address critical vulnerabilities. Learn about the security flaws and how to protect your network.

Tenable Research discovered "ConfusedComposer," a GCP Composer vulnerability enabling privilege escalation. Learn how attackers could exploit Cloud Build permissions.
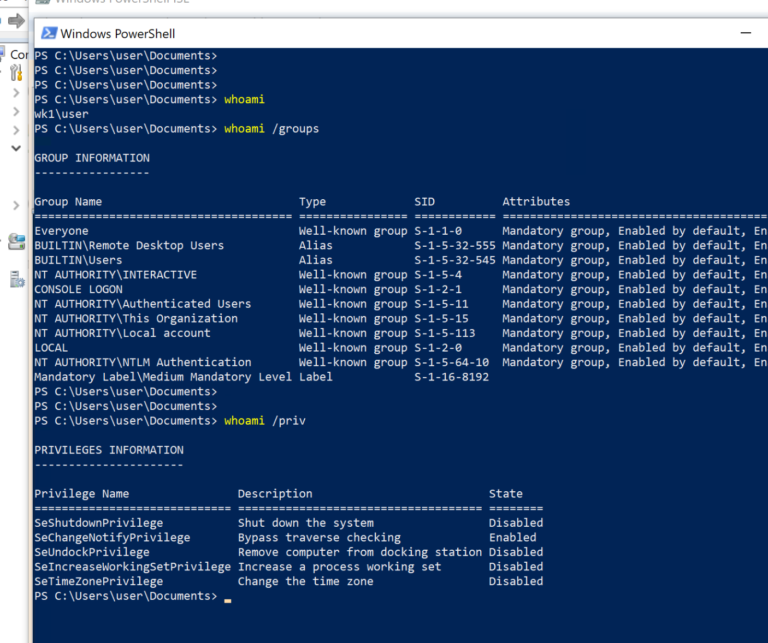
A critical flaw (CVE-2025-21204) in the Windows Update Stack allows local privilege escalation. Details and proof-of-concept exploit released.

A WinZip vulnerability (CVE-2025-33028) allows attackers to bypass Mark-of-the-Web (MotW) protection, enabling silent code execution via malicious archives.

A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.
CVE-2025-3616 in Greenshift plugin allows subscriber-level users to upload malicious files, enabling remote code execution on 50,000+ WordPress sites.

Cellebrite's Android zero-day exploit (CVE-2024-53104) used in alleged spyware attempt on activist. Details, technical analysis, and patch info.

CVE-2025-32434: Critical RCE vulnerability in PyTorch’s torch.load(weights_only=True) affects ≤2.5.1. Update to v2.6.0 to patch this major flaw

Yokogawa recorders have a critical vulnerability (CVE-2025-1863) due to insecure default settings. Attackers can manipulate data. Update security now!