
 Do Son
ASUS routers have a critical vulnerability (CVE-2025-2492) allowing unauthorized access. Update firmware and strengthen security now.
Vulnerability

Critical vulnerability (CVE-2025-42599) in Active! mail allows remote code execution. Update to the latest version immediately to protect your systems.
Critical RCE vulnerability (CVE-2025-24797) in Meshtastic allows remote takeover. Update to 2.6.2 immediately to stay safe.

GitHub patches CVE-2025-3509 and more in Enterprise Server. Flaws allow code execution, XSS, and data exposure. Admins urged to update immediately.

GCVE introduces a decentralized system for vulnerability IDs, empowering organizations with autonomy and speed. Complements CVE for smoother vulnerability management.
CISA warns of actively exploited vulnerabilities in Apple and Microsoft products. Urgent patching is required to mitigate risks from these attacks.

A critical vulnerability in Bubble.io allows attackers to bypass restrictions and extract all user data from Elasticsearch. The flaw remains unpatched.

PoC for CVE-2025-32433, a critical Erlang/OTP SSH flaw enabling unauthenticated RCE, has surfaced. Patch now to protect telecom and high-availability systems.

A vulnerability (CVE-2024-53141) in the Linux kernel's ipset component allows for privilege escalation and kernel-level code execution.
Hitachi Vantara addresses a critical resource injection vulnerability (CVE-2025-0756) in Pentaho Data Integration & Analytics, enabling RCE.

Siemens patches 66 SQL injection vulnerabilities in TeleControl Server Basic, urging users to upgrade and restrict access.
A critical vulnerability (CVE-2025-30911) in the RomethemeKit For Elementor WordPress plugin allows authenticated users to achieve RCE.

CVE-2025-32433 in Erlang/OTP SSH server enables unauthenticated RCE. Patch now to prevent full system compromise across all affected versions.

Cisco patches CVE-2025-20236, an RCE flaw in Webex App exploitable via crafted links. Users urged to update to avoid command execution risks.

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025

Apple releases urgent patches for zero-day flaws (CVE-2025-31200, CVE-2025-31201) targeting iPhones. Update now to protect your devices from sophisticated attacks.

CVE-2025-24054 exploited to leak NTLM hashes via .library-ms files with near-zero user interaction. Patch now to avoid exposure.

CISA extends funding for the CVE program, ensuring no disruption to global vulnerability tracking and cybersecurity infrastructure.

The CVE Foundation launches to ensure the future of the CVE Program after U.S. government funding ends for MITRE's operation.
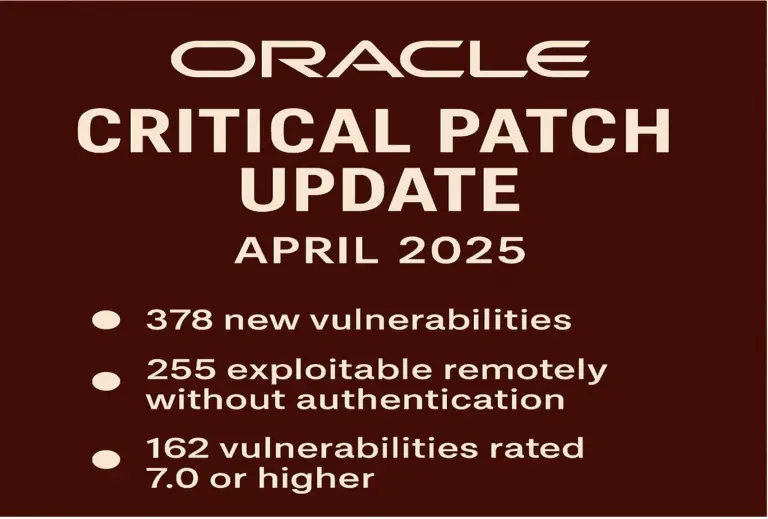
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

Google Chrome 135 fixes critical CVE-2025-3619 and high CVE-2025-3620 flaws. Users urged to update now to avoid potential code execution threats.
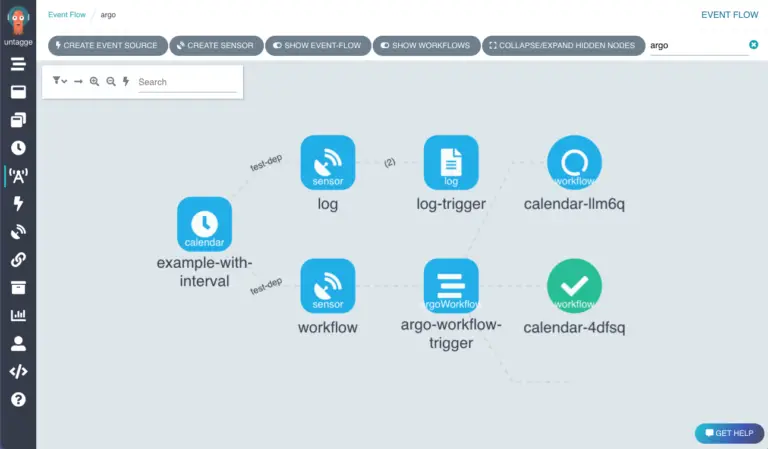
A critical vulnerability (CVE-2025-32445) in Argo Events allows users to gain privileged access to Kubernetes clusters. Upgrade to v1.9.6 to patch.