
 Do Son
MITRE warns the CVE program may halt after April 16 as U.S. funding expires, threatening global cybersecurity and vulnerability tracking.
Vulnerability

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.

iFAX Solutions discloses a critical remote code execution vulnerability (CVE-2025-1782) affecting HylaFAX and AvantFAX due to improper sanitization

PyPI resolved a security issue on April 14, 2025, where users retained team privileges after organization removal. The swift 2-hour fix prevented potential escalation.

CrushFTP vulnerabilities CVE-2025-32102 & CVE-2025-32103 enable SSRF and directory traversal. Update now to secure your file transfer server

Coinspect reveals flaws in browser wallets like Freighter and Coin98 that let attackers drain crypto without phishing, clicks, or wallet connection.
Apache Roller has a security vulnerability (CVE-2025-24859) where sessions aren't invalidated after password changes, risking unauthorized access

A Forescout report reveals critical vulnerabilities in solar power systems that could be exploited to destabilize power grids and compromise user data.

A China-nexus APT group exploited Ivanti Connect Secure VPN vulnerabilities to infiltrate organizations globally, deploying the SPAWNCHIMERA malware toolkit

Subdomain takeovers are evolving into a serious supply chain threat, allowing attackers to inject malicious content.

Fortinet warns of a novel persistence exploit using symbolic links in FortiGate SSL-VPNs. Upgrade to patched FortiOS versions to mitigate the threat.

CVE-2025-32428 flaw in Jupyter Remote Desktop Proxy exposes TigerVNC over the network. Patch to version 3.0.1 or switch to TurboVNC to mitigate.
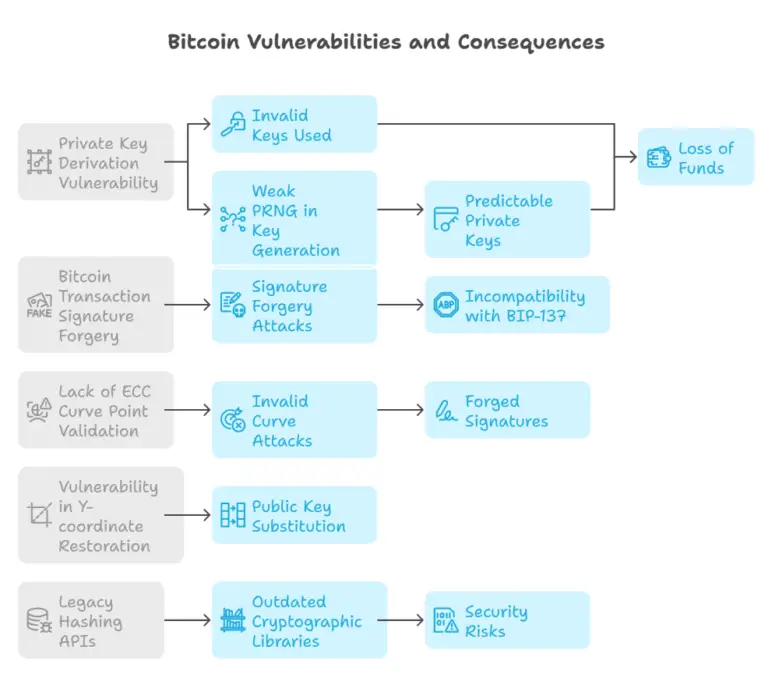
A critical vulnerability (CVE-2025-27840) in ESP32 microcontrollers threatens billions of IoT devices and the security of Bitcoin wallets. Exploits range from private key theft to forged transactions.

CVE-2024-58136: A security vulnerability in the Yii 2 PHP framework is being actively exploited. Learn about the risk and necessary updates.

Perl has a heap buffer overflow (CVE-2024-56406) vulnerability in the "tr" operator, potentially causing DoS. Update to Perl 5.40.2 or 5.38.4 to fix

CVE-2025-32896 in Apache SeaTunnel allows unauthenticated file read and RCE via REST API v1. Patch now by upgrading to version 2.3.11.

CVE-2024-0132: This report details how an incomplete NVIDIA Container Toolkit patch allows container escape and denial-of-service (DoS) attacks, affecting AI systems and Docker on Linux

A critical vulnerability in the Everest Forms WordPress plugin allows unauthenticated attackers to inject PHP Objects. Update to version 3.1.2 immediately to protect your site.

A critical vulnerability (CVE-2025-3248) in Langflow allows unauthenticated remote attackers to fully compromise servers. Users are urged to upgrade to version 1.3.0 or restrict network access

A critical vulnerability in the InstaWP Connect WordPress plugin allows unauthenticated attackers to include and execute arbitrary files. Update to version 0.1.0.86 immediately.

Rapid7 reveals details of Ivanti zero-day CVE-2025-22457, a critical stack-based buffer overflow actively exploited by a China-linked group. Learn about the vulnerability and available patches.

A vulnerability in Jenkins Docker images (CVE-2025-32754, CVE-2025-32755) allows SSH host key reuse, enabling attackers to intercept and modify build processes. Update to jenkins/ssh-agent 6.11.2 to mitigate.