
 Do Son
Discover SysBumps, the first successful KASLR break attack targeting macOS systems on Apple Silicon processors. Find out how vulnerabilities in speculative execution can compromise kernel memory.
Vulnerability

Discover the flaw in Windows BitLocker that allows attackers to bypass encryption and access sensitive data. No screwdrivers or hardware hacking required.

Take action to secure your ASUS router! Find out about the vulnerabilities (CVE-2024-12912 and CVE-2024-13062) and why it's crucial to update your firmware.

SafeBreach also released a PoC tool that tests a vulnerable Windows Server against CVE-2024-49112, available on their GitHub repository.

Stay informed about the critical vulnerabilities in WhatsUp Gold network monitoring software. CVE-2024-12108 allows complete server control through the public API.

Discover the new technique called Bad Likert Judge that can bypass the safety measures of Large Language Models (LLMs) and generate harmful content.

D-Link issues critical advisory for End-of-Life routers. Learn about the vulnerabilities exploited by botnets and the need for replacement.

Learn about the proof-of-concept (PoC) exploit for CVE-2024-21182 in Oracle WebLogic Server. Understand the risks and take action to secure your server.

Uncover the hidden vulnerabilities of the Network File System (NFS) protocol. Learn about the security risks and ways to protect your data.

Urgent warning: Exploited vulnerability in Palo Alto Networks PAN-OS firewall software (CVE-2024-3393) allows attackers to disable network security.

Discover the critical vulnerability in TrueNAS CORE (CVE-2024-11944) that enables remote code execution. Protect your devices now.

Discover the latest security vulnerability, CVE-2024-12987, affecting popular DrayTek gateway devices. Learn how it enables remote command execution and puts over 66,000 devices at risk.

A proof-of-concept (PoC) exploit for CVE-2023-4147 has been published on GitHub, increasing the urgency for patching.

Find out about the high-risk vulnerability (CVE-2024-56512) in Apache NiFi and take proactive measures to secure your sensitive data.

Discover the alarming Postman vulnerabilities exposed in a recent report. Learn how misconfigured access controls and poor data handling practices put sensitive information at risk.
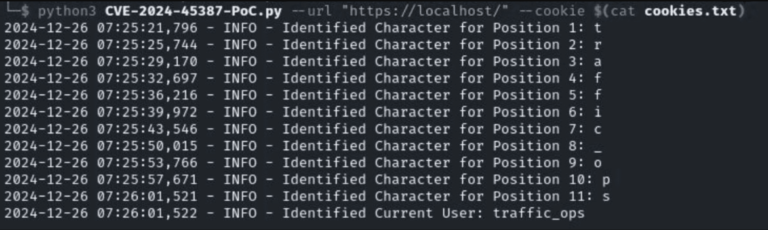
With a PoC exploit already circulating and a near-perfect CVSS score, CVE-2024-45387 is a significant threat to organizations using Apache Traffic Control

Vulnerability alert: Four-Faith routers vulnerable to CVE-2024-12856. Find out how attackers can exploit this flaw for RCE.

Discover the high-severity vulnerability CVE-2024-55950 in Tabby, a widely used terminal emulator for Windows, macOS, and Linux.

GStreamer vulnerability exposed: Learn about the 29 vulnerabilities discovered in the popular Linux multimedia framework.

Learn about the recent spike in botnet activity from FICORA and CAPSAICIN targeting D-Link devices and the vulnerabilities they exploit.
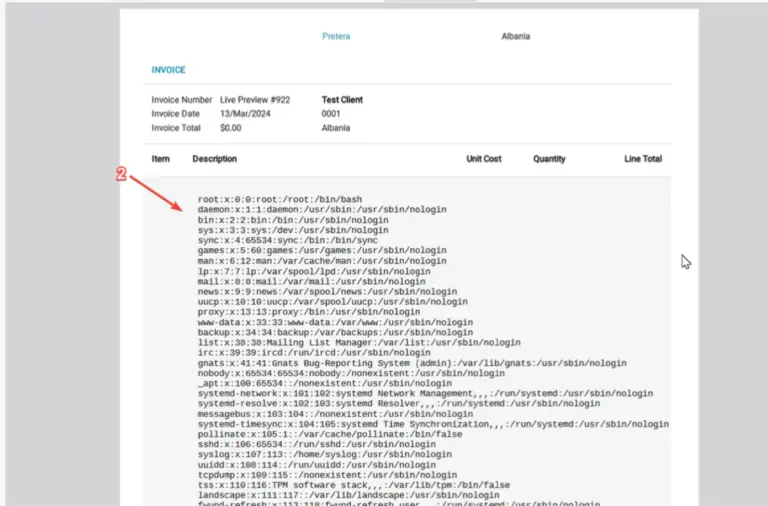
Discover the CVE-2024-53353 vulnerability in Invoice Ninja that could allow attackers to access sensitive files.
Critical vulnerability in Palo Alto Networks PAN-OS software: CVE-2024-3393 could disrupt firewall operations and force maintenance mode.