
 Do Son
Discover the severity of CVE-2024-52046 in Apache MINA. Take action now to protect your systems from potential code execution attacks.
Vulnerability
Protect your systems from CVE-2024-40896, a critical flaw in libxml2. Learn how to mitigate the risk and keep your sensitive data secure.

Learn about the urgent need to address the trio of SQL injection vulnerabilities (CVE-2024-12744, CVE-2024-12745, and CVE-2024-12746) in Amazon Redshift drivers.

Learn about the critical vulnerability CVE-2024-43441 affecting Apache HugeGraph-Server. Discover its potential impact on graph data security and ways to mitigate the risks.
Stay informed about the critical security flaw CVE-2024-45387 in Apache Traffic Control. Learn how this vulnerability could compromise data and disrupt services.

Stay informed about the recently discovered security vulnerabilities in Gogs. Explore the impacts of CVE-2024-39930 and other critical CVEs.
Learn about OilRig, also known as APT34 or Helix Kitten, and its sophisticated cyber espionage activities in the Middle East.

Learn about a recent study exposing vulnerabilities in WPA3 networks. Discover how social engineering and technical exploits can compromise Wi-Fi security.

Krueger is a Proof of Concept .NET post-exploitation tool for remotely killing Endpoint Detection and Response (EDR)

Learn about the stealthy operation of LITTLELAMB.WOOLTEA, a backdoor targeting Palo Alto Networks firewalls. Explore its entry point and persistent qualities.
Stay informed about the security flaw CVE-2024-23945 in Apache Hive and Apache Spark. Understand the impact and learn how to mitigate the risks.
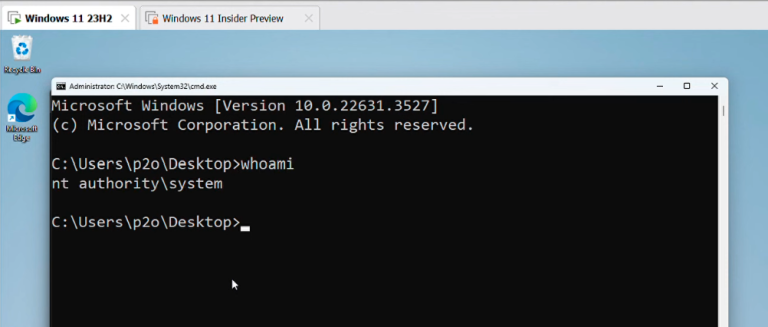
Researcher published the technical details and a PoC exploit code for CVE-2024-30085 - Windows Cloud Files Mini Filter Driver Elevation of Privilege Flaw

Discover the command injection flaw in Webmin (CVE-2024-12828) that allows attackers to execute arbitrary code with root privileges.

Learn about the severe command injection flaw (CVE-2024-56334) in Node.js system information package and its potential impact on RCE and privilege escalation.

Urgent security advisory: CVE-2024-53552 affects CrushFTP versions 10 and 11. Take immediate action to protect your accounts.

Urgent security update for Adobe ColdFusion: CVE-2024-53961. Take action now to safeguard your data from potential exploitation and file access.
Learn about the security flaw CVE-2021-44207 in Acclaim USAHERDS. Discover how attackers can exploit static encryption keys for remote code execution.
Find out about the critical CVE-2024-56337 vulnerability in Apache Tomcat. Learn how to mitigate the risk and protect your system.

Discover the details of the critical vulnerability (CVE-2024-56145) in Craft CMS that allows for unauthenticated remote code execution.

Discover the dangerous Hail Cock botnet and its target: the vulnerable DigiEver DS-2105 Pro DVRs. Learn how to safeguard your devices.

Learn about the severe vulnerabilities in IBM Cognos Analytics platform (CVE-2024-51466 and CVE-2024-40695) and how to mitigate the risks.

Protect your Rockwell Automation PowerMonitor 1000 devices from critical vulnerabilities CVE-2024-12371, CVE-2024-12372, and CVE-2024-12373. Learn how to secure your systems.