
 Do Son
A high-severity vulnerability (CVE-2024-38513) has been discovered in Fiber, a widely-used web framework for the Go programming language
Vulnerability

An attacker can first bypass authentication using CVE-2024-5716 and then leverage CVE-2024-5717 to execute arbitrary code

The OpenStack Foundation has issued an urgent security advisory, disclosing a critical vulnerability (CVE-2024-32498)

Security researchers from Graz University of Technology have unveiled a novel cybersecurity threat dubbed "SnailLoad" (CVE-2024-39920)
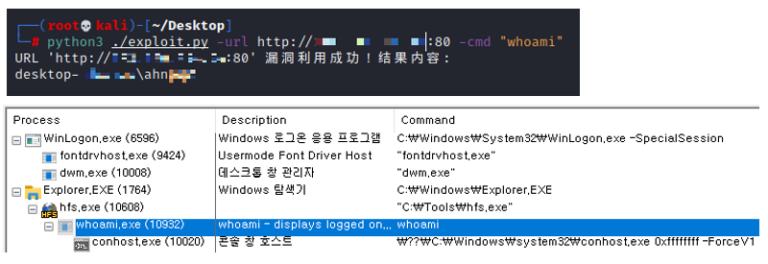
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

Adding to the urgency, security researcher carsonchan12345 has published a proof-of-concept (PoC) exploit code for CVE-2024-37726

SonarSource, a leading code security firm, has uncovered four unpatched vulnerabilities in Gogs, a popular open-source self-hosted Git service

CVE-2024-21586 (CVSSv4 8.7), allows unauthenticated attackers to remotely crash the Packet Forwarding Engine (PFE) and cause a DoS condition

A severe security flaw, CVE-2024-36401 (CVSS 9.8), has been discovered in GeoServer, a widely-used open-source software platform

Nearly three years after the notorious ProxyLogon and ProxyShell vulnerabilities caused widespread havoc on Microsoft Exchange servers
CVE-2024-6172 has been assigned a near-maximum CVSS score of 9.8, underscoring its critical nature & potential impact on the over 90,000 websites

Google released the July 2024 security patches for the Android operating system, which address several critical vulnerabilities

CVE-2024-38472 (Important): Server-Side Request Forgery (SSRF) vulnerability on Windows systems, potentially leaking sensitive NTML hashes

A security researcher has published a PoC exploit code targeting a high-severity CVE-2024-1085 vulnerability in the Linux kernel

McPhail has identified a critical vulnerability (CVE-2024-1724) in Snap, a popular package manager for Ubuntu and other Linux distributions
CVE-2024-3330 stems from insufficient input validation, allowing low-privileged attackers with read/write access to craft malicious Analyst files
CVE-2024-20399 has been discovered in Cisco NX-OS Software, the operating system powering a wide range of Cisco's networking devices

TRU has detailed a CVE-2024-6387 flaw, dubbed 'regreSSHion,' that leaves millions of Linux systems vulnerable to remote code execution

A security researcher has released PoC exploit code targeting a high-severity vulnerability (CVE-2024-0193) within the Linux kernel

The Document Foundation has issued an urgent security advisory regarding a critical flaw (CVE-2024-5261) in its LibreOfficeKit component

Dubbed "Indirector" attacks, exploit weaknesses in the chip's branch prediction mechanisms to precisely manipulate program execution flow

Water Sigbin employs various techniques, including creating scheduled tasks, adding exclusions to Windows Defender