Skip to content
September 16, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Celebrating 24 years of FreeDOS: Founder shares common FreeDOS commands
  • Technology

Celebrating 24 years of FreeDOS: Founder shares common FreeDOS commands

Do Son July 2, 2018 1 minute read
FreeDOS commands
Add Daily CyberSecurity as a preferred source on Google
In August 1981, Microsoft released MS-DOS 1.0. In 1994, Microsoft announced that the next version of Windows (Windows 95) would deprecate MS-DOS. In June of the same year, Jim Hall, a student, issued a declaration proposing to develop an open source alternative
Within a few weeks, several programmers including Pat Villani and Tim Norman joined the project, launched a new project called “FreeDOS”, and released the first alpha version in September.
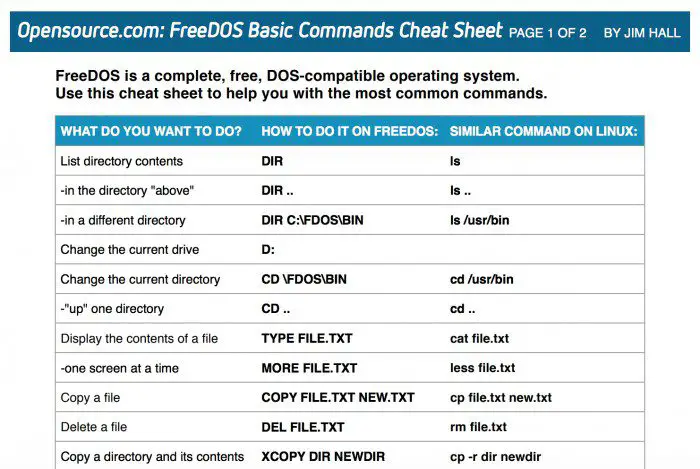
FreeDOS is a complete, free, and DOS-compatible operating system that runs older DOS games or commercial software, as well as embedded applications. After 24 years of FreeDOS, there is still an active developer community that is expected to remain strong.
To celebrate FreeDOS’s 24th birthday, Jim Hall recently created a handy FreeDOS command memo list, which includes some very common command descriptions and an introduction to DOS batch scripts.
You can download here.

Related coverage

  • Google updates ‘Ad Settings’ Allows Users to Control More Personal Data
  • Microsoft announces new AI-powered data types to Excel
  • Alphabet Q2 2026 Revenue Hits $119.8B as Pichai Confirms Gemini 4
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Stay Ahead of the Threat

Join security professionals receiving zero-hour CVE alerts, PoC updates, and threat analysis directly to their inbox.

No spam. One actionable email per week. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: FreeDOS commands

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-87886
    Exploitation of this vulnerability has been detected in the wild in limited, targeted attacks against Acronis Backup plugin...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-39364
    Vite is a frontend tooling framework for JavaScript. From 7.1.0 to before 7.3.2 and 8.0.5, on the Vite...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-27540CVSS 9.0
    Unrestricted Upload of File with Dangerous Type vulnerability in Rymera Web Co Pty Ltd. Woocommerce Wholesale Lead Capture...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-76461CVSS 9.8
    A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an...
    CISA KEV📅 Added to KEV: Sep 14, 2026
  • CVE-2026-51990
    A critical remote code execution vulnerability in Sogou Input Method, one of the most widely used Chinese-language input...
    Admin intel📅 Updated: Sep 12, 2026
Powered by CVE Watchtower

🔴 Live Critical Threats

  • CVE-2026-27565CVSS 9.8
    An unauthenticated remote attacker can upload a malicious IODD file that places...
  • CVE-2026-27546CVSS 9.8
    An unauthenticated remote attacker can exploit an authentication bypass in the _account_log...
  • CVE-2026-73447CVSS 9.1
    A privileged attacker can exploit certain operation to execute arbitrary commands with...
  • CVE-2026-12793CVSS 9.8
    The JetFormBuilder — Dynamic Blocks Form Builder plugin for WordPress is vulnerable...
  • CVE-2026-14349CVSS 9.8
    The TrueBooker – Appointment Booking and Scheduler System plugin for WordPress is...
  • CVE-2026-73807CVSS 9.8
    The mySCADA myPRO Manager command API does not properly enforce authentication for...
  • CVE-2026-81855CVSS 9.1
    A hardcoded cryptographic client authentication key vulnerability exists in the robot testing...
  • CVE-2026-78225CVSS 9.0
    A hardcoded cryptographic server key vulnerability exists in the deployer-ng Update Controller...
  • CVE-2026-61560CVSS 9.8
    `@zereight/mcp-gitlab` is a Model Context Protocol server for GitLab. Prior to version...
  • CVE-2026-73437CVSS 9.6
    On affected platforms running Arista EOS with Dynamic Host Configuration Protocol (DHCP)...
Powered by CVE WATCHTOWER

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.