Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Chrome and Firefox browsers will further reduce the use of memory
  • Technology

Chrome and Firefox browsers will further reduce the use of memory

Do Son July 30, 2018 2 minutes read
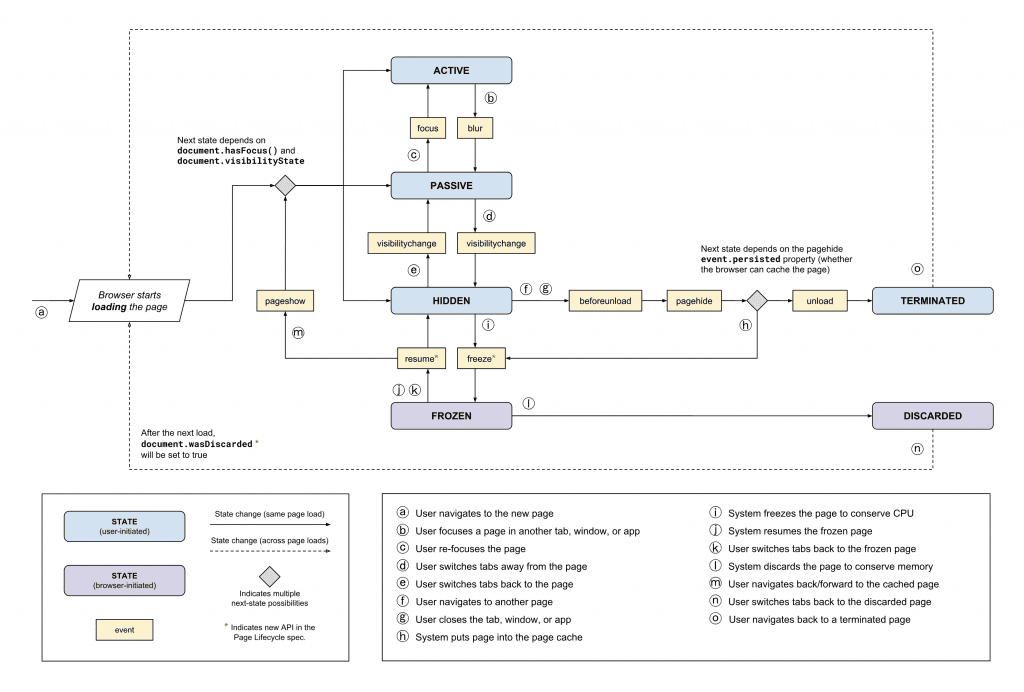
Page Lifecycle API
In a PC, running memory is still a scarce resource, and when the capacity is insufficient, it can cause the system to become significantly slower. As the most high-frequency application in daily use, browser vendors’ optimization in memory optimization is very worth looking forward. Chrome v68 began to introduce “Page Lifecycle API,” which can gracefully “freeze” inactive background pages, thereby saving system computing resources.

“ browsers today already do take active measures to conserve resources for pages in background tabs, and many browsers (especially Chrome) would like to do a lot more of this — to lessen their overall resource footprint.The problem is developers currently have no way to prepare for these types of system-initiated interventions or even know that they’re happening. This means browsers need to be conservative or risk breaking web pages.

The Page Lifecycle API attempts to solve this problem by:

  • Introducing and standardizing the concept of lifecycle states on the web.
  • Defining new, system-initiated states that allow browsers to limit the resources that can be consumed by hidden or inactive tabs.
  • Creating new APIs and events that allow web developers to respond to transitions to and from these new system-initiated states.”
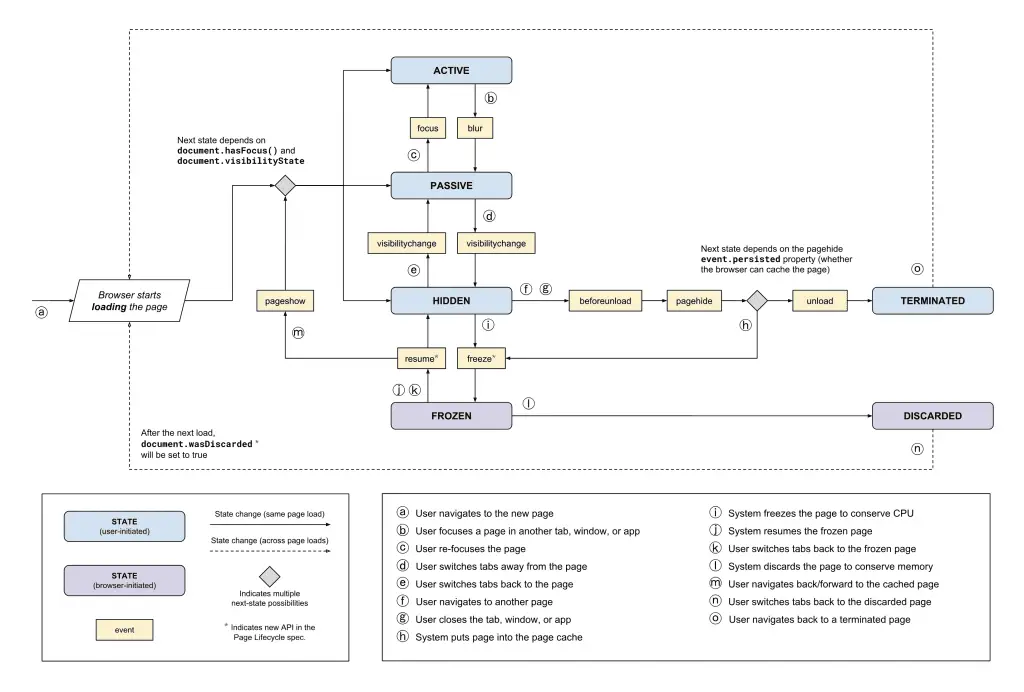
Image: developers.Google
At the same time, Firefox also built the “Fission MemShrink” project, which optimizes more than 100 processes for rendering web pages. The goal of each process is to save the 7MB of memory.

“The Fission MemShrink project is one of the most easily overlooked aspects of Project Fission (also known as Site Isolation), but is absolutely critical to its success. And will require a company- and community-wide effort effort to meet its goals.The problem is thus: In order for site isolation to work, we need to be able to run *at least* 100 content processes in an average Firefox session. Each of those processes has its own base memory overhead—memory we use just for creating the process, regardless of what’s running in it. In the post-Fission world, that overhead needs to be less than 10MB per process in order to keep the extra overhead from Fission below 1GB. Right now, on our best-cast platform, Windows 10, is somewhere between 17 and 21MB. Linux and OS-X hover between 25
and 35MB. In other words, between 2 and 3.5GB for an ordinary session.”

However, the implementation of the two new technical features is not a one-step process.
Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Let’s Encrypt Root gains the trust of all major root programs
  • Untethered Diagnostics: iOS 27 Introduces On-Device Recovery Mode
  • WannaCry-killer, Marcus Hutchins faces new charges
  • Cloudflare offers free Athenian protection services for election sites
  • The Command Line Coup: Why Google is Pivoting Project Mariner to Chase the Rise of AI Agents
  • AWS Bedrock Unleashed: 18 New AI Models, AgentCore Upgrades, and Enhanced Security
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Fission MemShrink Page Lifecycle API

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-83542CVSS 9.8
    Improper Control of Generation of Code ('Code Injection') in Apache OFBiz 24.09 before 24.09.08 on all platforms allows...
    📅 Updated: Nov 6, 2026
  • CVE-2026-82907CVSS 9.8
    Authentication Bypass by Capture-replay in ExternalLoginKeysManager in Apache OFBiz 24.09 before 24.09.08 on all platforms allows a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102894CVSS 9.1
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. From 0.7.1 until...
    📅 Updated: Nov 6, 2026
  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48751CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block`...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48750CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.