Skip to content
November 20, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • Facebook open source oomd: A new way to handle out-of-memory issues
  • Technology

Facebook open source oomd: A new way to handle out-of-memory issues

Do Son July 23, 2018 2 minutes read
OOMD

Recently, on Facebook’s website, the company’s Daniel Xu announced open source oomd under the GPLv2 license. oomd is userspace Out-Of-Memory (OOM) killer for Linux systems, which mentioned in a recent article on block I/O latency controllers. When there is not enough memory, the Out-Of-Memory killer will kill some processes; its primary task is to protect the kernel so that the application may be affected.

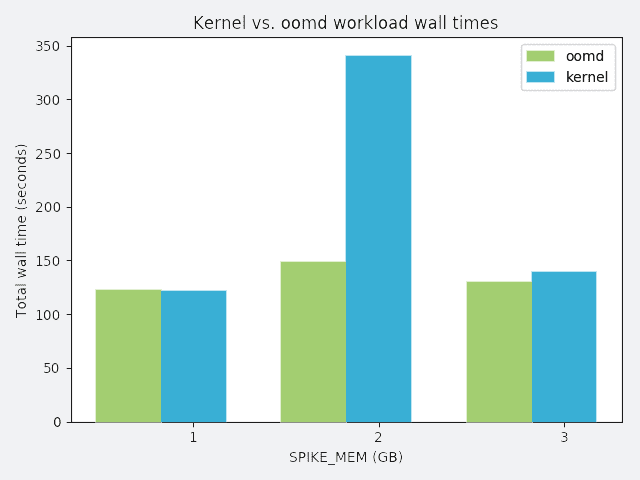
Compared to traditional Linux Out-Of-Memory killers, oomd comprehensively monitors the system to assess whether the system is under unrecoverable workloads. Before the system’s OOM Killer role, oomd takes corrective action in userspace.

Facebook says its infrastructure has evolved to include news streams, Messenger, Instagram, WhatsApp, Oculus and a host of other products. These products and the systems behind them run on millions of servers distributed across multiple geographically distributed data centres. As the scale of the infrastructure continues to expand, Facebook’s machines and networks are increasingly spanning numerous generations. A side effect of this multi-generation production environment is that new software versions or configuration changes may cause the system to function correctly on a single computer. An Out-Of-Memory (OOM) problem was encountered on another computer. Traditional Linux Out-Of-Memory killer in some cases works well, but in other cases, it starts too late, causing the system to enter the uncertain times of livelock.

So Facebook developed oomd, a faster, more reliable solution for common Out-Of-Memory (OOM) situations, which can run in user space rather than kernel space. The oomd designed by Facebook contains two key features: pre-OOM hooks and custom plugin systems. The pre-OOM hook provides visibility into OOM before the workload is threatened. Because OOM detection standards can vary by workload, plug-in systems support customisation of detection and process termination policies.

Source, Image: code.fb.com

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • eMudhra Certificate Revocation Extends to RSA Intermediate Keys
  • Cloudflare R2 Outage Explained: Accidental Shutdown
  • Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI
  • Airbnb CEO on AI: ‘Not the New Google’ But a Key to Customer Service
  • Qualcomm’s Bold Move: Intel Acquisition Bid Faces Antitrust Hurdle
  • Alphabet to Acquire Cybersecurity Powerhouse Wiz for $23 Billion
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Out-Of-Memory

🚨 Active Exploits in the Wild

  • CVE-2026-123890CVSS 9.8
    VMware vCenter contains an authentication bypass vulnerability in the VMware Directory Service. Affected versions: 9.1.x (fixed in 9.1.1.0200);...
    Watchtower Verified📅 Updated: Nov 19, 2026
  • CVE-2026-114938CVSS 8.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    Admin intel📅 Updated: Nov 19, 2026
  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-65094CVSS 9.0
    NVIDIA VIRTIO-Net for Bluefield contains a vulnerability in Virtio-Net where a VM user may cause a Write-What-Where condition...
    📅 Updated: Nov 20, 2026
  • CVE-2023-46846CVSS 9.3
    SQUID is vulnerable to HTTP request smuggling, caused by chunked decoder lenience, allows a remote attacker to perform...
    📅 Updated: Nov 20, 2026
  • CVE-2026-125273CVSS 9.6
    No replay or command-integrity protection. Commands lack sequence numbers, nonces, or session tokens; captured commands can be replayed,...
    📅 Updated: Nov 20, 2026
  • CVE-2026-96805CVSS 9.6
    The affected product has an unauthenticated command injection, which may allow an in-range BLE device to gain access...
    📅 Updated: Nov 20, 2026
  • CVE-2026-80188CVSS 9.8
    The BuddyBoss Addons plugin for WordPress is vulnerable to Authentication Bypass leading to Account Takeover in versions up...
    📅 Updated: Nov 20, 2026
  • CVE-2026-133528CVSS 9.3
    BeamNG.drive before 0.40.6 contains an out-of-bounds write vulnerability because JIT-compiled LuaJIT traces omit FFI array bounds checks, letting...
    📅 Updated: Nov 20, 2026
  • CVE-2026-77359CVSS 9.3
    Standalone `streamable-http` mode in `datalayer/jupyter-mcp-server` rejects forged `Host` and `Origin` headers on `/mcp`, but custom management routes mounted...
    📅 Updated: Nov 20, 2026
  • CVE-2026-68791CVSS 10.0
    Incorrect authorization in Azure Machine Learning allows an unauthorized attacker to disclose information over a network.
    📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.